❌

Lees weergave

v1.18.35

Core

Improvements

  • Added canonical redirects and JSON and Markdown data formats for agent-readable stats.

Bugfixes

  • xAI tool results now include supported images, while unsupported image formats are skipped. (@Jaaneek)

Thank you to 3 community contributors:

  • @dc85:
    • docs(web): add Fledge Alpha Free to Zen docs (#52895)
  • @jm0ney337:
    • docs(ecosystem): add opencode-supabase to ecosystem plugins (#49848)
  • @Jaaneek:
    • fix(opencode): bump @ai-sdk/xai to 3.0.139 so tool-result images reach xAI (#53549)

  •  

v4.4.0

This release adds built in traffic analytics for Traefik and Caddy, experimental support for SQLite as a database, readable container names with a configurable container prefix, third-party secret managers, Cloudflare DNS management, OpenID Connect sign-in, GitHub Actions runners on build servers, and Docker registry logins. It also includes many fixes.

Added

  • Traffic analytics for Traefik and Caddy using the new Rust version of sentinel (#11292)
    • Sentinel ingests the proxies JSON access logs and stores aggregate rollups only. Raw access logs are rotated on the server.
    • Per-server toggle on the new server Analytics page, off by default. Enabling it restarts the proxy and Sentinel. Optional MaxMind license key; GeoIP works without one.
    • Views: team dashboard widget, global Analytics page with server and application filters, per-server Analytics page, per-application and per-service Analytics tab.
    • Metrics: requests, bandwidth, unique visitors, and p95 latency KPIs with sparklines, requests chart, status-code breakdown, interactive globe with country breakdown, device, path, host, referrer, and browser breakdowns, optional live refresh for the 24h range.
    • Settings for top-N, sampling threshold, retention, and GeoIP. Nginx is out of scope.
    • Caddy applications and services need a redeploy after the toggle changes so their logging labels are updated. Caddy needs caddy-docker-proxy 2.9 or newer.
image image
  • SQLite database (#11992)
    • Add SQLite as a standalone database, based on a custom image (peakimages/sqlite).
    • Connect a SQLite database to an application or Docker Compose application on the same server in one click. Coolify mounts its data volume, protects connected volumes, and lets you unlink applications.
    • Back up and restore SQLite databases, including scheduled backups.
image
  • Container name prefix for generated names (#11704)

    • Optional prefix for the generated (rolling update) naming mode, set in the application's container settings or via custom_container_name_prefix in the API. It is slugified, limited to 30 characters, and unique per server. Rolling updates keep working compared to the custom container name (consistent mode) which loses rolling updates.
    before after
    single container app (prefix: shop-api) k9p2m4x7q1w3e5r6t8y0u2i4-20260908T141530 shop-api-20260908T141530
    compose service web (prefix: shop-api) web-k9p2m4x7q1w3e5r6t8y0u2i4-20260908T141530 web-shop-api-20260908T141530
  • Split action buttons (#11409)

    • Resource action menus show the primary action as a one-click button with secondary actions in a dropdown. This improves UX as the primary action is now only one click away, rather than two clicks and hidden inside a dropdown menu
  • Autofocus on auth forms (#11324)

  • Third-party secret managers (#11474)

    • Doppler, Infisical, and HashiCorp Vault as secret sources for applications, services, and standalone databases.
    • {{vault.KEY}} references are resolved during deployment and database start. Values are never stored in Coolify's database and are redacted from deployment logs.
    • Key browsing, bulk import as references, autocomplete, provider validation, and clear deployment errors for missing secrets. Build reuse is skipped when build-time secret references may have changed.
  • Team audit log (#11462, #11788)

    • Searchable, filterable log of UI, API, MCP, and webhook activity under Team β†’ Audit Log, covering resource changes, deployments, backups, proxy controls, membership, token, and integration changes, account security events, and server, application, service, and instance settings.
    • Entries show the previous and new value of each changed field under "View changes". Changes are encrypted at rest, and secrets, commands, and configuration content are left out.
    • Stores actor, resource, and request context with sensitive metadata redacted. Events are pruned after 90 days.
    • Team admins and owners can read events with GET /audit-events in the API.
  • Database import API (#11699)

    • Import backups into standalone and service databases from an upload, a server path, or S3 storage: POST /databases/{uuid}/imports/uploads, POST /databases/{uuid}/imports, GET /databases/{uuid}/imports/{activity_id}, and the same under /services/{uuid}/databases/{database_uuid}/imports.
    • Uploading and starting an import need the write permission. An import from a server path also needs deploy.
  • Cloudflare integration tokens (#11359)

  • Cloudflare DNS record management (#11699)

    • From the application and service Domains pages, Coolify matches hostnames to zones reachable with the team's Cloudflare tokens and creates records pointing at the server.
    • Detects records that already point elsewhere and offers a replace action, shows a "Managed by Coolify" badge, and deletes managed records with the domain after confirmation.
  • OpenID Connect single sign-on (#10543)

    • Sign in and register with any OIDC provider.
    • Registration policy per provider: allow or block password registration and user creation, optionally auto-join new users to the Root team.
    • Linked SSO identities are shown on the user profile. Provider-managed email addresses cannot be changed in Coolify.
    • Microsoft Entra ID: use https://login.microsoftonline.com/<tenant ID>/v2.0 as the issuer URL and add the optional ID token claims email and xms_edov to the app registration. xms_edov counts as a verified email.
  • Alpine Linux server support (#6189)

    • Add and update alpine based servers with apk.
  • Copy environment variable values (#11379)

    • Copy resolved values directly from the environment variables page. Shared variables and $SERVICE_* references resolve to their actual value, except references to locked shared variables. Locked variables have no copy button.
  • Named volumes (#7591)

    • New volume mounts use named Docker volumes instead of host source paths, including on Swarm. New volumes are pre-filled with a resource-based name.
    • Existing bind mounts keep their source paths, which are shown read-only.
  • Server roles for deployments and builds

    • Set a server to Deployments only, Builds only, or Deployments and builds in the server settings or via server_role in the API. The deprecated is_build_server field still works.
    • Deployments only servers never build images themselves, and applications on them need a Docker image name.
    • Choose per team whether builds fall back to the deployment server when no build server is usable.
  • GitHub Actions self-hosted runners (beta) (#12054)

    • Builds only servers can run GitHub Actions workflow jobs for an organization GitHub App. Each job gets a new runner container that is removed when the job ends.
    • Set labels, parallel runners, CPU and memory limits, the runner image, timeouts, and Docker in jobs (privileged Docker-in-Docker, Sysbox, or none) on the new server GitHub Runners page. The host Docker socket is never mounted.
    • Jobs started by pull requests are refused unless you allow them.
    • The server role cannot be changed while runners are enabled, and a server can be reserved for runners so it takes no application builds.
  • Docker registry logins (#12048)

    • The new Registries page and the Registries tab of each server list the registries a server is logged in to and the registries its applications need.
    • Log in, update, and log out with presets for Docker Hub, GHCR, GitLab, Google Artifact Registry, Azure ACR, and AWS ECR, or any other registry. Coolify runs docker login on the server and does not store the token.
    • API: GET /servers/{uuid}/registries, POST /servers/{uuid}/registries, POST /servers/{uuid}/registries/{registry}/check, and DELETE /servers/{uuid}/registries/{registry}.
  • Docker images page (#11689)

    • The new server Images page lists every image with its size, age, and the containers that use it, and shows the total and reclaimable disk space. Unused images can be deleted after typing their reference.
  • Traefik ACME certificates (#12015)

    • View and delete certificates stored in Traefik's acme.json on the new TLS Certificates page in the server's Proxy menu. Deleting does not revoke the certificate, and the server shows that the proxy needs a restart.
    • Coolify backs up acme.json before every change and keeps the last 10 backups, which can be restored or deleted on the same page.
  • Account deletion (#12088)

    • Delete your own account from the profile page. Teams where you are the only member are deleted, you are removed from all other teams, and your API tokens and sessions are revoked.
    • Deletion is blocked for the root user, while a team you own alone still has servers, projects, or Git sources, and while a shared team would be left without an admin or owner.
  • Preview deployments API

    • GET /applications/{uuid}/previews and GET /applications/{uuid}/previews/{pull_request_id} return preview deployments. POST /applications/{uuid}/previews opens or redeploys the preview of a pull request and needs the deploy permission.
  • Reopen the live deployment log (#11783)

    • Services, databases, and applications show a "Deploying… View log" indicator that reopens the running log. Deploy, Start, or Restart during a running operation reopens the log instead of failing.
  • Application settings filter (#11783)

    • Filter the application settings sidebar, including sub-pages such as Advanced β†’ Proxy.
  • Use variables such as ${NETWORK:-coolify} or ${COMPOSE_PROJECT_NAME}_default in Compose network names of applications and services, including a service's networks: list. A network name that is a single variable is added as an editable environment variable.

  • Delete a server from its cloud provider (Hetzner, Vultr, or DigitalOcean) through the API with delete_from_provider=true on DELETE /servers/{uuid}. (#12026)

  • Give additional users access to the Horizon dashboard with the HORIZON_ALLOWED_EMAILS environment variable (#9354)

  • Show pending team invitations on the dashboard.

  • Test S3 storages that were marked unusable again every hour, so they become usable on their own once the connection works.

  • Generate a random manual webhook secret with one click.

  • Show a warning icon on the server Proxy menu when the proxy is not running.

  • Link the Healthcheck row in the status summary of applications and databases to the healthcheck page.

  • Add a favicon, an Apple touch icon, and a web app manifest.

  • Add OAuth settings to auto-join new OAuth users to the root team and to disable password registration while OAuth is on. The login page then shows "Only OAuth registration is enabled."

  • Add a shared copy component which is used across resource (#11368)

Changed

  • Realtime runs on Laravel Reverb inside the Coolify container, next to the terminal server. The separate coolify-realtime (Soketi) container is no longer used; existing proxy routes and port settings keep working, and a soketi override in docker-compose.custom.yml is still accepted. (#10530, #11935)
  • Generated container names use an ISO 8601 timestamp suffix (<uuid>-20260908T141530) instead of HHMMSS plus microseconds (the old suffix is still recognized). (#11702)
  • Containers are labelled with coolify.applicationUuid, coolify.serviceUuid, coolify.service.subUuid, and coolify.databaseUuid instead of numeric ID labels. Existing containers keep working and get the new labels on the next deploy or restart.
  • Database restores: the import command is read-only, and single-database PostgreSQL restores no longer drop existing objects by default. The new "Replace objects that already exist" option (replace_existing in the API) restores the previous --clean behavior. PostgreSQL archive restores also skip owners and privileges unless "Keep owners and privileges" (keep_owners) is set. (#11699)
  • Database restores support PostgreSQL custom and tar archives, MongoDB archives and dump directories, and bz2, xz, and zip files. All-databases MySQL and MariaDB restores can restore users and privileges (restore_mysql_users), and SQLite restores can pick the target file (sqlite_database). The import form shows the exact restore script.
  • All OAuth providers are managed from one Settings β†’ Authentication page with provider icons and clearer login buttons. (#10543)
  • OAuth accounts link to a provider identity, not only to an email. The first OAuth login links the account. To link an existing account, the provider must verify the email, except for accounts without a password that an OAuth login made before this release. New accounts follow the registration settings.
  • Each account links to one OAuth provider. If you used two providers with the same email before, use the first one you sign in with after the upgrade.
  • If you rename a self-hosted GitLab, Authentik, Clerk, or Zitadel host, or change the Azure tenant, run php artisan oauth:rekey <provider> --from=<old URL or tenant> so linked accounts keep working.
  • Authentik 2025.10 and later: to link an existing Coolify account to Authentik, the email scope must return email_verified: true. Add a scope mapping in Authentik under Customization β†’ Property Mappings that returns {"email": request.user.email, "email_verified": True}, and use it on the provider instead of the default email mapping.
  • OAuth logins ask for the 2FA code if 2FA is on, and SSO users can turn on 2FA without a password.
  • Users with a linked OAuth identity confirm destructive actions with the typed confirmation only, without a password.
  • The Google "Hosted domain" setting is enforced. * allows any Workspace account.
  • Denied OAuth logins show the reason on the login page instead of a generic error.
  • Metrics collection settings (collection rate, history retention, push interval) moved from the Sentinel page to the Charts page. The Sentinel custom image is saved with an Apply and restart button instead of autosave. (#11292)
  • Chart tooltips show the viewer's local time and UTC. (#11292)
  • The container log viewer has Time, Type, and Message columns, and log lines expand with pretty-printed JSON (#11292). Only the visible rows are rendered, so large logs stay responsive.
  • Standalone database starts run through a queued job so credentials from secret managers can be resolved. (#11474)
  • On new KeyDB and Dragonfly databases, a REDIS_PASSWORD environment variable sets the server password and the connection URLs. Databases created before this release keep their stored password unless the variable reads a secret manager.
  • New proxy configurations use Traefik v3.7 and caddy-docker-proxy 2.13.
  • Coolify no longer reconnects the proxy to all Docker networks every hour and on server checks. The proxy is connected when a destination is created, when an application or service is deployed, and when the proxy starts or restarts.
  • Environment variable names must match [A-Za-z_][A-Za-z0-9_.]*. Existing runtime-only variables with other names, such as my-var, still deploy with a warning and a suggested name, while invalid build-time names stop image builds. (#11917)
  • Applications on multiple servers: additional servers must use the same proxy (Traefik or Caddy) as the primary server and always pull the image the primary server pushed instead of building it. Persistent volumes and Docker Compose applications can no longer be combined with multiple servers. Existing setups get a warning in the deployment log. (#12053)
  • Scheduled database backups, scheduled tasks, volume backups, and Docker cleanups are each dispatched every minute by their own scheduler process instead of one queued job, so a busy queue or a slow schedule type no longer delays the others.
  • Stopping or deleting a resource runs Docker cleanup only when the server's disk usage is at or above its cleanup threshold and no cleanup finished in the last hour. Only one cleanup runs per server at a time.
  • Hourly Sentinel version checks and weekly server patch checks run at a different time for each server instead of for all servers at once.
  • High disk usage notifications repeat at most once per interval for each server, 24 hours by default instead of about hourly. Set the interval in Server β†’ Advanced or with server_disk_usage_notification_interval_hours in the API. A new alert is sent earlier when usage dropped at least 5 points below the threshold and rises again.
  • Logging in no longer accepts a pending team invitation automatically. Invitations are accepted on the invitation page.
  • SSH_COMMAND_TIMEOUT=0 or an invalid value no longer removes the time limit of remote commands. The default of 3600 seconds is used instead.
  • Docker Swarm can only be enabled for teams that already use it.
  • Resource settings sidebars collapse their groups again, with the group of the active page open. (#11783)
  • Production and preview environment variables are shown in separate labelled sections. (#11783)
  • Project cards and lists show compact resource stats, the server list shows resource count and status, and database URLs have a copy button. (#11783)
  • Notification channel toggles and database and service actions update instantly. (#11783)
  • The running deployments indicator moved from a floating button into the sidebar (the top bar on mobile) and is also shown on the dashboard.
  • The remaining native browser confirmation dialogs are replaced with Coolify confirmation modals.

Security

  • Issue short-lived terminal session tokens on the server instead of sending SSH commands through the browser (#11942)
  • Require the two-factor challenge for OAuth sign-in, link existing accounts only when the provider verified the email address, and enforce the configured Google Workspace domain (#11907, #11989)
  • Build email verification links and the default OAuth callback URL from the instance URL instead of the request's Host header
  • Remove the unused PUT /user/profile-information route, which changed the account email without verification
  • Validate Git-based Docker Compose applications against Compose injection when they are loaded, saved, and deployed
  • Validate git refs before a deployment is queued and again when it starts (#11905)
  • Validate environment variable names before they are used in Docker commands and quote docker run -e values (#11917)
  • Validate custom internal container names, Compose network names, and static images, and quote them in Docker commands (#11912, #11914, #11958)
  • Quote container names, paths, owners, and modes in backup, database start, scheduled task, stop, service, and file storage commands (#11970, #11979, #11983, #11989)
  • Validate Compose build paths, file storage paths, and Compose volume paths. Relative file storage paths must stay inside the resource directory, Coolify never deletes host paths outside it or writes through symbolic links there, and API tokens need the deploy permission for mounts outside it (#11911, #11943, #11944, #11993)
  • Validate proxy configurations before they are saved (#11923)
  • Stop exposing the Traefik dashboard in new proxy configurations and remove the legacy dashboard router from saved ones (restart the proxy to apply)
  • Deploy pull requests from other repositories on GitLab, Gitea, and Bitbucket only when public preview deployments are enabled (#11922)
  • Hide matching applications in manual webhook responses and throttle repeated distinct signature failures per client address, repository, and branch, without blocking correctly signed deliveries (#11989)
  • Require at least 16 characters for new or changed manual webhook secrets
  • Reject Stripe webhooks when Stripe is not fully configured (#11915)
  • Enforce team ownership and permissions in onboarding, deploy key selection, notification settings, team invitations, and tag deployments (#11913, #11920, #11960, #11966, #11989)
  • Use the team that owns a resource instead of the currently selected team for permissions, secret redaction, and selectable servers, destinations, S3 storages, private keys, Git sources, cloud provider tokens, tags, and shared variables, so switching teams in another tab cannot mix teams
  • Accept and use only private keys of the same team when adding a server, on GitHub App and GitLab source settings, and for GitHub App tokens, git commands, SSH connections, and backup downloads
  • Keep existing SSH private keys out of the browser during onboarding and require update permission on a key to select it
  • Hide HTTP basic auth passwords, log drain keys, and the Sentinel token from members without update permission (#11961)
  • Hide Docker Compose content, file mount content, environment variable values hardcoded in the Compose file, server shared variable values, and proxy configuration files from members without update permission
  • Keep S3 storage keys and database passwords hidden from members after a failed save or a page refresh
  • Show container logs and scheduled task commands and output only to users who can update the resource, and require the read:sensitive permission for the log endpoints and scheduled task output in the API
  • Return the saved proxy configuration and validation logs of servers in API responses only with the read:sensitive permission
  • Keep the reference instead of the value when an environment variable references a locked shared variable
  • Show the team Danger Zone only to the team owner
  • Prevent root team admins from deleting the root user, root team owners, or their own account in the team admin view
  • Check permissions before import file checks on the database import form and before Vultr status refreshes
  • Lock the domain and DNS validation state on the Domains pages against changes from the browser
  • Require the deploy permission for instant_deploy in the API and accept only known API token permissions (#11969, #11981)
  • Enforce the server limit on every server creation path, including the API, onboarding, and cloud providers (#11968)
  • Send Git source API requests through the outbound URL guard while still allowing self-hosted Git sources on private networks, and block NAT64 addresses (#11964, #11967)
  • Keep secrets out of deployment logs when a command fails, including multiline and literal values (#11974)
  • Encrypt remote commands stored for queued tasks, remove them when the task ends, and keep the command line out of error logs, timeout errors, backup logs, and failure notifications
  • Require an instance admin for impersonation and the team admin view (#11989)
  • Rate limit logins per normalized email address (#11989)
  • Update league/commonmark to 2.10.3, which fixes GHSA-8rr7-cvq3-gmfh
  • Remove an unused application config download action

Fixed

  • Custom container names (#11701)
    • A stored custom name was applied on deploy even when consistent naming was off, while the UI hid the field. Those applications are migrated to consistent naming so their names do not change.
    • Custom names are only used in consistent naming mode. In the API, custom_internal_name turns consistent naming on, and sending it with is_consistent_container_name_enabled: false returns 422.
    • Docker Compose applications ignored the custom name and now use it: web-shop-api instead of web-<uuid>.
    • A name that another application on the same server already uses is no longer saved.
  • Deployments
    • Concurrent deployment requests respect the server queue limit, no longer queue duplicates of the same commit, and can no longer start the same queued deployment twice. (#11987)
    • A deployment that cannot be started, for example because of an invalid registry image name, is marked as failed instead of staying in progress and blocking later deployments.
    • An error after the new container passed its health check, for example in a notification, no longer removes the new container or marks the finished deployment as failed.
    • Cancelling a deployment stops the helper container on the build server and on the deployment server, and no longer runs kill -9 on the server with a process ID from the Coolify container.
    • Deployments connect the proxy to the destination network before the containers start.
    • Deleting a server marks its queued deployments as failed instead of leaving them queued.
    • Deploying, closing, or deleting a preview no longer removes the containers of other pull requests whose number starts with the same digits, such as PR 1 and PR 12.
    • Loading pull requests and pull request status updates are only used for applications with a GitHub App source.
  • Applications on multiple servers
    • Stop reaches every server even when one of them is unreachable, file mounts are written on every server, and additional servers deploy the same commit, rollback, and image tag as the primary server.
    • Queued deployments on additional servers start when the running deployment finishes or is cancelled.
    • One deployment notification is sent after all servers finish.
    • Deployments without a Docker image name fail with a clear error when started from a webhook or the API.
  • Servers
    • A server is marked unreachable only after two consecutive failed connection checks instead of one, and a single failed check no longer marks all resources on the server as exited.
    • Deployments recheck a server that is marked unreachable before failing with "Server is not functional".
    • Queue workers keep using SSH multiplexing after a server connection check.
    • Remote commands that failed on the server are no longer run a second time because their output contained words such as "connection refused". A failed S3 backup upload shows the real error.
    • Containers are matched to their resource by UUID, so containers of another Coolify instance that manages the same server are no longer mixed up with resources that have the same ID.
    • Leftover helper containers are cleaned up on every server instead of one server per run.
    • A manual Docker cleanup that starts while another cleanup runs waits instead of being dropped, and a failed cleanup marks only its own execution as failed.
    • Stopped Hetzner, DigitalOcean, and Vultr servers have the Power On button again.
  • Servers with a non-root SSH user
    • Starting and restarting the proxy and loading and saving its configuration work when the user cannot enter the proxy directory.
    • Database starts and backups, application deployments, service starts, the log drain, and volume clones work when the user cannot write to /data/coolify.
    • Pipes inside quoted strings, such as Docker --format templates, are no longer rewritten with sudo.
  • Sentinel
    • Sentinel is started with --restart unless-stopped, so Docker restarts it after a crash or reboot.
    • A Sentinel that runs but stopped pushing, or is unhealthy, is restarted, and Sentinel is no longer restarted in a loop while it starts.
    • Two Sentinel starts for the same server no longer collide, and Sentinel checks are skipped on unreachable servers. (#12100)
    • Changing the instance URL updates the Sentinel URL of remote servers that use the generated URL.
    • Container health changes show in the UI after the next push instead of up to five minutes later, and the Sentinel page shows the last push error while Sentinel is out of sync.
  • Scheduled jobs and backups
    • Scheduled backups whose queued job was lost are queued again after 60 minutes. Lost scheduled tasks and Docker cleanups are recorded as failed, and the team is notified.
    • One schedule that fails no longer stops the other due schedules, and schedules with a fixed time run once when daylight saving time repeats an hour.
    • Scheduled backups use the current server state instead of a state cached by the queue worker.
    • Backups and scheduled tasks that exceed their timeout fail with the timeout error instead of staying open.
    • Two backups of the same database that start in the same second no longer write the same file, and a backup is skipped while the database starts, restarts, or imports.
    • "All databases" backups of PostgreSQL, MySQL, and MariaDB fail when the dump command fails instead of saving an incomplete archive.
    • In a backup of several databases, every database gets its own result and finish time.
    • Failed volume backup recovery no longer piles up retry jobs or blocks new backups. Executions that need action show "Needs attention" with the reason and a retry button.
    • Settings β†’ Backup loads when the Coolify database has no backup schedule and always uses the instance database.
    • Instance cleanup jobs are no longer blocked for up to 24 hours after a worker was stopped mid-run.
    • php artisan scheduled:diagnostics no longer changes scheduler state.
  • Databases
    • "Regenerate SSL Certificates" writes server.crt and server.key for PostgreSQL, MySQL, MariaDB, Redis, KeyDB, and Dragonfly instead of server.pem, so these databases start again, and the CA file on the server matches the CA that signed the certificate.
    • New and regenerated database SSL certificates use a P-256 key, so Electron-based clients such as MongoDB Compass can connect.
    • The MongoDB health check pings the database instead of always passing. (#11730)
    • ClickHouse databases with a file mount keep their data volume. Affected databases keep their current data and ask to adopt it before the next start.
    • Databases and services show their new status right after a start.
  • Database restores
    • Single-database MySQL and MariaDB restores decompress .gz archives instead of piping them into the client, and dump-all MySQL restores emit valid shell environment variables. (#11699)
    • Database restores detect the backup format before changing anything. "All databases" imports no longer drop everything when the file cannot be restored, PostgreSQL restores run in one transaction, and replace restores of SQL backups only swap in the new database on success.
    • Interrupted or stale database imports are stopped and cleaned up and no longer block later imports, and a second start, restart, or import while one is running is rejected (409 in the API). Long imports are no longer cut off by the 10-minute task timeout.
    • Imports use the selected source. A checked server path is no longer replaced by an earlier upload that was never imported.
  • Compose and storage
    • Compose volumes declared as external are used as declared instead of being renamed to <uuid>_<name>. Existing resources keep their old volume, the deployment log explains how to switch, and the storage page lists external volumes. Preview deployments keep their own volume.
    • Compose volumes keep their driver, driver_opts, and labels when Coolify renames them (volumes created before the upgrade keep their settings), NFS and CIFS volumes are no longer dropped from a service that has other volumes, and ../ bind sources resolve to the parent directory.
    • Deleting a Docker Compose preview removes only the networks and volumes Coolify created for it, instead of every network and volume in the Compose file.
    • Content files are written before the containers start, for every build pack and on every server of the application, and their content is no longer deleted when Docker created a directory at the file's path.
    • File and directory mounts with a relative path are created inside the resource directory instead of the SSH user's home directory, and cloned volumes keep the driver and options of the source volume.
    • Service switches save without saving pending Compose edits, services with an empty Compose file no longer block proxy starts, and Compose comments are kept. (#11985)
    • Starting a service after the configuration of an existing volume changed no longer skips the next start step.
  • API
    • GET /applications/{uuid}/logs respects service_name and returns 404 when no running container matches. (#12066)
    • POST /deploy with pull_request_id builds the pull request instead of the base branch for deploy key and public repository applications.
    • Creating a Docker Compose application no longer generates an unused top-level domain.
    • Pull request IDs above the integer range return a validation error instead of a 500, also in the MCP deploy tool.
    • Database create requests are validated (422 for invalid input), accept numeric resource limits, and read instant_deploy as a boolean.
    • The database list no longer returns backup configurations of another database type with the same ID.
    • GET /servers/{uuid}/domains?uuid=<application uuid> filters by application instead of returning 404.
    • The API reference documents PATCH /security/keys/{uuid} instead of PATCH /security/keys.
  • Event toggles on the Email notification settings page work again. (#11512)
  • Email notification and log drain settings are restored when enabling them fails, other notification toggles return to their saved state when saving fails, and conflicting email providers can no longer be enabled together. (#10543)
  • Resend errors show a clear message, and an email that Resend did not accept is no longer counted as sent.
  • A proxy in a restart loop sends at most one "container restarted" notification per hour.
  • GitLab OAuth sign-in reads the user from GitLab API v4 instead of the removed v3 endpoint.
  • Revoking or expiring a team invitation no longer deletes a user who already joined another team.
  • Pages that stay open while you switch teams in another tab no longer fail when realtime events arrive.
  • Members get a 403 instead of a 500 on the Cloud Tokens page, and non-admins are redirected from the OAuth settings page.
  • Gitea preview deployments use the pull request's head commit instead of HEAD.
  • Webhooks with pushes without commits or malformed payload values get a clean response instead of a 500.
  • Re-checking DNS replaces a stored result, so application, service, and preview domains no longer keep their first status. (#11951)
  • DNS checks compare IPv6 addresses by value, so the same address written differently matches.
  • Copying DNS record values from the DNS entries dialog works on instances served over plain HTTP.
  • Services on unreachable servers can be removed from Coolify only. Deleting any resource on an unreachable server warns that its Docker resources stay on the server and notifies the team afterwards.
  • The service list no longer becomes empty when the template CDN returns an empty or invalid response.
  • The Grafana admin user and password fields show for Grafana images with a registry prefix, such as docker.io/grafana/grafana. (#10617)
  • The terminal shows an error instead of an endless "connecting…" spinner when a session cannot start.
  • The Logs page shows why containers could not be loaded instead of "No containers are running".
  • Applications without a configuration snapshot show pending configuration changes again.
  • "Generate default" for the custom Nginx configuration of a static site with SPA enabled generates the SPA configuration.
  • Saving an environment variable shows validation errors instead of a generic error.
  • The "Never" expiry of a new API token is kept instead of falling back to 30 days.
  • GitHub sources have the Test connection button again.
  • The duplicate check for private keys only looks at the team the key belongs to.
  • The 2FA setup URL on the profile page is shown and copied with & instead of &amp;.
  • The Help form shows an error when the feedback could not be delivered.
  • Quick adding tags with special characters, such as apostrophes, works. (#11971)
  • Additional destinations can no longer be added twice.
  • Applications with a git:// repository URL no longer crash when showing commit links.
  • Running the install script again no longer changes the owner and permissions of resource data under /data/coolify, and it waits for the Docker daemon on OpenRC.
  • The daily database cleanup deletes old rows in batches instead of one long DELETE.

Services

New

  • 9router: AI coding gateway that routes coding assistant requests to 40+ LLM providers with fallback (#11592)
  • Bulwark: JMAP webmail (#11180)
  • Docling: converts PDF, DOCX, PPTX, images, and HTML to Markdown and JSON (#9121)
  • Engram: persistent memory sync server for AI coding agents over MCP (#10808)
  • Hermes Agent: autonomous AI agent with persistent memory, scheduling, and a web dashboard (#10703)
  • Honcho: memory and reasoning for personalized AI agents (#11184)
  • Lidarr: music collection manager for Usenet and BitTorrent (#11576)
  • Linkwarden: collaborative bookmark manager that preserves web pages (#11561)
  • Obsidian: the Obsidian desktop app in the browser (#10704)
  • OpenWA and OpenWA with PostgreSQL and Redis: self-hosted WhatsApp API gateway with a dashboard (#11448)
  • PeerTube: decentralized video platform (#9564)
  • Portabase: database backup and monitoring (#11054)
  • Snipe-IT: IT asset management (#10544)
  • Zero: query-driven sync engine for TypeScript apps backed by Postgres (#10713)

Updated

  • Appwrite 2.0.0. New Appwrite services use PostgreSQL instead of MariaDB. (#10810)
  • Authentik 2026.5.6, with data stored in ./data instead of ./media. (#8791)
  • Autobase 2.11.0 with DBDesk Studio. (#9850, #11749)
  • Beszel Agent 0.19.0 with configurable LISTEN and HUB_URL. (#11647)
  • Bugsink requires an admin email and adds email, site title, and time zone settings.
  • Budibase no longer runs Watchtower.
  • EMQX Enterprise 6.2.2. (#10922)
  • Garage 2.3.0 with a generated access key, secret key, and default bucket. (#10735)
  • Hermes Agent with WebUI uses Hermes Agent v2026.6.5 and Hermes WebUI 0.51.489. (#10702)
  • Homarr 1.74.0. (#9821)
  • Karakeep 0.33.2 with the Karakeep Chrome image and Meilisearch 1.41.0. (#11245)
  • Plausible 3.2.1, which fixes CVE-2026-8467. ClickHouse settings match upstream: a 30-day query log, IPv4-only listening, and lower resource usage. (#10975, #11939)
  • Pterodactyl Panel and Pterodactyl with Wings 1.12.3 are available again. (#11173)
  • Rallly uses PostgreSQL 18, requires an initial admin email, and adds a registration toggle.
  • SigNoz 0.137.1 with ClickHouse 25.12.5. (#11346)
  • Terraria Server 1.4.5.0 with a generated server password. (#11322)
  • Vikunja and Vikunja with PostgreSQL have health checks and use VIKUNJA_SERVICE_SECRET. (#10331)
  • Mattermost is marked as AMD64 only.
  • osTicket is hidden from the service list. (#10621)

Fixed

  • AFFiNE: the Postgres health check uses the configured user instead of affine.
  • Budibase: one-click deployments work with the budibase/database image. (#9828)
  • Bugsink: superuser creation works, and the MySQL user and password show in the UI. (#11225)
  • Buzz: desktop app origins are allowed by CORS. (#11046, #11741)
  • Chatwoot: the Sidekiq health check is lighter. (#10920)
  • Chibisafe: uploaded files are served from the correct uploads volume. (#11804)
  • CyberChef: uses port 8080. (#11170)
  • Deno KV: its options show up again. The template is renamed from denoKV to deno-kv, and the old key still works in the API and for existing services.
  • Dozzle with auth: documents the bcrypt password hash and the correct default password. (#11235)
  • Fider: BASE_URL no longer includes the port, which caused CSP errors. (#11682)
  • OpenClaw: the generated username shows in the UI. (#8629)
  • Rallly: login no longer fails with an invalid origin error. (#9536)
  • SigNoz: no more broken pipe errors. (#11640)
  • TriliumNext: runs on ARM64. The health check uses Node instead of wget.
  • Twenty: connects to its backend again. (#11562)
  • Vaultwarden: fresh installs with Vaultwarden 1.37 work with the SQLite database URL. (#11471)

Removed

  • Unused persistent storage Show Livewire component and view. (#11615)
  • Unused Blade and Livewire components and views.
  • Legacy Laravel Dusk browser tests, DuskServiceProvider, and the laravel/dusk dependency. Browser tests use the Pest browser plugin.
  • Laravel Nightwatch integration: the laravel/nightwatch dependency, the Nightwatch agent service in the Coolify container, and the NIGHTWATCH_ENABLED setting.
  • Settings β†’ Scheduled Jobs monitoring page.
  • The PROXY_CONNECT_NETWORKS_INTERVAL_SECONDS setting.
  • The TrustHosts middleware, which never checked the host.

Refactored

  • Container name generation uses one code path for single-container and Compose applications. (#11701)
  • Database start command execution is extracted into a shared service and job. (#11474)
  • Action buttons share one split-button component, removing duplicated markup and CSS. (#11409)
  • Volumes and directory mounts are separated in the storage UI. (#7591)
  • Team broadcast events share one trait and always name their team.

Issues

  •  

Minecraft 26.4-snapshot-3 (snapshot) Released

26.4 Snapshot 3 (known as 26.4-snapshot-3 in the launcher) is the third snapshot for Java Edition 26.4, released on October 6, 2026, which adds the ice caves including ice crystals, icicles, ice balls, the frostbite and the Freezing effect, and fixes bugs. Full changelog: https://minecraft.wiki/Java_Edition_26.4-snapshot-3
  •  

South Dakota: Community Spotlight

Since the release of the South Dakota DLC for American Truck Simulator, we’ve loved seeing all of your screenshots, videos, reviews, and trucking adventures from across the Mount Rushmore State. Watching our community explore this new expansion has been incredibly rewarding for our team, which is why we wanted to shine a spotlight on some of our favourite community content, as shared by you!


For those of you who may not have had the chance to hit the road in South Dakota just yet, we wanted to highlight a few YouTube videos we enjoyed, to give you a glimpse of what awaits in this newest map expansion for ATS. We hope these will inspire you to start your own journey through the The Land of Infinite Variety! A big shoutout to everyone featured below, be sure to give them a subscribe and a like!


We’ve also been seeing plenty of amazing screenshots and videos shared across social media on X, BlueSky, Instagram, Facebook, TikTok, and more. Thank you to everyone who has tagged us, shared their adventures, and shown off their favourite areas of South Dakota. Our teams genuinely enjoy scrolling through your photos and seeing your unique trucking setups and routes. Here are just a few that we liked!


We also want to thank everyone who has taken the time to leave reviews and feedback on Steam. Reading your comments and impressions means a lot to our developers, map designers, artists, and the entire team behind American Truck Simulator. Your support, suggestions, and enthusiasm continue to help shape the future of the game and motivate us every day.Β 


If you’ve been enjoying your time in South Dakota, we’d really appreciate it if you considered leaving a review on the DLC Steam page, we would really appreciate it! You can find the review section at the bottom of the Steam Store page.

We have also reached out to a few content creators who got the opportunity to try out this DLC in early access to give us their opinion on the South Dakota map expansion. It's safe to say they enjoyed it too! We also recommend checking out their channels for more content!

BadMae


"We’ve had such a fun time exploring South Dakota together! Seeing Mount Rushmore was definitely a highlight, but we also loved discovering the quarries, landmarks, and quiet towns throughout the state. With a little research, you start to realize just how much history is represented across the map and how each place played a part in shaping South Dakota. We also got an early taste of the new Road Trip experience, which gave us an entirely new and fun way to explore the South Dakota map. South Dakota has been a great addition to ATS, and we’re excited to keep discovering more!"Β  - Christian & Monique, BadMae

Milan


"South Dakota's the first state DLC in a while that actually made me slow down on purpose. The plains stretch forever, then you drop into the Badlands and it feels like someone switched planets, especially around golden hour.

Mount Rushmore is the obvious photo stop, but the real grin moments are in the smaller details: that quarry plonked weirdly in the middle of the Sioux Falls suburbs, the trailer plants in Watertown and Mitchell, and farm depots surrounded by actual shelterbelts dating back to the Dust Bowl era.

Deadwood still has that Wild West vibe, which I personally enjoy, and compared to some previous DLCs, South Dakota feels like it has several different personalities packed into one state. You keep getting those "wait, is that a real landmark?" moments along the way. That's probably what I like most about it. It feels more like a proper road trip."


TheHuskie


"What impressed me the most in South Dakota DLC is how much effort has clearly gone into making the state feel authentic and realistic. The scenery is incredibly detailed, and the variety between the wide-open Great Plains, the Badlands, and the Black Hills makes the experience feel very different depending on where you are driving.

I especially enjoy the Black Hills and the more winding roads there. They provide some really beautiful driving experiences and, from a content creator’s perspective, give me a lot of opportunities to create cinematic shots. Mount Rushmore and the other landmarks also make exploring the map feel more rewarding, while the smaller towns and rural areas add a lot of character to the journeys."


We would like to thank you all for your continued support! Keep on sharing your journeys through the South Dakota DLC with us on our social media channels using the hashtag #CruisingSouthDakota and by tagging us on Social Media. Until next time, keep on truckin'!Β 

  •  

Firefox 157.0.1

Fixed

  • Fixed downloads failing on macOS when Firefox is set to ask where to save files but doesn't have permission to access the Downloads folder. (Bug 2077390)

  • Fixed the sidebar getting stuck on the Bookmarks or AI Chatbot panel for some users. (Bug 2076296)

  • Fixed the Restore from Backup option not appearing during onboarding on Windows. (Bug 2073401)

  • Security fix.

  •  

MediaInfo 26.10

MediaInfoLib source code has been audited by several security researchers and private individuals. Thank you to Yazan Balawneh (CyStack), Feng Ning (Innora), TristanInSec, Gareth Davidson (bitplane), Stanley Tang, Brandon Barrante, Erik White, Miklos Juhasz, iliasabk, buzz, mega-wli, cjee21, and many others for their reports and/or patches.
+ Update of Turkish translation, thanks to umablognot
+ Update of Czech translation, thanks to Michal VΓ‘rady
+ Update of Portuguese (Brazil) translation, thanks to FΓΊlvio Alves
+ Update of Russian translation, thanks to solokot
+ Windows GUI: Fix missing translation for some UI elements
+ macOS GUI: Add close button in Compare view's header
+ Android GUI: avoid to ask for geolocation data access many times
+ Android GUI: fix of a couple of crashes while migrating from Rx Java to Kotlin Coroutines, thanks to cjee21
+ Conformance checker: update with more precise error messages, sponsored by Austrian Mediatek
+ Conformance checker: tolerate common padding patterns found in some files, sponsored by Austrian Mediatek
+ MXF: cross-check header and footer values for timecode tracks, prioritizing the footer value
+ MXF: support more ARRI camera metadata, thanks to Luis GΓ³mez GutiΓ©rrez
+ Global performance improvement when analyzing files with uncommon file extensions or junk files
+ HEVC: support interlaced content, thanks to TorbjΓΆrn Einarsson
+ HEVC: detect CBR and report nominal bitrate
+ AV2: support v1.0.0 streams, thanks to cjee21
+ MP3: support gapless files, thanks to hat3k
+ MOV/MP4: support Auro CS layout information, thanks to almirus
+ DTS:X: support supplemental channel layout, thanks to almirus
+ EIA-608/708: report maximum number of characters per line
+ TTML: report maximum number of characters per line
+ MOV: support chpl version 0
+ ELF: support RISC-V
+ GIF: support XMP and loop count, thanks to cjee21
+ GIF: support animated GIFs
+ I2632, ApeTag: handle cover images, thanks to cjee21
x I2690, TAR: improve parsing of the TAR header to avoid more false positives
x I2706, MPEG-TS: fix infinite loop with some partial packets at the end of the file
x I2670, DVD-Video: preserve IFO stream languages after VOB merge, thanks to wastaken7
x I2589: fix MediaInfoList_Open file options not being used with the DLL API
x MXF: fix failure to detect sparse content in Teletext or OP47, thanks to MaxEliaserAWS
x DTS: move DTS:X objects to their own field, matching Dolby Atmos
x Opus: fix 5.0 support and center-channel ordering, thanks to Puella Purpura
x MP3: detect headerless VBR after parsing finishes, thanks to Bernard Wiesner
x MP3: fix reconstructed settings for LAME CBR 256 and 320 kbps, thanks to hat3k
x MP3: clean up some LAME version values
x MOV: fix mapping for Apple language tags >= 95

  •  

The best vMix Laptop for 2026-2027!

Each year at vMix we take a look at the available laptops on the market and put forward the best option for vMix. It’s usually a powerful laptop that capable of a 4 camera production with streaming and recording…but at an affordable price point. You may have preferred laptop brands, and that’s ok! You’ll just need to match or exceed our recommended specs. This year we’re recommending the…

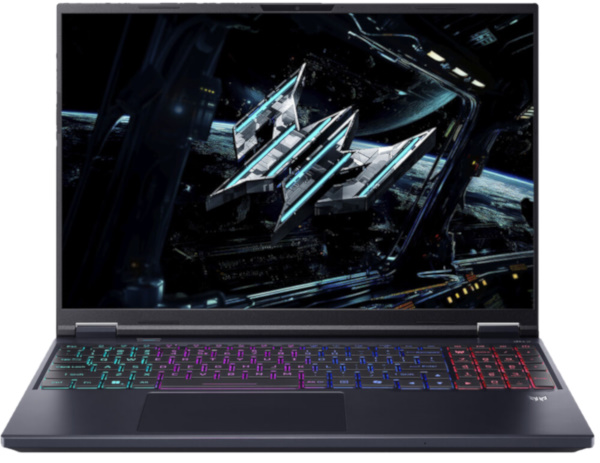
Acer 16β€³ Predator Helios Neo 16 AI (PHN16-I71-90LV)

  • Intel Core Ultra 9 290HX Plus 24-Core
  • 16GB DDR5 | 1TB M.2 PCIe 4.0 SSD
  • 16β€³ 2560 x 1600 IPS 240 Hz Display
  • NVIDIA GeForce RTX 5070 Ti (12GB GDDR7)
  • HDMI | USB-C | USB-A | Thunderbolt 4
  • 2.5 GbE | Wi-Fi 6E | Bluetooth 5.4
  • Full HD Webcam
  • RGB Backlit Keyboard | Touchpad
  • Windows 11 Home
vMix Laptop 2026-2027

Link to the laptop on B+H. It retails for $2,549.00 USD but it’s often on sale, so if you keep your eye on it you can probably get it for cheaper!

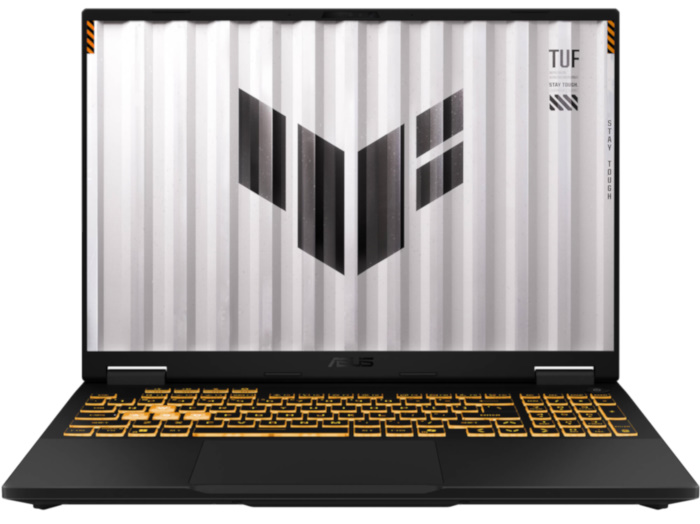
ANOTHER Option! ASUS 16β€³ TUF Gaming F16 Laptop (FX608LPG-BB94)

Unsurprisingly, after we bought the Acer and made the video…B+H started to stock the 2026 version of the Asus TUF Gaming F16 with the 290HX! It’s very similar to the Acer Predator, although it has an RTX 5070 instead of the 5070ti, but that’s not really worth the extra $150.

  • Intel Core Ultra 9 290HX Plus 24-Core
  • 16GB DDR5 | 1TB M.2 SSD
  • 16β€³ 2560 x 1600 OLED 165 Hz Display
  • NVIDIA GeForce RTX 5070 GPU (8GB GDDR7)
  • Gigabit LAN | Wi-Fi 6E | Bluetooth 5.4
  • Thunderbolt 4 | HDMI 2.1 | USB-C
  • User-Upgradable RAM & SSD Slots
  • Full HD IR Webcam
  • Windows 11 Home

B+H link. This is currently priced at $2,399.99 USD, but again, there are always sales at B+H, so you may be able to get it cheaper.

Asus website link to the laptop model.

If you want to different brand or model, what should you look for?

  • Intel Core Ultra 9 290HX Plus 24-Core
  • 16GB or 32GB of DDR5 Ram
  • 1TB SSD
  • NVIDIA GeForce RTX 5060/5070/5070 Ti GPU
  • Advanced Optimus or Mux Switch
  • Thunderbolt 4 if you require it

Do you need the latest and greatest?

If you don’t need bragging rights then no you don’t need the latest gen of CPU. If you’re able to get an Intel Ultra 9 275HX on sale, then that’s a great way to go! Here’s the specs to look for-

  • Intel Core Ultra 9 275HX
  • 16GB or 32GB of DDR5 Ram
  • 1TB SSD
  • NVIDIA GeForce RTX 5060/5070/5070 Ti GPU
  • Advanced Optimus or Mux Switch
  • Thunderbolt 4 if you require it.

You could even look for an older CPU like a 14th gen i9. Here are some of our older recommendations!

2024-2025 Laptop– Intel i9 14900HX
2025-2026 Laptop– Intel Core Ultra 9 275HX

Laptop best practices!

Check out our Knowledge Base article about getting the most out of your laptop with vMix-https://www.vmix.com/knowledgebase/article.aspx/264/laptop-best-practices

  •  

Counter-Strike 2 Update

[p]\[ MISC ][/p]
  • [p]Pet photobook pages now have localized text art.[/p][/*]
  • [p]Added play menu buttons to manage downloaded Workshop maps.[/p][/*]
  • [p]Adjusted VK shader cache extension flags.[/p][/*]
  •  

12.2

πŸš€ Jellyfin Server 12.2

We are pleased to announce the latest stable release of Jellyfin, version 12.2! This minor release brings several bugfixes to improve your Jellyfin experience. As always, please ensure you take a full backup before upgrading!

Discuss this release further on our forums.

Changelog (51)

πŸ“ˆ General Changes

  •  

12.2

πŸš€ Jellyfin Web 12.2

We are pleased to announce the latest stable release of Jellyfin, version 12.2! This minor release brings several bugfixes to improve your Jellyfin experience. As always, please ensure you take a full backup before upgrading!

Discuss this release further on our forums.

Changelog (17)

πŸ”’ Security

  • Fix track titles and external urls not being escaped [PR #8533], by @thornbill

🌟 Highlights

πŸ—οΈ Enhancements

πŸ“ˆ General Changes

  •  

uNmINeD 0.20.11-dev

New uNmINeD development snapshot is available for download!

Changes:

  • Fixed lossy WebP transparent background
  • Missing Bedrock LevelDB *.ldb files are ignored instead of throwing an error
  • Added LibDeflate for linux-musl (Alpine) builds for speed
  • Improved Bedrock to Java block conversion speed
  • 2D rendering speed optimizations
  • Improved 26.3+ default blockstate resolving speed
  • (Isometric) Added 14Β° pitch angle
  • (Isometric) Redesigned block model processing, caching and rendering pipeline
  • (Isometric) Huge drop in memory usage
  • (Isometric) Improved speed
  • (Isometric) Improved CPU utilization
  • (Isometric) Fixed crashes when using image adjustments

Notes:

  • Isometric image and web export is not yet available
  • Documentation and howto’s for isometric mode are coming soon

Setting up isometric mode:

  • Isometric mode and the experimental block model rendering needs a Java Edition client JAR file for both Java and Bedrock worlds. Select one in World/App settings menu (β€œDefault Minecraft client JAR to use” setting). If you do not have a Java Edition client installed, you can download a client JAR file from the Minecraft Wiki.
  • For Bedrock, select a vanilla resource pack ZIP file in World/App settings. You can download one from GitHub: click on Assets, then download the bedrock-samples-*-full.zip file. Versions does not have to match exactly, using the latest resource pack usually works.
  •  
❌