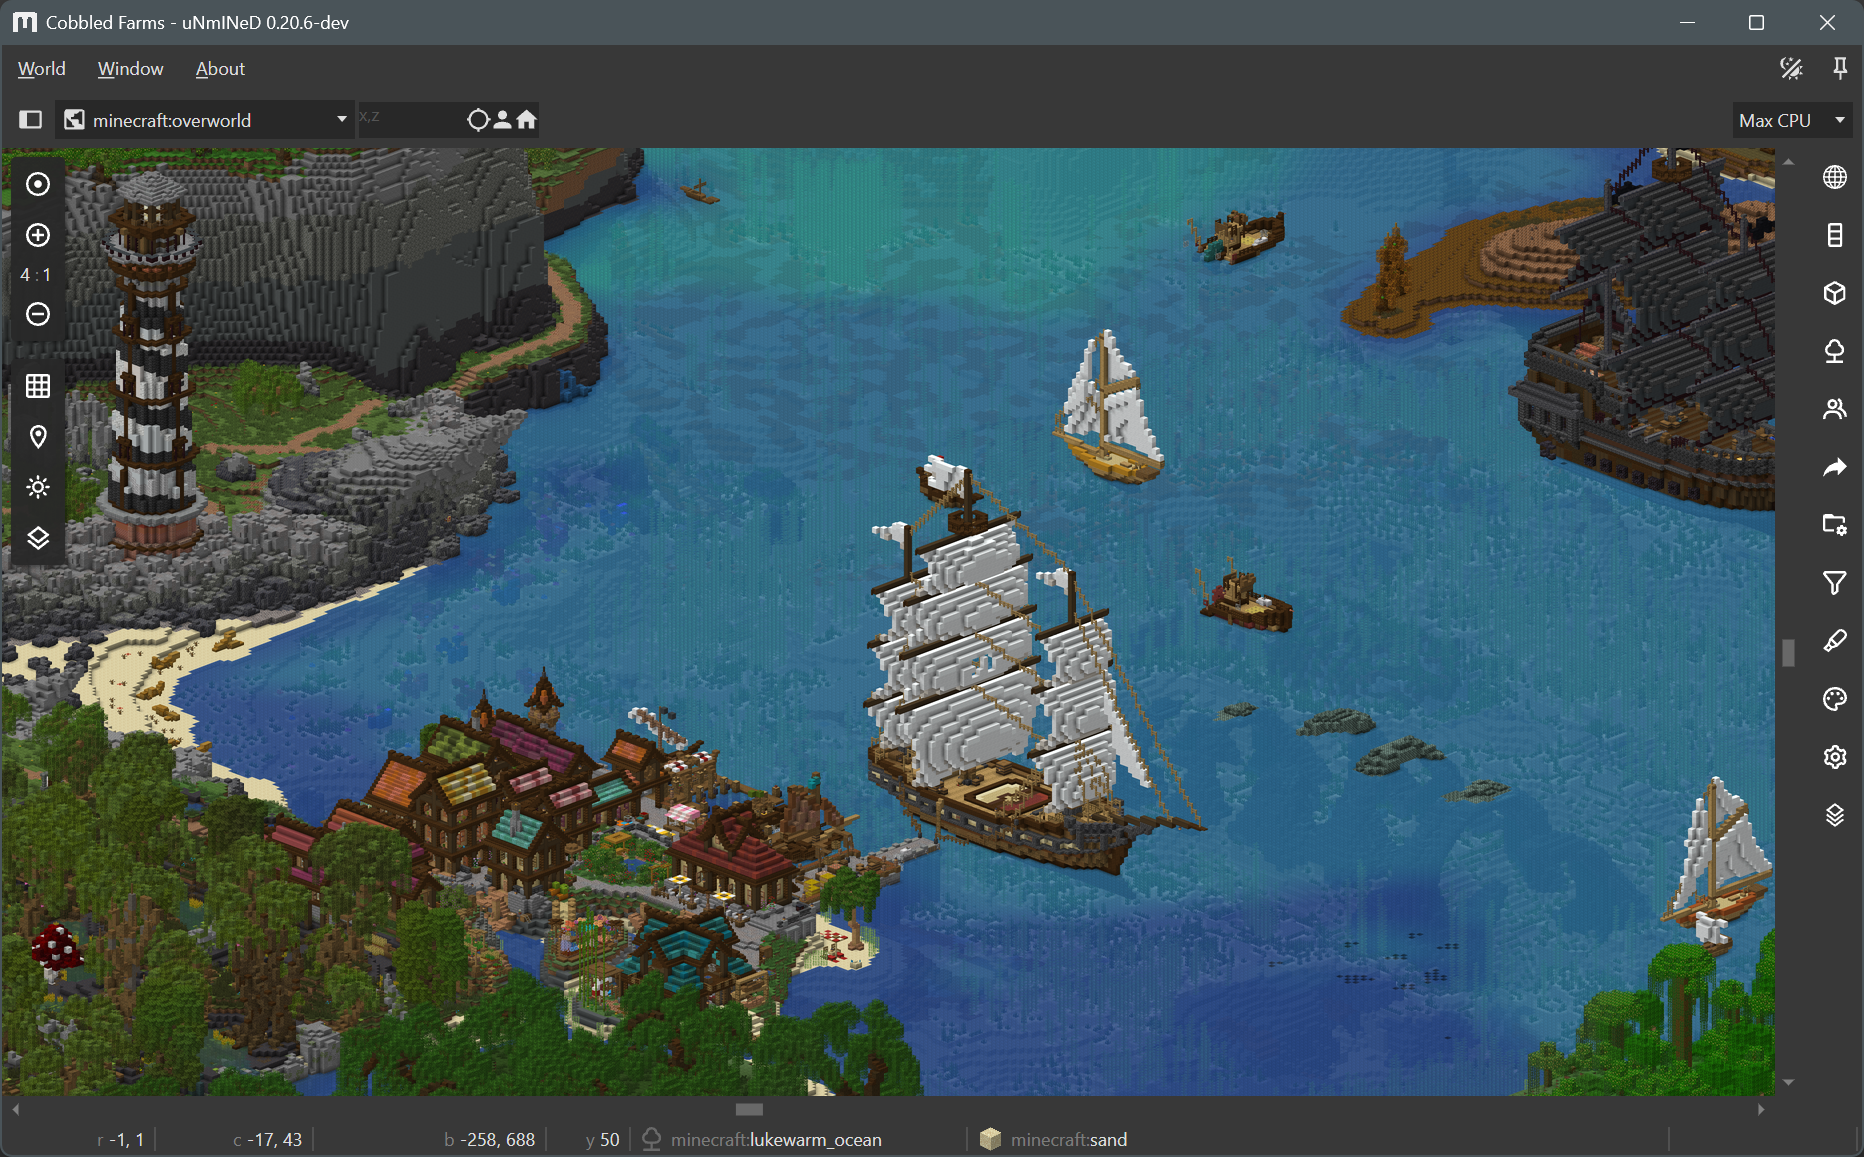
❌

Lees weergave

v0.16.21

[0.16.21] - 2026-09-06

If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.

Added

Changed

  • Sieve: Messages generated by user scripts are DKIM signed through the new SieveUserInterpreter.dkimSignDomain setting, which defaults to the account's own domain.

Fixed

  • JMAP:
    • CalendarEvent/set requests that ask for scheduling messages are rejected with a forbidden error when the account cannot send them.
    • Calendar/get and AddressBook/get return every property when the properties argument is omitted or null.
    • EventSource ping events advertise the interval in seconds rather than milliseconds.
    • Calendar synthetic ids returned when expanding recurrences identify an occurrence by its recurrence id.
  • IMAP: Every command in a pipelined STATUS or FETCH batch receives its tagged completion, instead of the first failing command dropping the responses for all commands queued behind it.
  • WebDAV: Accounts without a storage quota no longer advertise a 4 GiB limit in DAV:quota-available-bytes.
  • MTA: Inbound DMARC and TLS aggregate reports that a reporter sends more than once are imported again as a duplicate entry.
  • Spam filter: Domain and URL blocklists are queried only for text written as a link.
  • iTIP: Detaching an occurrence that the recurrence rule already generates is sent as a METHOD:REQUEST carrying the RECURRENCE-ID instead of a METHOD:ADD.
  • Sieve: fileinto :specialuse and specialuse_exists accept special-use attributes in the \Trash form.
  • LDAP: Active Directory servers that answer an unauthenticated bind (a non-empty DN with a zero-length password) with success no longer authenticate accounts without a password.
  • Network: Listeners bound to the unspecified IPv6 address ([::]) fall back to IPv4 when socket creation fails with EPROTONOSUPPORT.
  • OpenTelemetry: log exporter does not include the parent span's attributes.

Check binary attestation here

  •  

v1.21.0

New major features

Media-over-QUIC

  • support forwarding streams (#6145)

API

  • add /paths/static-sources/get endpoint (#6177) this allows to obtain details about static sources.
  • add type-specific properties to forward destinations (#6178)
  • add type-specific properties to static sources (#6184)

Fixes and improvements

General

  • add --validate-conf flag (#5549) (#6140)
  • use internal/core/VERSION as single source of truth to get version (#6119)
  • httpp: propagate Flush() through the response writer wrappers (#6126) handlerLogger's responseRecorder and handlerWriteTimeout's writeTimeoutWriter both wrap http.ResponseWriter but implement neither http.Flusher nor Unwrap(). Any handler that flushes mid-response has that flush silently dropped, and its output only reaches the client when the handler returns. That defeats the stated purpose of writeTimeoutWriter, whose own comment says it exists so one can "write long responses, splitted in chunks, without causing timeouts": the deadline is reset per Write(), but nothing ever leaves the buffer until the end. Found while adding a server-sent-events endpoint: events written and flushed at t=0.4s onlyreached the client at t=2.2s, when the handler returned. Adding Flush() plus Unwrap() (so http.ResponseController can reach through) fixes both. The new test drives a real listener throughboth wrappers and reads while the handler is still blocked, so it fails on the current code by hitting the read deadline.
  • support setting read buffer size on macOS (#6128) (#6131)
  • drop support for Debian Bullseye (#6137) Bullseye reached EOL on 31st august 2026.
  • emit "closed" log message when a server is closed (#6152)
  • fix external command exit code reporting on non-Windows platforms (#6155)
  • conf: support YAML version directives (#6157)
  • metrics: add 'pos' property to forward_dests (#6183)
  • metrics: deprecate the 'remoteAddr' property (#6174) Metrics are meant to provide aggregate statistics, not per-peer properties, that can be accessed through the API. The property is still served to keep backward compatibility.
  • metrics: add 'type' to forward dests, deprecated 'protocol' (#6170) 'type' is aligned with the terminology used in the rest of the server.
  • metrics, pprof: set default Allow-Origins to empty list (#6165) This prevents cross-site attacks to the API with the default configuration.
  • always-available: support disabling recording when the source is offline (#6182) Add alwaysAvailableRecorded parameter that controls whether recording happens during offline periods for always-available paths. When set to false, recording only starts when a real source is connected.
  • allow sources and forward destinations with an empty password (#6193) Restore the behavior introduced in #395 and accidentally reverted by #5779, which factored the RTMP/HLS credential check into validateURL() and applied it to RTSP sources too. A username with an explicitly empty password is valid per RFC 3986 and is required by some legacy cameras whose password cannot be set. It is now accepted for every scheme handled by validateURL(), including forward destinations. A username without password or a password without username is still rejected,with a clearer error message pointing to the right syntax.
  • fix wrong validation of HTTP allowed origins (#6198) An allowed origin with wildcards was making the server accept origins with a different scheme. This is fixed.
  • fix HTTP allowed origins dots being interpreter as any character (#6199) A dot in an HTTP allowed origin now requires a corresponding dot in an incoming origin.
  • serve Origin: Vary header with Access-Control-Allow-Origin (#6200) This prevents CDNs from caching the Access-Control-Allow-Origin header regardless of the origin.
  • stop returning wildcard in Access-Control-Allow-Origin (#6201) if domain is allowed, return the domain, otherwise nothing.
  • pmp4, fmp4: stop validating inbound H264/H265 SPS (bluenviron/mediacommon#366) Validating SPS adds latency and is generally redundant.
  • pmp4, fmp4: do not accept empty H264/H265 parameters (bluenviron/mediacommon#367)
  • h265: fix DTS extraction of streams with temporal sub-layers (bluenviron/mediacommon#368) The picture-type switches in the H265 DTS extractor accepted only TRAIL_N/TRAIL_R/RASL_N/RASL_R, so an access unit whose slices are TSA_N/TSA_R/STSA_N/STSA_R (Rec. ITU-T H.265, table 7-1, types 2-5) fell through to "access unit doesn't contain an IDR or non-IDR NALU" and the stream could never be recorded. TSA and STSA pictures use the same slice segment header syntax as TRAIL pictures, so handle them in the same way.

API

  • add 'type' to forward dests, deprecated 'protocol' (#6170) 'type' is aligned with the terminology used in the rest of the server.
  • set default Allow-Origins to empty list (#6165) This prevents cross-site attacks to the API with the default configuration.
  • deprecate 'conf' field of forward destinations (#6175) configuration is already available through the confName property of the path.
  • refactor endpoint names (#6172) group endpoints by category (i.e. /hls/muxers, /hls/sessions), rename /forward/* into /forward-dests/*, use kebab-case. Backward compatibility is preserved by still serving old endpoints.

Media-Over-QUIC

  • rename boolean header fields (#6148) rename Properties into HasProperties, FirstObject into IsFirstObject
  • add shared Conn interface (#6149)
  • close server streams when no longer in use (#6151) Explicitly close bidirectional and unidirectional streams that were previously keep open for the entire duration of the session. Note that closing a stream in QUIC/WebTransport means telling the peer that "we are not sending data anymore", while still allowing inbound data.
  • add shared client (#6150)
  • impose a 100MB limit on reordered bytes per session (#6194) previously, the limit was per-track. This decreases the probability of incurring in an out-of-memory situations.

RTSP

  • redact credentials in logs (#6158)
  • demux MPEG-TS from static source pull (#6181) When rtspDemuxMpegts is set, a pulled single MP2T track is demuxed into elementary streams, matching RTSP publishers, so HLS can attach.
  • support setting read buffer size on macOS (#6128) (bluenviron/gortsplib#1143)
  • client: ignore invalid source IPs in SETUP responses (bluenviron/gortsplib#1070) (bluenviron/gortsplib#1145)
  • fix decoding and encoding fragmented MPEG-4 audio packets (bluenviron/gortsplib#1150) The AU-size field was set incorrectly in subsequent fragments.
  • stop validating inbound H264/H265 SPS (bluenviron/gortsplib#1151) Validating SPS adds latency and is generally redundant.
  • Support SDES (RFC 4568) SRTP key exchange for RTSP/RTSPS sources (bluenviron/gortsplib#1148)
  • rtpklv: do not reuse buffer of returned KLV units (bluenviron/gortsplib#1154) Decode() returns a slice that points to the decoder's internal buffer, and the next call to Decode() overwrites that same array in place. A caller that holds the previous unit - for instance while it is being recorded or forwarded on another goroutine - ends up reading the bytes of the next unit, or a torn mix of both when the sizes differ. Clear the buffer instead of truncating it, so each unit gets its own array. This is what the h264, h265, av1, vp8 andmpeg1video decoders already do, at the cost of one allocation per unit.
  • auth: support qop=auth in digest client (bluenviron/gortsplib#1074) (bluenviron/gortsplib#1155) The client never looked at the qop directive of a digest challenge and always computed the legacy RFC 2069 response, so servers that require qop="auth" - as most RFC 7616 implementations do - rejected every request with a 401. Parse qop in WWW-Authenticate, and when the server offers "auth", send qop, cnonce and nc and compute the response as H(HA1:nonce:nc:cnonce:qop:HA2) (RFC 7616, section 3.4.1). The nonce count increases at every request, as required. Challenges without qop keep the previous behavior. auth-int is not implemented. Also copy the opaque value of the challenge into the Authorization header, which RFC 7616 section 3.3 says the client should return unchanged.
  • client: remove Content-Length from HTTP tunnel GET request (bluenviron/gortsplib#1158)
  • rtpav1: do not set Y/Z bits when no OBU bytes were written (bluenviron/gortsplib#1153) When the remaining space in a packet is too small to hold any byte of thenext OBU, the encoder writes nothing but still marks the current packet with Y=1 and the following one with Z=1. The AV1 RTP payload format (v1.0, section 4.4) requires both bits to be 0 unless an OBU element is actually fragmented across the two packets. Receivers that honor the bits therefore join two complete OBUs into one: this happens with the decoder in this package, with pion/rtp and with ffmpeg. It is reachable whenever an earlier OBU leaves exactly 0 free bytes (or 0-2 when the next OBU is size-prefixed), so it affects streams that are repacketized, e.g. non-RTSP sources read over RTSP in mediamtx.

RTMP

HLS

  • validate hlsSegmentCount according to the HLS variant (#6154)

WebRTC

  • Register RTX for incoming video tracks (#6125)
  • fix deprecated webrtcICEServers parser for IPv6 hosts; (#5932)

RPI Camera

Dependencies

  • code.cloudfoundry.org/bytefmt updated from v0.85.0 to v0.88.0
  • github.com/bluenviron/gohlslib/v2 updated from v2.4.3 to v2.4.4
  • github.com/bluenviron/gortmplib updated from v1.0.1 to v1.0.2
  • github.com/bluenviron/gortsplib/v5 updated from v5.6.4 to v5.6.5
  • github.com/bluenviron/mediacommon/v2 updated from v2.9.3 to v2.9.4
  • github.com/matthewhartstonge/argon2 updated from v1.5.6 to v1.5.7
  • github.com/pion/webrtc/v4 updated from v4.2.18 to v4.2.19
  • github.com/quic-go/quic-go updated from v0.61.0 to v0.62.0
  • github.com/quic-go/webtransport-go updated from v0.12.0 to v0.13.0
  • github.com/stretchr/testify updated from v1.12.0 to v1.12.1
  • github.com/dunglas/httpsfv updated from v1.1.0 to v1.1.1
  • github.com/pion/stun/v3 updated from v3.1.6 to v3.1.7
  • github.com/pion/turn/v5 updated from v5.0.12 to v5.0.13
  • gopkg.in/yaml.v3 removed
  • go.yaml.in/yaml/v3 v3.0.5 added
  • github.com/bluenviron/mediamtx-rpicamera updated from v2.8.0 to v2.9.0
  • hls.js updated from v1.7.0 to v1.7.2

Security

Binaries are compiled from source code by the Release workflow, which is a fully-visible process that prevents any change or external interference in produced artifacts.

Checksums of binaries are also published in a public blockchain by using GitHub Attestations, and they can be verified by running:

ls mediamtx_* | xargs -L1 gh attestation verify --repo bluenviron/mediamtx

You can verify checksums of binaries by downloading checksums.sha256 and running:

cat checksums.sha256 | grep "$(ls mediamtx_*)" | sha256sum --check

  •  

v4.3.17

Fixes

  • Corrected notification and deployment log links to use the configured instance URL. #11623
  • Cleaned up orphaned helper containers when helper images used unqualified names, nested registry paths, tags, or digests. #11540 closed #11511.
  • Preserved Docker restart policies when applications, previews, databases, and service applications were stopped without removing their containers.
  • Fixed type errors when stopping applications and adding scheduled tasks.
  • Kept Docker Compose domains in sync when noindex settings changed.
  • Prevented removed Docker Compose service domains from being regenerated by magic service URL variables.
  • Preserved generated Compose variables during bulk environment variable replacement and reported blocked deletions correctly.
  • Cleared stale Traefik version data after proxies stopped or changed.
  • Prevented invalid repository URLs from producing malformed commit links.

Improvements

  • Removed app-only restart-limit enforcement from database resources so databases continued to follow their configured Docker restart behavior.
  • Made missing required environment variables directly accessible from a service's disabled Deploy action.
  • Hid Coolify-managed Compose variables from the developer environment variable view to prevent accidental edits.

What's Changed

  • fix: build notification and deployment log links from the instance url by @peaklabs-dev in #11623
  • fix(docker): reap orphaned helper containers regardless of registry by @kashik0i in #11540

New Contributors

Full Changelog: v4.3.16...v4.3.17

  •  

Bitfocus Companion v5.0.5

πŸ“¦ Downloads available at

πŸ’΅ Donate to the project at

Companion v5.0.5 - Release Notes

🐞 BUG FIXES

  • variables not being updated in feedbacks or localvariables in presets
  • hidden elements not being invalidated when variables/dependencies change #4380
  • catch variable changes that happen during async getDrawStyle #4380
  • ensure ui font metrics are cleared after fonts are loaded
  • feedbacks not updating while editing button in ui
  • limit number of in flight updates/upgrades to each connection
  • yield during import to ensure connections dont timeout
  • loosen variable name rule
  • preserve add entity modal expanded collections #4433
  • UI Crash in TextInputField when label is not a string #4435
  • exclude copyleft packages from offline bundle

Full Changelog: v5.0.4...v5.0.5

  •  

v4.3.16

Fixes

  • Corrected internal routing and proxy labels for Docker Compose applications and previews to use each service's configured port, with the application port as a fallback.
  • Restored the unsaved-changes indicator when switching label management to manual mode by updating Livewire. (#11612, closes #11265)
  • Routed Telegram alerts for outdated Traefik versions to the configured topic instead of the main chat. (#11526)
  • Corrected the file and directory deletion confirmation text. (#11541)

Improvements

  • Ran stuck-resource cleanup in the background at 03:17 each day so it no longer blocked other scheduled tasks.
  • Displayed the API token's one-time visibility warning directly beside the generated token.

What's Changed

Full Changelog: v4.3.15...v4.3.16

  •  

v4.3.15

Features

  • Added per-domain internal port overrides for applications, Docker Compose services, and preview deployments across Traefik and Caddy. Public domain URLs remained portless, while the UI showed effective ports and warned about unrecognized ports. (#11594)
  • Consolidated service database, volume, and directory backups into one page with schedule editing, on-demand runs, combined history, live status, downloads, and imports. (#11574)
  • Added domain management and DNS status checks for preview deployments.

Fixes

  • Blocked read-only team members from directly invoking protected Livewire mutations for credentials, servers, applications, databases, and security resources. (#11596)
  • Preserved every application domain in COOLIFY_URL and COOLIFY_FQDN, including multi-domain configurations with ports. (#11527, fixes #10824)
  • Kept stopped containers visible after they reached their restart limit, prevented further automatic restarts, and added retry deployment and container removal actions. (#11566, closes #10624, #10906, and #11521)
  • Rejected invalid build-time environment variable names before builds started and reported the offending key with rename guidance. (#11575)
  • Prevented unauthorized users from receiving stored private keys and GitHub App secrets in Livewire state.
  • Restricted web terminal SSH commands to approved hosts, keys, ports, and options.
  • Preserved existing domains when switching an application to Docker Compose and waited for confirmation before loading its Compose file.
  • Redirected immediately after resource deletion while cleanup continued after the response.

Improvements

  • Improved the Docker Compose editor layout on mobile screens.
  • Warned before removing a port required by a service domain.
  • Warned that full PostgreSQL restores could overwrite administrator passwords.
  • Reduced the remotely callable Livewire API and kept authorization checks on user-facing write actions. (#11578)

What's Changed

New Contributors

Full Changelog: v4.3.14...v4.3.15

  •  

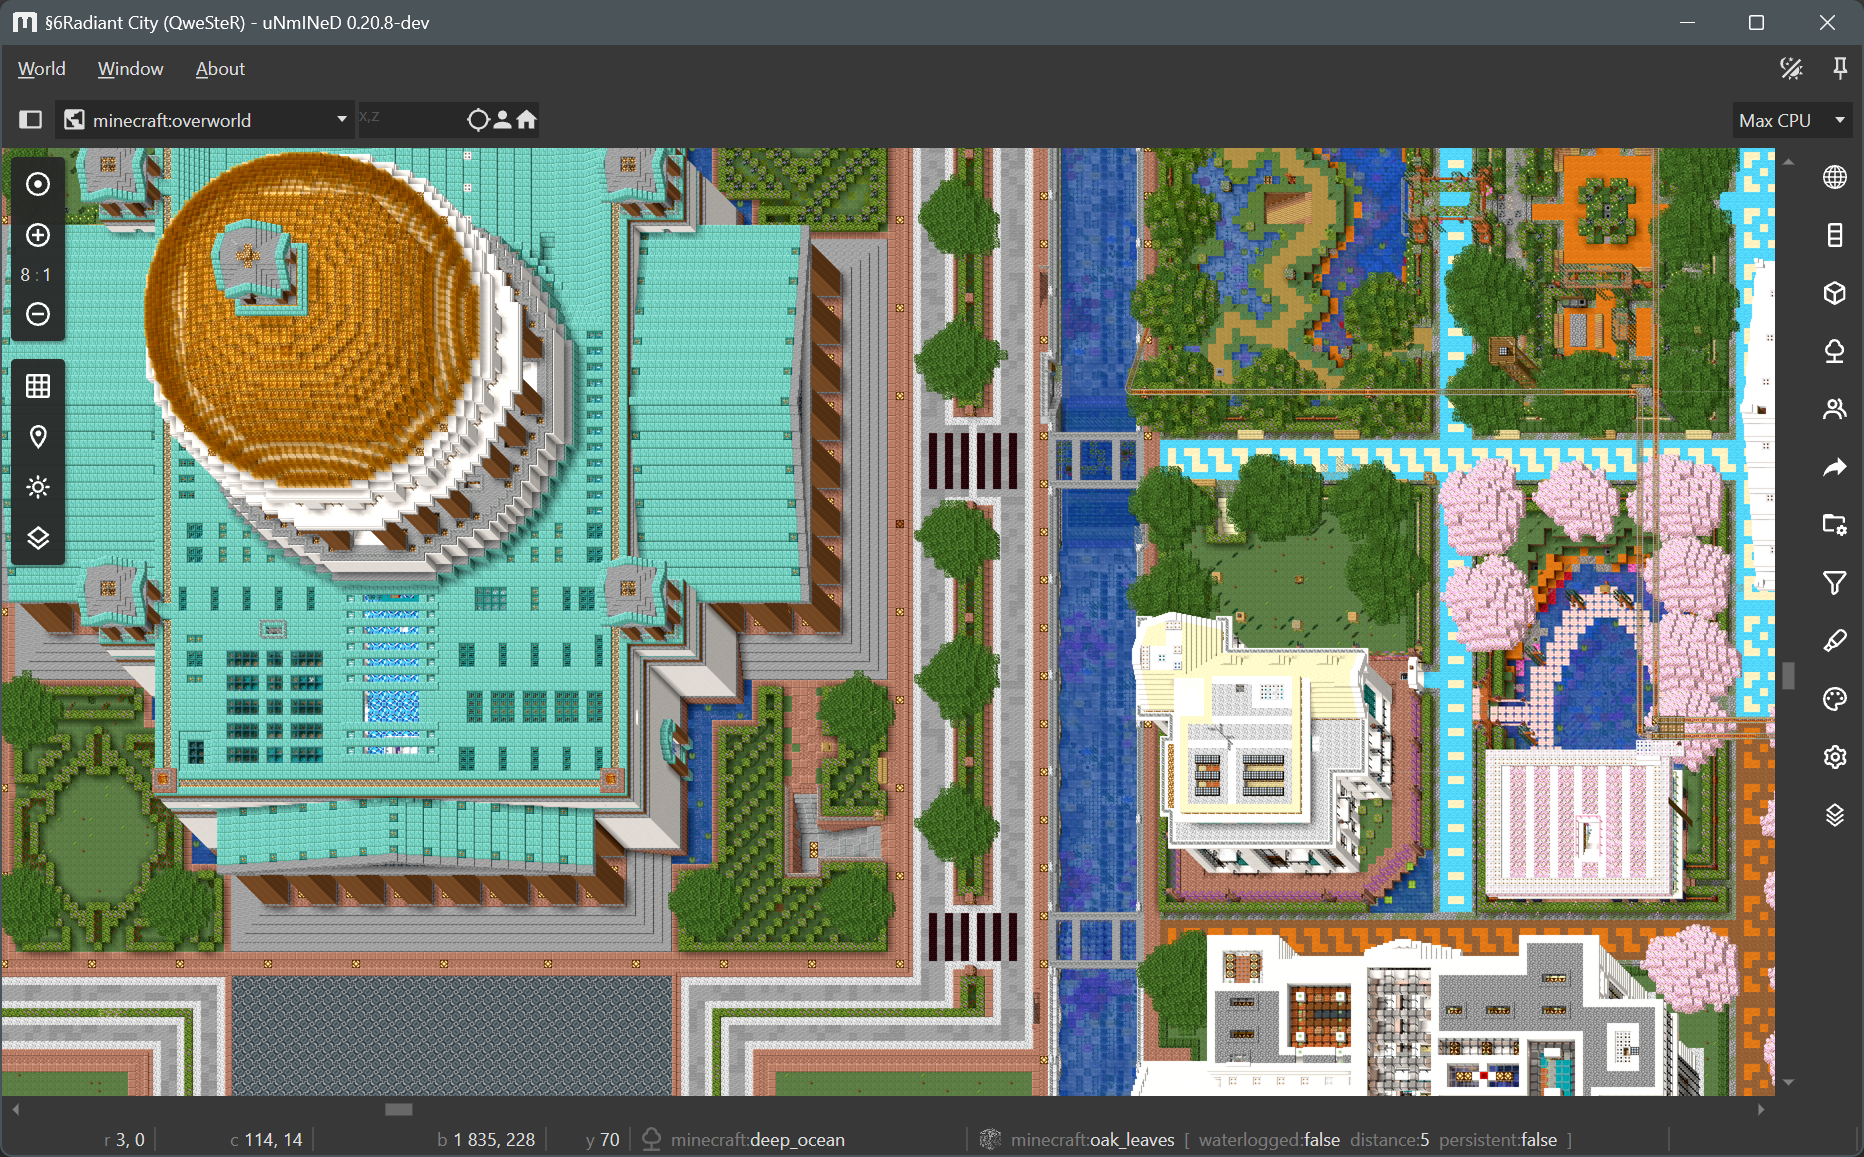
uNmINeD 0.20.8-dev

New uNmINeD development snapshot is available for download!

Changes:

  • Fixed support for Bedrock worlds with missing LevelDB log file
  • Added support for Bedrock sections without biome information
  • (Isometric) Added horizontal and vertical north directions (using cabinet projection)
  • (Isometric) Speed and memory optimizations
  • (Isometric) Fixed broken north direction buttons (broken in 0.20.7)

Cabinet projection:

  •  

v0.16.20

[0.16.20] - 2026-08-30

If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.

Added

  • System for Cross-domain Identity Management (SCIM) v2 (Enterprise):
  • JMAP: CalendarEvent/set support for updating and deleting synthetic ids (#2925).
  • Calendar:
    • Conference links in calendar invites and email alarms.
    • Translations for Arabic, Brazilian Portuguese, Bulgarian, Chinese Simplified, Chinese Traditional, Croatian, Czech, Finnish, Hebrew, Hindi, Hungarian, Indonesian, Japanese, Korean, Lithuanian, Norwegian BokmΓ₯l, Persian, Romanian, Russian, Slovak, Slovenian, Thai, Turkish, Ukrainian and Vietnamese.

Changed

  • Calendar: Updated HTTP RSVP page.

Fixed

  • DANE:
    • TLSA records are looked up whenever the MX RRset is signed, even when the MX host's own zone is not.
    • Mandatory DANE failures are permanent rather than temporary, bouncing messages that should be delayed.
    • Valid but unusable TLSA records fall back to the configured TLS strategy, permitting cleartext delivery where TLS is required.
  • S3: Fix outdated upstream af-south-1 region configuration.
  • Setup wizard: SQL directories set to use the main data store are now validated against the data store being configured.
  • CardDAV: Delete default address book id when deleting the default address book.
  • Redis: Sentinel deployments configured with rediss:// URLs now connect to the master over TLS instead of silently falling back to cleartext.
  • Email: Generated Message-ID headers use the hostname of the node that built the message instead of the configured server hostname.
  • MTA:
    • Do not send DMARC reports to local domains.
    • Messages addressed to an inboundReportAddresses match are only discarded when they actually contain a report (#1088).
  • Directory: Impersonation using the recovery admin fails when the impersonated account has not logged in before (LDAP and SQL directories).
  • WebUI: Failed logins open the browser's native credential prompt.
  • Cluster: Expired node id leases are released periodically rather than only during startup, so entries for removed nodes no longer remain Stale or Inactive indefinitely.

Check binary attestation here

  •  

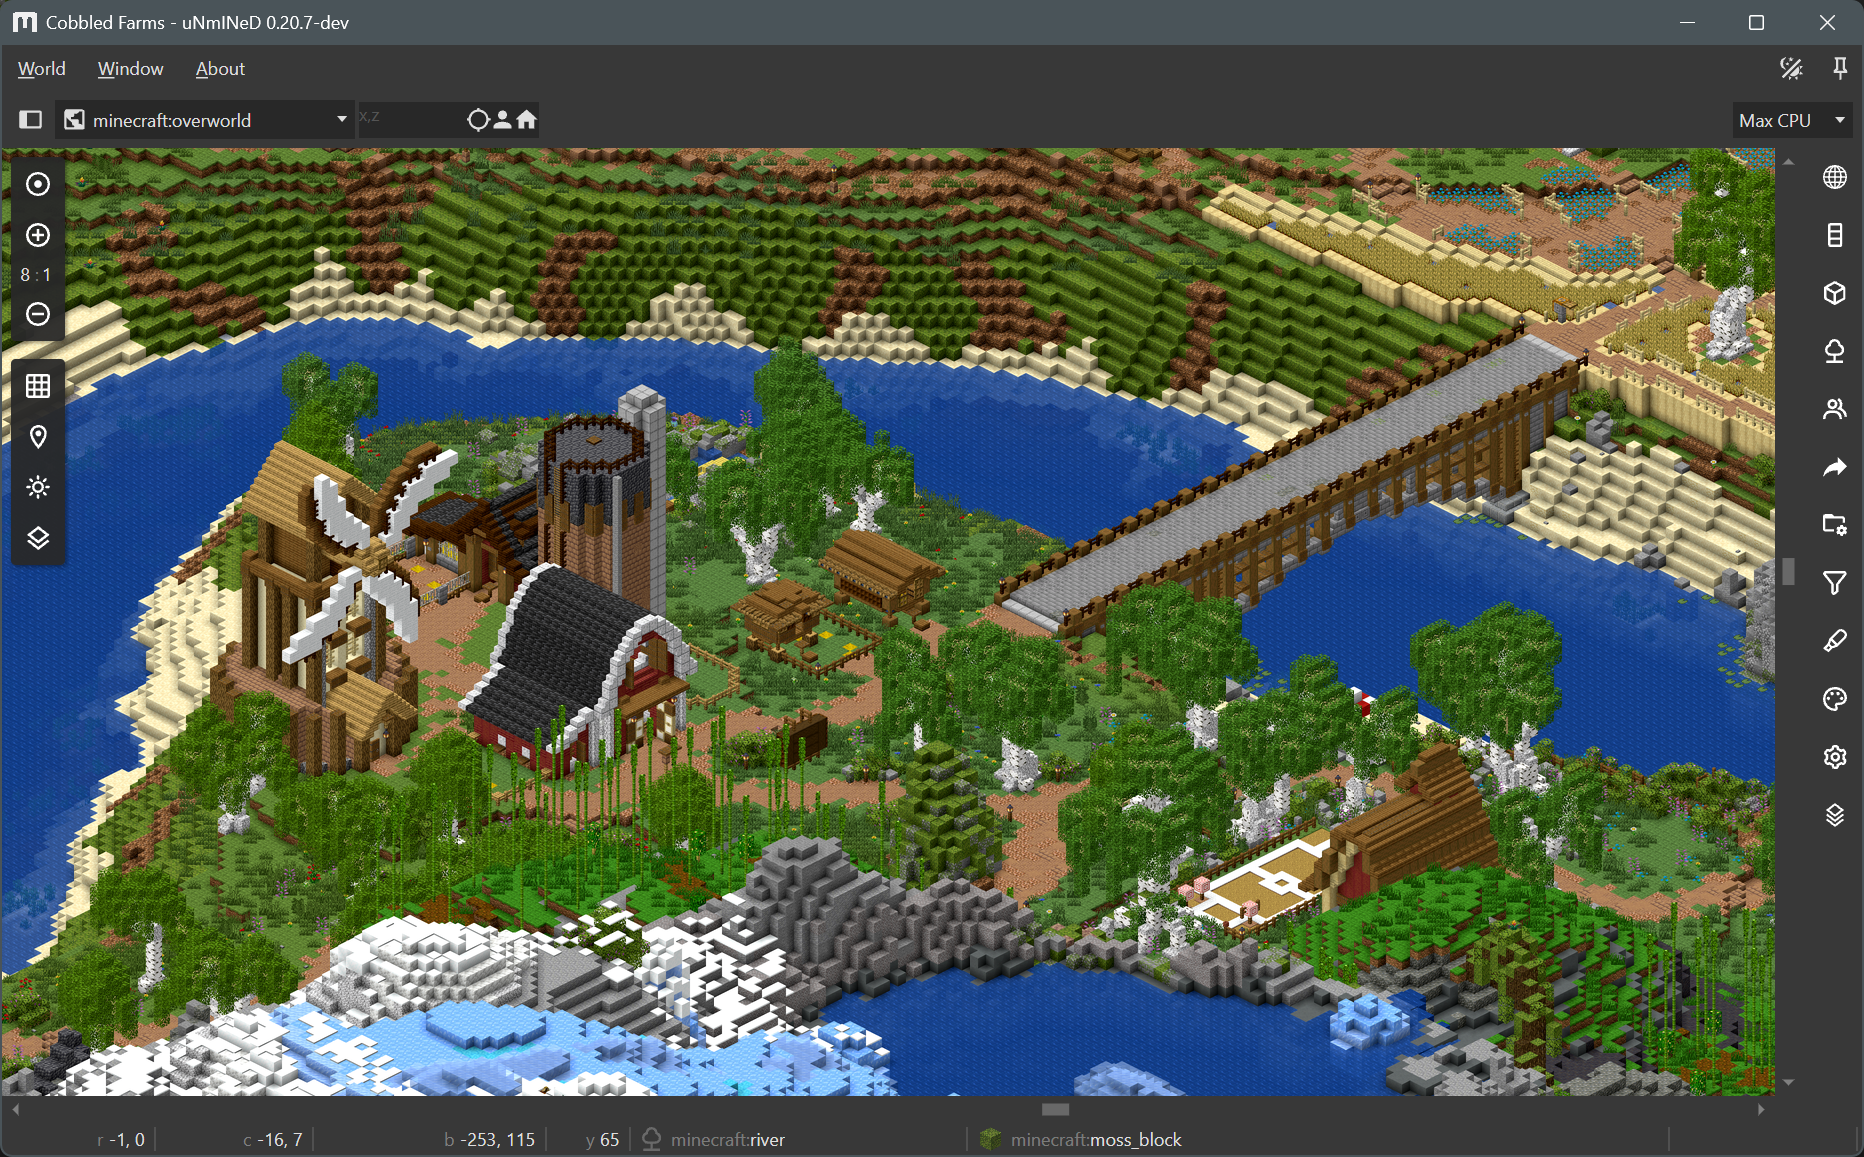
uNmINeD 0.20.7-dev

New uNmINeD development snapshot is available for download!

Changes:

  • (Isometric) Moved isometric settings to a separate tab
  • (Isometric) Added gamma and contrast settings (brighter and more vibrant images)
  • (Isometric) Added water transparency and depth fading settings
  • (Isometric) Biome blending is now ON by default
  • (Isometric) Fixed rendering queue cancellation
  • (Isometric) Fixed high IO pressure during rendering
  • (Isometric) Rendering speed optimizations

Screenshot:

  •  

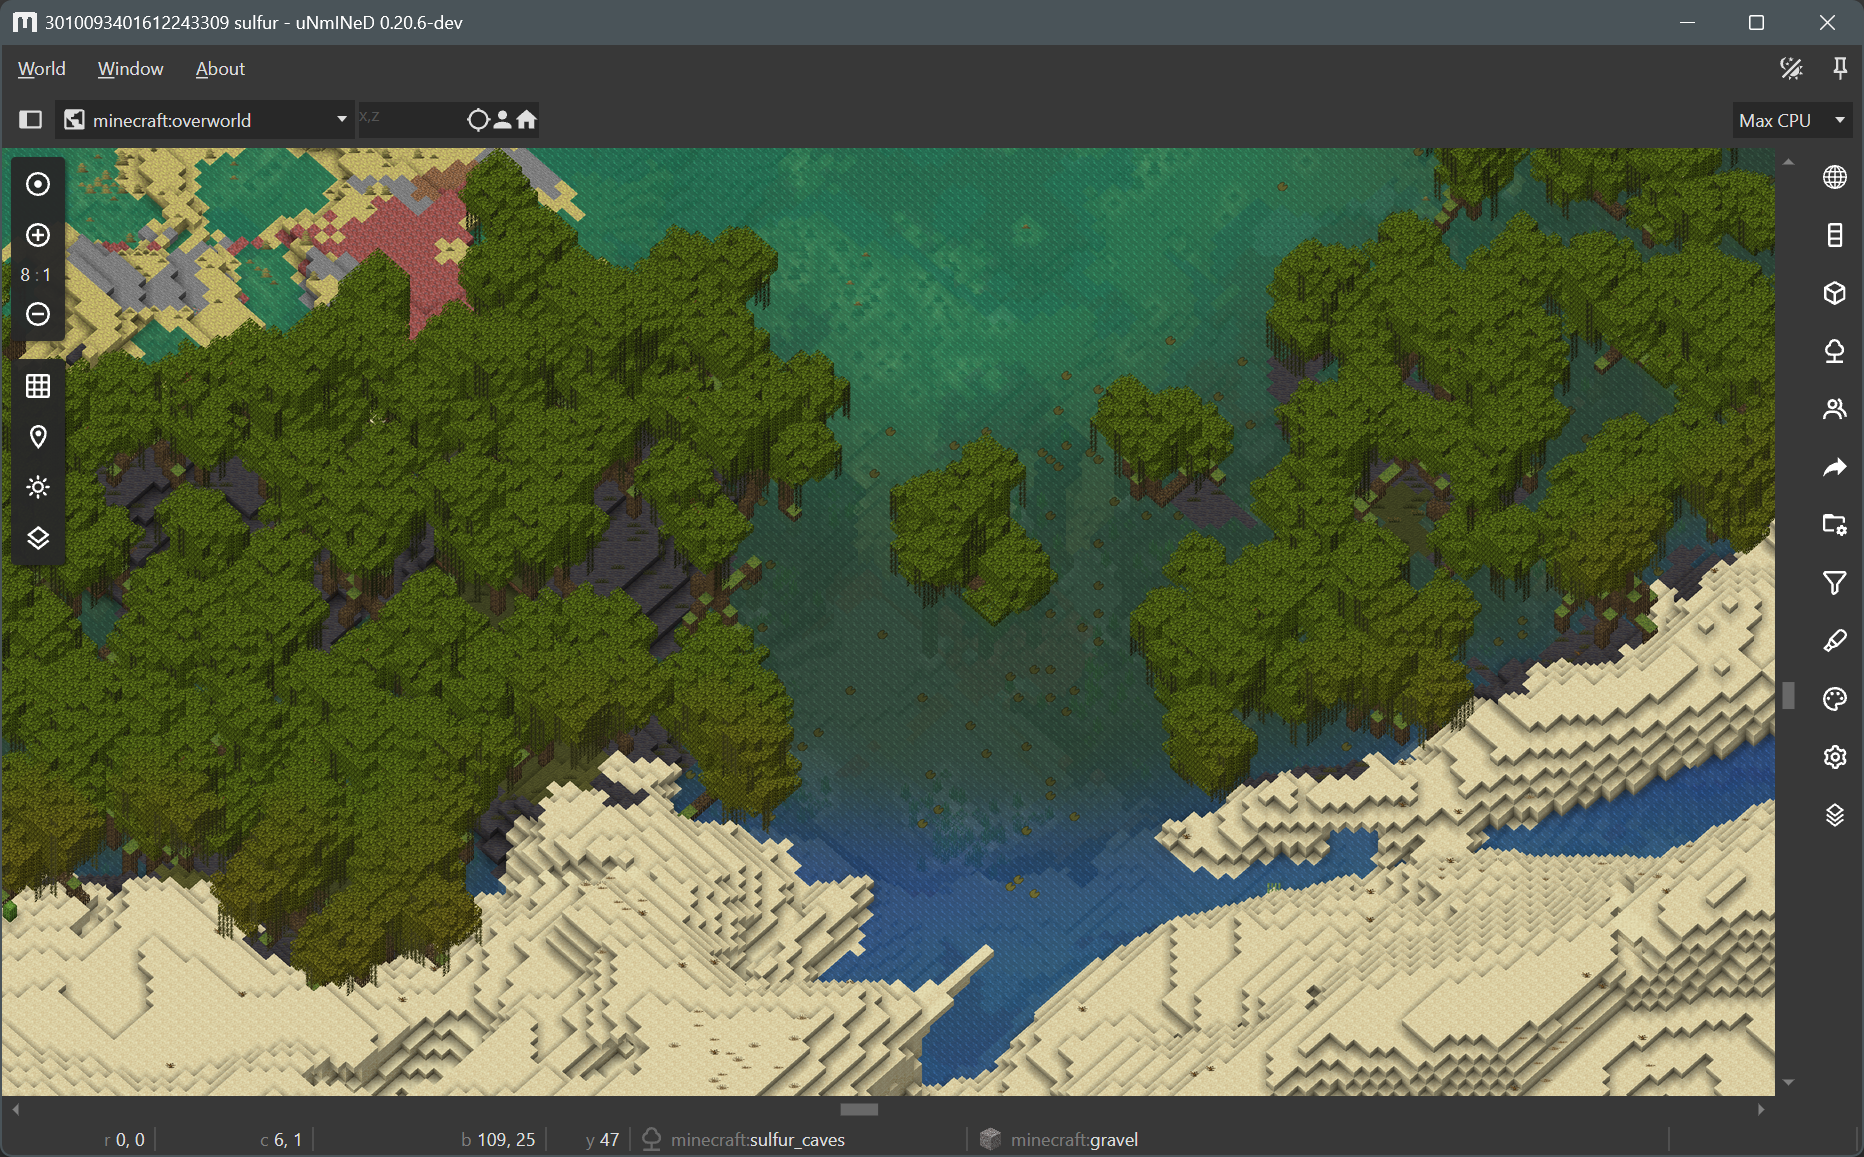
uNmINeD 0.20.6-dev

New uNmINeD development snapshot is available for download!

Changes:

  • Improved Java Edition datapack error handling and logging
  • (Isometric) Speed optimizations
  • (Isometric) Ambient occlusion shading now works at chunk borders
  • (Isometric) Added water transparency
  • (Isometric) Added support for waterlogged blocks
  • (Isometric) Added support for transparent textures
  • (Isometric) Added biome tint blending

Transparent water and smooth biome borders:

  •  

Release v2.4.5

You can install pre-built binaries from https://repo.dovecot.org/

Docker images can be found at https://hub.docker.com/r/dovecot/dovecot

Please review https://doc.dovecot.org/2.4.4/installation/upgrade/2.3-to-2.4.html and https://doc.dovecot.org/2.4.4/installation/installation.html.

Important

There are experimental features in 2.4, one is enabled with --enable-experimental-mail-utf8, and another with --enable-experimental-imap4rev2, and you also need to set mail_utf8_extensions=yes and imap4rev2_enabled=yes to enable them in config.

Critical bug fixes

  • CVE-2026-27852: Messages with a huge number of From/To/Cc/etc email addresses
    could result in excessive memory usage.
  • CVE-2026-33263: Submission: Login service crashes with panic once
    mail_max_userip_connections limit is reached.
  • CVE-2026-33604: The SMTP outbound dot-stuffing mechanism does not properly
    escape dots following a bare \r in message bodies, potentially allowing
    spoofed emails via malicious end-of-DATA injection.
  • CVE-2026-33606: Mail content stored by a user can be crafted so that it is
    interpreted as dsync protocol commands when an administrator later runs dsync
    with the stream protocol, for example during a migration.
  • CVE-2026-33607: IMAP LIST command could be used to cause excessive CPU usage.
  • CVE-2026-40014: IMAP THREAD command could have used excessive amount of CPU
    processing a single email with a massive number of Message-IDs in References
    header.
  • CVE-2026-40015: Invalid IMAP command sent to imap-hibernate process might
    crash it.
  • CVE-2026-40017: IMAP THREAD command could have used excessive amount of CPU
    processing emails with a large number of specially crafted Message-IDs in
    References header. The fix requires a new dovecot.index.thread file format,
    which is enabled only after setting dovecot_storage_version or newer. This
    rebuilds the index, so it will cause some extra CPU usage and extra
    metacache disk IO usage. It shouldn't cause (much) extra object storage IO,
    because all the fields should be coming from dovecot.index.cache.
  • CVE-2026-40203: When IMAP COMPRESS=DEFLATE was enabled, an attacker
    could send mails into a victim's mailbox and observe network traffic to
    determine whether a secret message matched a known string by comparing
    compressed response sizes (a CRIME-style attack). The fix resets the
    compression dictionary after each IMAP command, preventing information from
    leaking between commands.
  • CVE-2026-40205: If multiple OAUTH scopes were required, then
    this could have been only partially enforced with certain
    configurations.
  • CVE-2026-4200: XCLIENT FORWARD allows to forward key only passdb
    fields without the "forward_" prefix which allows connections from
    trusted networks to set nopasswd field which allows to skip the
    authentication.
  • CVE-2026-42391: Pre-login IMAP ID command could have used excessive
    amount of memory, causing the process to become killed and disconnecting
    all the other IMAP connections being proxied by the process. Or
    alternatively it could have caused excessive CPU usage, slowing down
    all the other IMAP connections being proxied by the process.
  • CVE-2026-42392: If URLAUTH is enabled, sending an invalid IMAP URLFETCH
    can result in an untagged NO response containing uninitialized memory,
    potentially leaking sensitive data.
  • CVE-2026-42393: Doveadm password length or API key length could still
    be determined via timing based attacks.
  • CVE-2026-42395: XCLIENT FORWARD command from login_trusted_networks
    could have been used to cause login processes to crash.
  • CVE-2026-52681: Sieve resource usage (sieve_max_cpu_time) was tracked
    in the active Sieve binary. Switching to a different active binary
    could have been used to reset (bypass) the resource usage.
  • CVE-2026-52687: Using IMAP COMPRESS ZSTD command can cause excessive
    memory usage in imap-login process, possibly making it reach vsz_limit
    and kill all the connections being served by the process. Fixed by
    disabling COMPRESS command with all other compression algorithms than
    the standard DEFLATE.
  • CVE-2026-73208: In oauth2, scope/aud checking was done with JWT tokens.
    Now it requires all scopes.
  • CVE-2026-73209: Sending IMAP COMPRESS package containing zero-length
    frames crashes imap or imap-login process.

Changes

  • auth: SIGHUP no longer flushes the passdb cache and SIGUSR2 no longer
    logs cache statistics. Use "doveadm auth cache flush" and the new
    "doveadm auth cache status" instead.
  • auth: The OTP authentication mechanism, the {OTP} password scheme and
    the passdb set-credentials support have been removed. They were
    unmaintained and unused. This also drops the passdb_sql_update_query
    setting.
  • config: doveconf no longer prints a flat global setting when a
    top-level named filter overrides the same setting.
  • doveadm: The doveadm protocol has been bumped to v1.4. The server uses
    the newer multiplex stream format with clients supporting it. Older
    clients keep working unchanged.
  • imap: Change imap_compress_on_proxy default to yes.
  • lib-dict-extra: Increase dict client request timeout from 30s to 65s,
    so it stays above the SQL/Cassandra query timeout.
  • lib-http: HTTP requests are now parsed strictly: obsolete line folding
    (obs-fold) and a bare LF line terminator are rejected. Both are
    request desynchronization/smuggling risks. HTTP responses are still
    parsed leniently.
  • lib-storage: A '~' in a mailbox name is now escaped only when it is at
    the beginning of the mailbox name, not at the beginning of every
    hierarchy part. Directories written by older versions are migrated
    automatically while listing mailboxes.
  • lib-var-expand: Add %{time:unix} provider and the epoch, from_epoch,
    date, iso8601 and escape filters. Deprecates the old time providers.
  • lib-var-expand: The safe filter must now be the last filter in the
    chain.
  • master: Increase the timeout after config reload before killing still
    running old processes from 6s to 35s, so that lib-master can stop them
    gracefully first.

New features

  • config: Support heredoc syntax for multi-line setting values:
    key = <<EOD ... EOD. doveconf now outputs inline SET_FILE contents
    (e.g. ssl_ca) using heredoc instead of the "inline:" prefix. The
    "inline:" form is still accepted.
  • configure: Build imap-hibernate also when only kqueue notify is
    available.
  • doveadm: Add "doveadm auth cache status" command, with --reset for
    clearing the counters.
  • doveadm: dump - List all supported dump types, and print the key type
    also for KEM and unsupported keys.
  • fts-flatcurve: Add support for phrase searching. This fixes false
    positives where the searched words existed, but not as a phrase.
  • fts-flatcurve: Delete the FTS index directory also when a Maildir
    mailbox is deleted.
  • imap: Add [THROTTLED] response code to tagged replies when a plugin
    has throttled the command.
  • last-login: Add last_login_dict_fields setting for updating multiple
    dictionary fields at login.
  • lib-dcrypt: Add ML-KEM-512/768/1024 support with OpenSSL 3.
  • lib-dcrypt: Support AEAD with Dovecot key encryption.
  • lib-settings: Expand %{variables} also in strlist and boollist keys.
  • lib-sql: sqlite - Add sqlite_busy_timeout setting, default 1s.
  • login-common: Log the destination also when a proxy connection fails.
  • quota: Update quota-clone also when "doveadm quota recalc" is run.

Bug fixes

  • Fix building on systems with a signed 32-bit time_t.
  • Fix building with Lua when LUA_LIBS contains linker flags such as -L.
  • anvil: Fix busy loop eating CPU after an admin socket connection was
    disconnected.
  • auth: Fix authentication failing after a password change when the
    passdb cache entry was verified by an auth worker.
  • auth: Fix the credentials scheme of one passdb leaking into the next
    one during a multi-passdb lookup.
  • auth: oauth2 - Fix losing userdb_* fields during OAUTHBEARER
    authentication.
  • auth: passwd-file - Fix %{passdb:...} and %{userdb:...} expansion
    returning garbage or crashing.
  • config: Fix crash in "doveconf -f" for a filter that includes a @group.
  • config: Fix crash when including a default @group into a filter.
  • config: Fix hiding secrets in doveconf output.
  • config: Fix startup failures with some settings containing %{variables}.
  • configure: Fix BUILD_IMAP_HIBERNATE detection.
  • doc: solr-schema-9.xml - Add the mandatory tokenizer class attribute.
  • doveadm: compress-connect - Fix writing server input to a non-blocking
    stdout.
  • doveadm: fs delete - Fix crash with concurrent async deletes.
  • doveconf: Fix bogus "Multiple settings matched" error when stdout is
    redirected to a file that already has content.
  • dsync: Fix truncating a mailbox attribute value when it is compared to
    the local one, e.g. truncating a Sieve script.
  • dsync: backup - Mailbox attributes changed or created only in the
    destination are now reverted or deleted.
  • fts-flatcurve: Ignore index directory entries that vanish during
    iteration.
  • fts: Don't run FTS optimize on forced resync.
  • fts: build-mail - Fix accessing Content-Type header buffer out of
    bounds.
  • imap-login, pop3-login: Tolerate SASL continuations "+" without a
    trailing space when proxying authentication.
  • imap: Don't report FETCH output stream errors as
    "BUG: Unknown internal error".
  • imap: Fix hibernation always failing on FreeBSD.
  • imap: Fix panic on GETMETADATA with an invalid UTF-8 mailbox pattern.
  • imapc: Don't send SEEEN/UNSEEN to the remote server when private
    indexes are used.
  • imapc: Fix SEARCH results pointing at wrong messages after an untagged
    EXPUNGE.
  • imapc: Fix SORT returning an empty result when search criteria were
    used.
  • imapc: Fix crash when copying a mail that was already expunged in the
    source mailbox.
  • imapc: Fix stale SEARCH/SORT results after a STORE in the same
    session.
  • imapc: Honor imapc_features=no-search also for SORT.
  • imapc: Properly handle search criteria that can be sent to remote server.
  • lib-dcrypt: Don't panic on key algorithms the backend doesn't support.
  • lib-dcrypt: Fix x9.62 ECDSA signatures randomly failing verification.
  • lib-dict-backend: cdb - Fix use-after-free of the returned key.
  • lib-dns-client: Fix handling of a disconnect initiated by the
    dns-client service.
  • lib-fs: Fix panic in fs_write_stream_abort(), e.g. when the disk is
    full during FTS indexing.
  • lib-index: Fix "File is already open" error when appending to the
    transaction log while another process is rotating it. This showed up
    as "NO [SERVERBUG] Internal error occurred." without any logging.
  • lib-ldap: Fall back to system default CA paths, needed for OpenLDAP
    built against GnuTLS.
  • lib-mail: istream-binary-converter - Fix heap use-after-free with a
    bodyless MIME part.
  • lib-mail: message-parser - Fix out of bounds read with an empty
    preamble, fix skipping the epilogue boundary line, and degrade to a
    re-parse instead of panicking with an inconsistent cached MIME tree.
  • lib-master: Fix kick reason when the KICK-USER-SIGNAL command arrives
    late, which logged "Killed with signal 15" instead of "User kicked".
  • lib-oauth2: jwt - Fix use-after-realloc, guard against an empty body
    segment and percent-encode bare "." and ".." identifiers.
  • lib-program-client: Fix panic upon irregular termination.
  • lib-settings: Fix sorting of the settings history, which caused
    changed defaults and renames to be ignored once a plugin registered
    its own history, if dovecot_config_version has been set to greater
    than 2.4.0.
  • lib-smtp: Fix assert with an empty broken localpart.
  • lib-smtp: xclient - Reject an invalid HELO parameter with 501.
  • lib-sql: pgsql - Fix binary field values for rows after the first.
    This mainly affected dict-sql maps with hexblob fields.
  • lib-ssl-iostream: Fix crash at process exit with OpenSSL 4.0.
  • lib-storage: Don't log an error when the client resets the connection
    while saving a mail.
  • lib-storage: Fix crash when reverting a failed mailbox deletion.
  • lib-storage: Fix decoded size calculation for base64 attachments,
    which could delete the cache record of a mail with a detached
    attachment.
  • lib-storage: Fix handling escaped mailbox names in the mailbox list
    index.
  • lib-storage: Fix rewriting non-NFC subscriptions with mUTF-7 storage
    names, which caused repeated rename errors.
  • lib-storage: Fix searching flags when the view is not up to date. This
    broke e.g. a pipelined UID STORE +FLAGS \Deleted followed by UID
    EXPUNGE.
  • lib-storage: Fix the mailbox vsize header not being repaired when it
    is corrupted, causing wrong mailbox sizes to be reported.
  • lib-storage: thread - Fix panic when running IMAP THREAD in multiple
    connections in parallel.
  • lib-var-expand: Reject an empty separator in the index filter, which
    caused an infinite loop.
  • lib: Fix crash and out of bounds reads when decoding IDN addresses.
    Reachable only with the experimental mail UTF-8 support enabled.
  • lib: ioloop - Fix panic and delayed timeouts when time moves forwards.
  • lib: ostream-multiplex - Fix stalls, busy loops and a panic when
    streaming data through a multiplexed connection, e.g. IMAP FETCH
    through a login proxy or TLS connections.
  • login-common: Fix connection hanging if an ostream write failed. This
    happened at least with HAProxy health check connections.
  • login-common: Fix real_remote_ip being looked up incorrectly.
  • login-common: Reject proxy credentials with ASCII control characters.
  • login-proxy: Fix "doveadm kick" for proxied connections in
    high-security mode, and log "Kicked by admin" as the reason.
  • maildir: Fix random SEARCH failures when another session concurrently
    expunges mails.
  • quota: Fix maildir quota dropping to zero after IMAP MOVE or REPLACE.
  • submission-login: proxy - Fix crash and unbounded memory usage with a
    multi-line or malformed AUTH reply from the backend.

  •  

v4.3.14

Fixes

  • Fixed standalone Docker destination setup on non-Swarm servers by creating networks with Docker's default bridge driver instead of the Swarm-only overlay driver.

Full Changelog: v4.3.13...v4.3.14

  •  

v4.3.13

Features

  • Added a one-click Executor service template with persistent storage and health checks (#11530).

Improvements

  • Served profile avatars and project icons directly from configured S3 storage or an optional CDN, with local routes as a fallback.

Fixes

  • Fixed missing service logos in global search and the service catalog by retrying a remote source before showing the default icon.
  • Gave Sentinel startup migrations enough time to finish before Docker health checks could restart the container.
  • Fixed stale Livewire keys and refresh races that could leave domain, storage, file, log, proxy, and scheduled job controls unresponsive after list changes.
  • Preserved PostgreSQL init script identity when files were renamed.
  • Rejected single-label hostnames in application and service domains while continuing to accept IP addresses.
  • Preserved custom application container names during consistent deployments and removed containers left under legacy generated names.
  • Fixed navigation after deleting or converting services, backups, scheduled tasks, sources, storage, and destinations.

What's Changed

Full Changelog: v4.3.12...v4.3.13

  •  

Asterisk Release 22.11.0

The Asterisk Development Team would like to announce
the release of asterisk-22.11.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/22.11.0
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 22.11.0

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-22.11.0

Links:

Summary:

  • Commits: 39
  • Commit Authors: 16
  • Issues Resolved: 28
  • Security Advisories Resolved: 0

  •  

Asterisk Release 23.5.0

The Asterisk Development Team would like to announce
the release of asterisk-23.5.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/23.5.0
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 23.5.0

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-23.5.0

Links:

Summary:

  • Commits: 39
  • Commit Authors: 16
  • Issues Resolved: 28
  • Security Advisories Resolved: 0

  •  

Asterisk Release 20.21.0

The Asterisk Development Team would like to announce
the release of asterisk-20.21.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/20.21.0
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 20.21.0

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-20.21.0

Links:

Summary:

  • Commits: 39
  • Commit Authors: 16
  • Issues Resolved: 28
  • Security Advisories Resolved: 0

  •  

uNmINeD 0.20.5-dev

New uNmINeD development snapshot is available for download!

Changes:

  • Right click menu items now work in isometric mode
  • Fixed isometric block rotation mismatches (mushroom blocks, logs)
  • Fixed isometric tile rendering failures (broken in 0.20.4)
  • Fixed isometric tile pixel alignment glitches (sometimes there was an one pixel gap between tiles)
  •  

v4.3.12

Fixes

  • Applied authentication rate limits per real client behind reverse proxies and Cloudflare, preventing visitors from sharing one rate-limit bucket (#11515).
  • Reset a server's unreachable counter after a successful connection check, preventing stale failures and false unreachable alerts (#11417, closes #11416).
  • Corrected placeholder alignment in code editor fields (#11514, closes #11420).
  • Queued Cloud registration verification emails with retries, making delivery more reliable.

What's Changed

New Contributors

Full Changelog: v4.3.11...v4.3.12

  •  

uNmINeD 0.20.4-dev

New uNmINeD development snapshot is available for download!

Changes:

  • Optimizations for isometric mode (more speed, reduced memory usage)
  • Isometric mode is now available from zoom 1:1 to 16:1
  • Fixed KeyNotFoundException when rendering zoom-out tiles for web
  •  

v4.3.11

Features

  • Added asynchronous DNS validation for application and service domains.
  • Added one-click service templates for HashiCorp Vault and Obsidian LiveSync CouchDB.

Fixes

  • Restored proxy connections to project networks after host reboots (#11476, fixes #11436).
  • Applied custom Docker options when applications used custom container names, honored selected rollback tags, and respected Compose stop grace periods (#11479, #11480, #11498).
  • Restored custom-format PostgreSQL backups with pg_restore (#11481, fixes #11459).
  • Removed persistent volumes when deleting application previews (#11455, fixes #11441).
  • Made Docker cleanup safe to retry and prevented missing resources from failing deletion (#11463).
  • Fixed registry pushes by updating the helper image's Docker CLI, Compose, and Buildx versions (#11461, fixes #11437).
  • Fixed service log lookup when Docker label values contained commas (#11477, fixes #11454).
  • Allowed system-wide GitHub Apps to work across teams and accepted Coolify CUIDs when updating their private keys through the API (#11453, #11468).
  • Allowed teams with unused private keys or system-wide Git sources to be deleted without removing shared sources (#11499, #11500, fixes #11494).
  • Restored clickable commit links in deployment logs (#11495, fixes #11482).
  • Cleared stale Traefik branch-upgrade warnings after the suggested branch was applied (#11496, fixes #11490).
  • Kept private-key edit dialogs working after multiple keys were deleted (#11497, fixes #11487).
  • Fixed terminal container selection when identical container names existed on different servers.
  • Refreshed service configuration after required environment variables changed.
  • Redacted dotted GitHub tokens from exported logs and prevented wide tables from overflowing their containers.

Improvements

  • Showed a toast with retry guidance when infrastructure-related Livewire requests failed.
  • Distinguished proxy restarts from proxy updates in server status indicators.
  • Made stuck-resource cleanup scalable, scheduled it automatically, and made resource deletion metadata updates atomic.

New Contributors

Full Changelog: v4.3.10...v4.3.11

  •  

MariaDB Server 12.3, 11.8, 11.4 and 10.11 – Q3 2026 Maintenance Releases, and Goodbye 10.6

MariaDB Server maintenance releases are here! On August 24, we released updates for our four currently maintained Long Term Support series: As usual, these maintenance releases include bug fixes, stability improvements, and ongoing work across MariaDB Server. You can find the complete release notes and changelogs for each version: MariaDB 12.3.3 MariaDB 11.8.9 MariaDB 11.4.13 […]

MariaDB Server 12.3, 11.8, 11.4 and 10.11 – Q3 2026 Maintenance Releases, and Goodbye 10.6 appeared first on MariaDB.org

  •  

uNmINeD 0.20.3-dev

New uNmINeD development snapshot is available for download!

Changes:

  • Bedrock LevelDB log file reader optimizations (speedup for worlds with large log files)
  • Isometric mode optimizations (huge speedup, less memory usage)
  • Isometric mode now uses the block filter settings
  • Added support for Java Edition default blockstates (from 26.3-snapshot-7)
  • Upgraded to .NET 11 (preview.7)

Default blockstates

Minecraft Java Edition from version 26.3-snapshot-7 does not store blockstate properties in the world save files when referencing a default blockstate. This caused these blockstates to render incorrectly.

uNmINeD now uses a configuration file config/vanilla.defaultblockstates.java.txt to resolve default vanilla blockstate properties. If it encounters a blockstate reference without properties, it will use the default properties from the configuration file.

The configuration file only contains default blockstate information for vanilla blocks. A mod will be available later that will allow you to generate a blockstate configuration file for modded worlds.

  •  
❌