❌

Lees weergave

Stable Channel Update for Desktop

The Stable channel has been updated to 154.0.8037.92/.93 for Windows and Mac and 154.0.8037.92 to Linux which will roll out over the coming days/weeks. A full list of changes in this build is available in the Log


Security Fixes and Rewards

Note: Access to bug details and links may be kept restricted until a majority of users are updated with a fix. We will also retain restrictions if the bug exists in a third party library that other projects similarly depend on, but haven’t yet fixed.
This update includes 32 security fixes. Please see the Chrome Security Page for more information.

[TBD][551673541] Critical CVE-2026-102331: Buffer overflow in ANGLE. Reported by @mfx on 2026-08-24
[N/A][517312707] High CVE-2026-102317: Improper privilege management in Mojo. Reported by Google on 2026-05-28
[TBD][551668264] High CVE-2026-102312: UI misrepresentation in Omnibox. Reported by jodyritonga on 2026-08-24
[N/A][556789073] High CVE-2026-102313: Uninitialized resource in ANGLE. Reported by Google on 2026-09-03
[TBD][556908674] High CVE-2026-102299: Type confusion in V8. Reported by Andrew Boni on 2026-09-04
[N/A][556926296] High CVE-2026-102306: Use after free in Bluetooth. Reported by Google on 2026-09-04
[N/A][556959073] High CVE-2026-102307: Uninitialized resource in Dawn. Reported by Google on 2026-09-04
[TBD][559266114] High CVE-2026-102323: Type confusion in V8. Reported by OpenAI Codex Security (amyb) on 2026-09-10
[N/A][559727039] High CVE-2026-102303: Uninitialized resource in GPU. Reported by Google on 2026-09-10
[N/A][559737160] High CVE-2026-102311: Uninitialized resource in GPU. Reported by Google on 2026-09-10
[TBD][560062638] High CVE-2026-102300: Uninitialized resource in WebGPU. Reported by Arni Hardarson (Neonix Security) on 2026-09-11
[TBD][560233248] High CVE-2026-102326: Type confusion in V8. Reported by OpenAI Codex Security (amyb) on 2026-09-11
[TBD][560238698] High CVE-2026-102316: Use after free in Views. Reported by Xinyang Ge on 2026-09-11
[TBD][560251736] High CVE-2026-102304: Use after free in Passwords. Reported by Xinyang Ge on 2026-09-11
[TBD][560536732] High CVE-2026-102328: Type confusion in V8. Reported by OpenAI Codex Security (amyb) on 2026-09-12
[TBD][560867085] High CVE-2026-102309: Use after free in FullScreen. Reported by sean geofrey on 2026-09-13
[N/A][561994362] High CVE-2026-102325: Uninitialized resource in Skia. Reported by Google on 2026-09-15
[N/A][561997480] High CVE-2026-102308: Use after free in Views. Reported by Google on 2026-09-15
[N/A][562004351] High CVE-2026-102301: Out of bounds write in GPU. Reported by Google on 2026-09-15
[N/A][562042411] High CVE-2026-102319: Uninitialized resource in GPU. Reported by Google on 2026-09-15
[TBD][562174487] High CVE-2026-102324: Use after free in PictureInPicture. Reported by Blockian Creator of Kritt and Open-Kritt on 2026-09-15
[N/A][562279351] High CVE-2026-102318: Out of bounds read in WebGL. Reported by Google on 2026-09-16
[TBD][563297615] High CVE-2026-102329: Cross-site scripting in WebUI. Reported by chipsec on 2026-09-18
[N/A][563351482] High CVE-2026-102315: Uninitialized resource in Media. Reported by Google on 2026-09-18
[N/A][563716534] High CVE-2026-102302: Buffer overflow in V8. Reported by Google on 2026-09-19
[TBD][565328105] High CVE-2026-102321: Type confusion in V8. Reported by Taisic Yun (@taisic_) of Theori, with Xint on 2026-09-23
[TBD][554038924] Medium CVE-2026-102320: Missing authorization in CORS. Reported by Anonymous on 2026-08-28
[$1,000][477726837] Low CVE-2026-102310: Missing authorization in Payments. Reported by Autodidact on 2026-01-22
[N/A][496212975] Low CVE-2026-102327: Incorrect authorization in WebView. Reported by Google on 2026-03-25
[N/A][498793976] Low CVE-2026-102330: Incorrect authorization in SiteIsolation. Reported by Google on 2026-04-02
[N/A][514059780] Low CVE-2026-102314: UI misrepresentation in TabStrip. Reported by Google on 2026-05-17
[N/A][533021953] Low CVE-2026-102305: UI misrepresentation in SignIn. Reported by Google on 2026-07-09

We would also like to thank all security researchers that worked with us during the development cycle to prevent security bugs from ever reaching the stable channel.
Many of our security bugs are detected using AddressSanitizer, MemorySanitizer, UndefinedBehaviorSanitizer, Control Flow Integrity, libFuzzer, or AFL.


Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.


Srinivas Sista

Google Chrome
  •  

Extended Stable Update for Desktop

The Extended Stable channel has been updated to 152.0.7977.149Β for Windows and Mac which will roll out over the coming days/weeks.

A full list of changes in this build is available in the log. Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.

Srinivas Sista
Google Chrome
  •  

Firefox 157.0

New

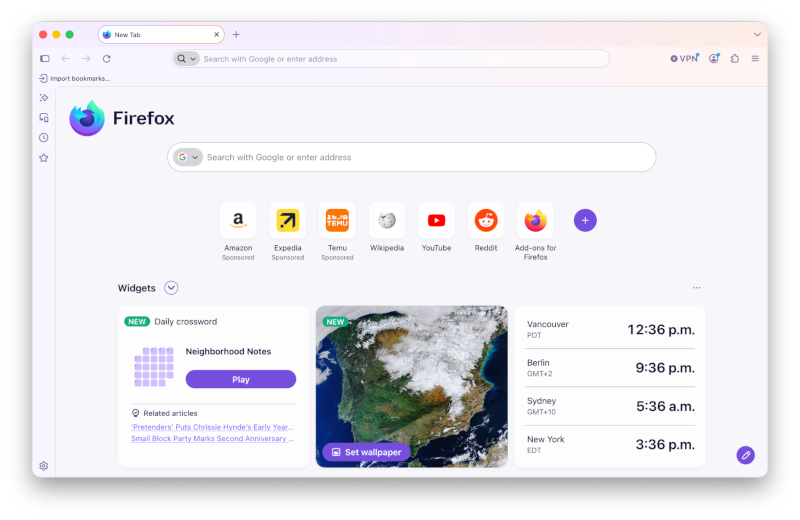
  • Screenshot of Firefox visual refresh

    Firefox's biggest visual refresh in years is now available, with a modernized look across the browser toolbars, sidebar, menus and individual features, built with our updated design system. It also includes:

    • New built-in themes with light and dark versions, to personalize the look of Firefox in one click.
    • A new compact mode that reduces toolbar and tab spacing to leave more room for web content, useful on smaller screens and in split-screen layouts.
  • WebRTC video calls can now use hardware AV1 decoding on devices that support it, instead of always decoding AV1 video in software.

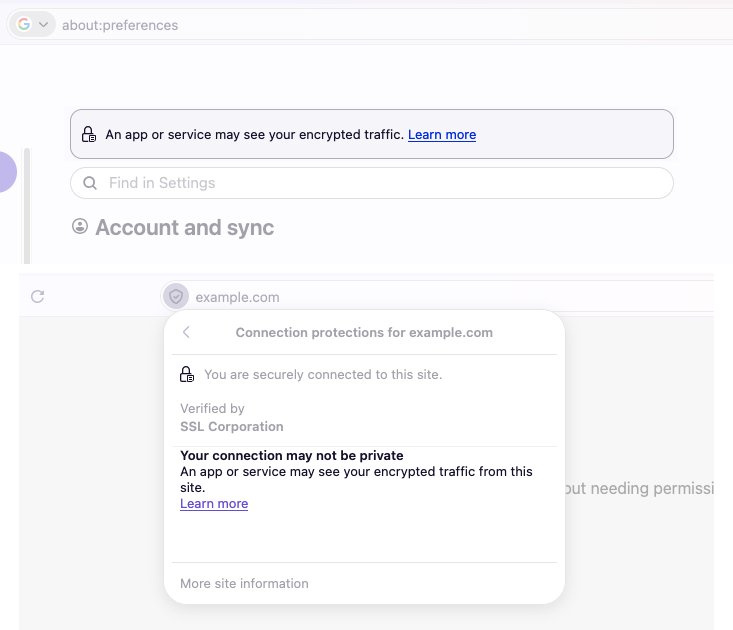
  • Firefox now shows a warning in the site information panel (the shield icon in the address bar) and in Settings when it has been set up to record its encryption keys, which could let other software on the computer read encrypted web traffic.
    Screenshot of TLS interception UI

  • Firefox Suggest now offers suggestions in the address bar in Austria, Belgium, Czech Republic, Denmark, Finland, Hungary, Ireland, Luxembourg, Netherlands, Norway, Poland, Portugal, Slovakia, Spain, Sweden, and Switzerland. They can be controlled in the Firefox Suggest settings. Learn more.

Fixed

  • Fixed video from phones and tablets appearing sideways or upside down in WebRTC calls.

  • Fixed the address bar searching for the typed text instead of opening the selected suggestion when a page was still loading, such as shortly after Firefox started.

  • Fixed some HDR videos encoded in 8-bit color formats looking dull and gray on Windows instead of displaying in HDR.

  • Improved audio and video synchronization when repeatedly changing the playback speed of videos, for example on YouTube.

  • Fixed the Vertical Tabs sidebar not reappearing when the cursor moves to the edge of the screen in full screen mode.

  • Fixed an issue on Windows where making a video full screen would leave the Windows taskbar showing over the video.

  • Various security fixes.

Changed

  • Pressing Tab now moves focus straight to the text field of the address bar and search bar instead of stopping on the search engine button first. The button can still be reached with Shift+Tab.

  • Amazon is no longer included as a built-in search engine. It can still be added as a custom search engine in the search settings. Learn more.

  • The updated sidebar is now enabled for everyone. Anyone still using the previous sidebar will keep a similar layout, with the panel switcher at the top of the sidebar. Additionally, the β€œShow sidebar” option has been removed from Settings.

    While we continue to refine the new design, the previous sidebar version can still be restored by setting sidebar.revamp to false in about:config. This also turns off vertical tabs. The preference will remain available until the end of 2027.

  • Web page alert(), confirm() and prompt() dialogs, the color and date pickers, and form autocomplete drop-downs now match the page's light or dark color scheme.

Enterprise

Developer

Web Platform

  • Firefox now supports the at-rule() function for @supports. This allows authors to detect browser support for specific at-rules, such as @supports at-rule(@scope).

  • Firefox now supports the chain value for the CSS overscroll-behavior property.

Community Contributions

  •  

v0.20.0-rc.7

❗ This is a pre-release

  • May contain bugs and unfinished features.

⚠️ Note for macOS users

Builds are unsigned (no Apple Developer ID). After dragging MarkText into Applications, clear the quarantine flag once:

xattr -cr /Applications/marktext.app

Verifying downloads

All artifacts are listed with their SHA-256 in SHA256SUMS.txt. Verify with:

sha256sum -c SHA256SUMS.txt --ignore-missing

What's Changed

  • fix: restore code block legibility and text crispness (#5539) by @Jocs in #5553
  • test: fold the two #5539 specs into one by @Jocs in #5557
  • fix(muya): keep a hard line break's glyph on the line it ends (#2094) by @Jocs in #5556
  • revert: keep grayscale antialiasing on editor text (#5539) by @Jocs in #5558
  • fix(muya): keep sequence diagram arrowheads in exported PDFs (#2423) by @Jocs in #5561
  • fix(muya): pair emphasis delimiters the way CommonMark does (#2086) by @Jocs in #5555
  • fix(muya): parse link destinations the way CommonMark does (#2377) by @Jocs in #5562
  • Add a zoom/pan viewer and image export for rendered diagrams by @Jocs in #5554
  • fix: give the editor and Preferences windows their own menu bar (#2245) by @Jocs in #5560
  • perf(muya): re-render only the two affected blocks when stepping through search (#5580) by @ycyc0421 in #5569

New Contributors

Full Changelog: v0.20.0-rc.6...v0.20.0-rc.7

  •  

Dopamine 3.0.11

[3.0.11] - 2026-09-25

Added

  • Added optional wave progress bar
  • Ctrl+F now selects all text in the search box for quick replacement
  • Added optional Stop button (Hidden by default, but can be enabled in the settings.)
  • Scroll position is now remembered when switching screens
  • Added buttons to the playback queue to clear the queue and to add the queued songs to a playlist
  • Added album release date to album image tooltips and optionally on the nog playing page
  • Added a playback speed control (Thank you @henryshuen)

Changed

  • Updated the Simplified Chinese translation (Thank you @jeremyooh)
  • Updated the Vietnamese translation (Thank you @honhatduy)

Fixed

  • Adding artist image doesn't always work
  • Crash when displaying rich lyrics of songs with a lot of artists
  • On KDE, Dopamine appears under "Lost & Found" in the application menu instead of "Multimedia" (Thank you @adem4ik).
  • Failure to index files with malformed TXXX frames

P.S.: If you enjoy Dopamine, please consider donating via PayPal or buying me a coffee. Your support keeps the music going!

  •  

OBS Studio 33.0.0 Beta 4

Beta 4 Changes

  • Fixed a CI and packaging issue. There are no application changes since Beta 1.

Beta 3 Changes

  • Fixed a CI issue. There are no application changes since Beta 1.

Beta 2 Changes

  • Fixed a versioning issue. There are no application changes since Beta 1.

33.0 New Features

  • Updated CEF from 127/6533 to 150/7871 [WizardCM] (#13900)
    • This is a massive update to the underlying framework used for browser sources and docks from the July 2024 release to September 2026
    • All of this work is on the backend and should be invisible to users. Please be sure to report any new weirdness or problems you run into with browser sources!
  • Complete overhaul to plugin loading [FiniteSingularity/PatTheMav] (#13594)
    • First-party plugins are now in a new folder named core
    • Third-party plugins have an updated installation location and folder structure
    • Existing third-party plugins will continue to load from the legacy locations until OBS Studio 34.0
    • More information is available in our knowledge base article.
  • Improved how source snapping works in the preview [Warchamp7] (#12298)
    • New visual indicator added
    • Sources now snap along the entire axis instead of only when directly touching
    • Sources no longer snap to hidden sources
  • Improved behavior of spinboxes for number values [Warchamp7] (#12337)
    • Typing is no longer mysteriously blocked in some situations
    • Numbers are no longer cut off in some situations
    • Values now update only after pressing Enter and Enter does not close the window
    • Holding Shift + Up/Down now advances multiple steps at a time
    • Dragging the cursor inside the input but outside the text itself now works properly
  • Enabled NVENC on Arm64 [RytoEX] (#13827)

33.0 Changes

  • Added a check for encoders being missing when loading a profile [derrod] (#11340)
  • Added support for newest NVIDIA Broadcast SDKs for NVIDIA Audio Effects and Video Effects [pkviet] (#13838)
  • Added hotkeys for controlling audio monitoring of a source [Warchamp7] (#13599)
  • Fixed issues with groups in Studio Mode [Warchamp7] (#11092)
    • Fixed moving sources inside a group causing them to glitch out in Program
    • Fixed moving sources inside a group showing up live in Program
  • Adjusted naming of Window Capture methods on Windows [Penwy] (#12047)
  • Improved detection of fullscreen games for Game Capture [Kira-NT] (#10880)
  • Improved transparency handling for macOS Screen Capture [jcm93] (#13030)
  • Scaled simple output recording audio bitrate by channel count [nickvonkaenel] (#13311)
  • Removed support for Ubuntu 24.04

33.0 Bug Fixes

  • Added a startup error if obs-transitions failed to load [notr1ch] (#13321)
  • Improved file splitting for Hybrid MP4/MOV [derrod] (#13386)
  • Fixed outputs getting stuck running when a bad rescale output resolution is set [suogesi] (#13375)
  • Fixed monitoring icon state getting desynced when using third-party tools or websockets [prgmitchell] (#13822)
  • Fixed potential crash when shader cache file is invalid [notr1ch] (#13538)
  • Fixed a potential crash on Linux when USB mic is removed [R0te/RytoEX] (#13922)
  • Fixed a potential crash when renaming a source with the Add Source window open [Warchamp7] (#13800)
  • Fixed a potential deadlock during video/audio tasks [exeldro] (#13579)
  • Fixed an issue with B-frame offset calculation in AMF that could cause streams to disconnect [lexano-ivs] (#13762)
  • Fixed PipeWire screencast sources being duplicated in studio mode [tytan652] (#13673)
  • Fixed a potential crash when switching off a newly created profile [Warchamp7] (#13182)
  • Fixed a source toolbar crash when source type is missing [Penwy] (#13539)

33.0 Developer Information

  • Added frontend event and output signal for replay buffer saving [Penwy] (#8955)
  • Added guidance regarding the theme system to the top of all theme files [Warchamp7] (#13733)
  • Added ability to set a file extension filter for OBS_PATH_FILE_SAVE path types [FiniteSingularity] (#10190)
  • Added obs_frontend_is_safe_mode for first-party plugins
    • Third-party plugins are not loaded at all in Safe Mode
  • Added versions to Flatpak plugin extension point [tytan652] (#13735)
  • Updated libnsgif to 1.0.0 [RytoEX] (#11178)
    • This is a breaking change for any plugins using libobs/graphics gs_image_file
  • Clarified documentation for obs_module_unload [notr1ch] (#13327)
  • Required MbedTLS 3 and exclude 4 or later [tytan652] (#13799)
  • Fixed repeated preview enable/disables not working [WarmUpTill] (#12580)
  • Only emit core signal handlers for public canvases [tt2468] (#13574)
  • Deprecated unused hidden API for sources [derrod] (#13122)
  • Deprecated APIs for audio source monitoring_type [Warchamp7] (#13599)
    • This is replaced by a new monitoring_enabled boolean

Checksums

OBS-Studio-33.0.0-beta4-Sources.tar.gz: 71f33df72e454d53c0eb1e706441e2b24c475acc3ac259b8c071e9707ad10eb7
OBS-Studio-33.0.0-beta4-Ubuntu-26.04-x86_64-dbsym.ddeb: 9be1bbd516cb9b62be1adb381be44c026f197c9c206c90d06381d4eb6baf99d4
OBS-Studio-33.0.0-beta4-Ubuntu-26.04-x86_64.deb: 055db4d5cb1099b106d67645f84bc076ad1409836a0b603a35f393e1aa063a1d
OBS-Studio-33.0.0-beta4-Windows-arm64-PDBs.zip: a1e5095bd3b20bd3703cd2a2e97dc9735f5bb08513218d463edb1e9b88376d10
OBS-Studio-33.0.0-beta4-Windows-arm64.zip: c8bdbd9963e9bbdaf5e8ffaa7536ce6edd4ac583bec560fff69a5dee532ac111
OBS-Studio-33.0.0-beta4-Windows-x64-Installer.exe: 28323560c1585d51a290984777e980ef8788cd3210f150993ccbd9ee62484d8a
OBS-Studio-33.0.0-beta4-Windows-x64-PDBs.zip: 4825a54748ff65dde606537042df5b8eae634e89bb419eb93439907e97963268
OBS-Studio-33.0.0-beta4-Windows-x64.zip: 0a6d97ed2fb4d4c4cd3669eeaf063365e89ce72b602dc101659fc135f047359e
OBS-Studio-33.0.0-beta4-macOS-Apple-dSYMs.tar.xz: 58c55f934334a51e49b26baa627da34ee60909fbc74dc1c10e8f2469b6156c92
OBS-Studio-33.0.0-beta4-macOS-Apple.dmg: ecaba68924c83e96a300ba58412da04f0f469f331f88c10e7a74c6117e6e41f3
OBS-Studio-33.0.0-beta4-macOS-Intel-dSYMs.tar.xz: cadfe8423ba34900543a68b8a394c74efce632395260386c85c3d0ba6fb969cb
OBS-Studio-33.0.0-beta4-macOS-Intel.dmg: 47461ba641b88375da22f1fd74f476277ca5156fbbf54e0536b5f0eae487e2d5

  •  

33.0.0-beta3: OBS Studio 33.0.0 Beta 3

βœ‡OBS
Door: RytoEX

Beta 3 Changes

  • Fixed a CI issue. There are no application changes since Beta 1.

Beta 2 Changes

  • Fixed a versioning issue. There are no application changes since Beta 1.

33.0 New Features

  • Updated CEF from 127/6533 to 150/7871 [WizardCM] (#13900)
    • This is a massive update to the underlying framework used for browser sources and docks from the July 2024 release to September 2026
    • All of this work is on the backend and should be invisible to users. Please be sure to report any new weirdness or problems you run into with browser sources!
  • Complete overhaul to plugin loading [FiniteSingularity/PatTheMav] (#13594)
    • First-party plugins are now in a new folder named core
    • Third-party plugins have an updated installation location and folder structure
    • Existing third-party plugins will continue to load from the legacy locations until OBS Studio 34.0
    • More information is available in our knowledge base article.
  • Improved how source snapping works in the preview [Warchamp7] (#12298)
    • New visual indicator added
    • Sources now snap along the entire axis instead of only when directly touching
    • Sources no longer snap to hidden sources
  • Improved behavior of spinboxes for number values [Warchamp7] (#12337)
    • Typing is no longer mysteriously blocked in some situations
    • Numbers are no longer cut off in some situations
    • Values now update only after pressing Enter and Enter does not close the window
    • Holding Shift + Up/Down now advances multiple steps at a time
    • Dragging the cursor inside the input but outside the text itself now works properly
  • Enabled NVENC on Arm64 [RytoEX] (#13827)

33.0 Changes

  • Added a check for encoders being missing when loading a profile [derrod] (#11340)
  • Added support for newest NVIDIA Broadcast SDKs for NVIDIA Audio Effects and Video Effects [pkviet] (#13838)
  • Added hotkeys for controlling audio monitoring of a source [Warchamp7] (#13599)
  • Fixed issues with groups in Studio Mode [Warchamp7] (#11092)
    • Fixed moving sources inside a group causing them to glitch out in Program
    • Fixed moving sources inside a group showing up live in Program
  • Adjusted naming of Window Capture methods on Windows [Penwy] (#12047)
  • Improved detection of fullscreen games for Game Capture [Kira-NT] (#10880)
  • Improved transparency handling for macOS Screen Capture [jcm93] (#13030)
  • Scaled simple output recording audio bitrate by channel count [nickvonkaenel] (#13311)
  • Removed support for Ubuntu 24.04

33.0 Bug Fixes

  • Added a startup error if obs-transitions failed to load [notr1ch] (#13321)
  • Improved file splitting for Hybrid MP4/MOV [derrod] (#13386)
  • Fixed outputs getting stuck running when a bad rescale output resolution is set [suogesi] (#13375)
  • Fixed monitoring icon state getting desynced when using third-party tools or websockets [prgmitchell] (#13822)
  • Fixed potential crash when shader cache file is invalid [notr1ch] (#13538)
  • Fixed a potential crash on Linux when USB mic is removed [R0te/RytoEX] (#13922)
  • Fixed a potential crash when renaming a source with the Add Source window open [Warchamp7] (#13800)
  • Fixed a potential deadlock during video/audio tasks [exeldro] (#13579)
  • Fixed an issue with B-frame offset calculation in AMF that could cause streams to disconnect [lexano-ivs] (#13762)
  • Fixed PipeWire screencast sources being duplicated in studio mode [tytan652] (#13673)
  • Fixed a potential crash when switching off a newly created profile [Warchamp7] (#13182)
  • Fixed a source toolbar crash when source type is missing [Penwy] (#13539)

33.0 Developer Information

  • Added frontend event and output signal for replay buffer saving [Penwy] (#8955)
  • Added guidance regarding the theme system to the top of all theme files [Warchamp7] (#13733)
  • Added ability to set a file extension filter for OBS_PATH_FILE_SAVE path types [FiniteSingularity] (#10190)
  • Added obs_frontend_is_safe_mode for first-party plugins
    • Third-party plugins are not loaded at all in Safe Mode
  • Added versions to Flatpak plugin extension point [tytan652] (#13735)
  • Updated libnsgif to 1.0.0 [RytoEX] (#11178)
    • This is a breaking change for any plugins using libobs/graphics gs_image_file
  • Clarified documentation for obs_module_unload [notr1ch] (#13327)
  • Required MbedTLS 3 and exclude 4 or later [tytan652] (#13799)
  • Fixed repeated preview enable/disables not working [WarmUpTill] (#12580)
  • Only emit core signal handlers for public canvases [tt2468] (#13574)
  • Deprecated unused hidden API for sources [derrod] (#13122)
  • Deprecated APIs for audio source monitoring_type [Warchamp7] (#13599)
    • This is replaced by a new monitoring_enabled boolean

  •  

33.0.0-beta2: OBS Studio 33.0.0 Beta 2

βœ‡OBS
Door: RytoEX

Beta 2 Changes

  • Fixed a versioning issue. There are no application changes since Beta 1.

33.0 New Features

  • Updated CEF from 127/6533 to 150/7871 [WizardCM] (#13900)
    • This is a massive update to the underlying framework used for browser sources and docks from the July 2024 release to September 2026
    • All of this work is on the backend and should be invisible to users. Please be sure to report any new weirdness or problems you run into with browser sources!
  • Complete overhaul to plugin loading [FiniteSingularity/PatTheMav] (#13594)
    • First-party plugins are now in a new folder named core
    • Third-party plugins have an updated installation location and folder structure
    • Existing third-party plugins will continue to load from the legacy locations until OBS Studio 34.0
    • More information is available in our knowledge base article.
  • Improved how source snapping works in the preview [Warchamp7] (#12298)
    • New visual indicator added
    • Sources now snap along the entire axis instead of only when directly touching
    • Sources no longer snap to hidden sources
  • Improved behavior of spinboxes for number values [Warchamp7] (#12337)
    • Typing is no longer mysteriously blocked in some situations
    • Numbers are no longer cut off in some situations
    • Values now update only after pressing Enter and Enter does not close the window
    • Holding Shift + Up/Down now advances multiple steps at a time
    • Dragging the cursor inside the input but outside the text itself now works properly
  • Enabled NVENC on Arm64 [RytoEX] (#13827)

33.0 Changes

  • Added a check for encoders being missing when loading a profile [derrod] (#11340)
  • Added support for newest NVIDIA Broadcast SDKs for NVIDIA Audio Effects and Video Effects [pkviet] (#13838)
  • Added hotkeys for controlling audio monitoring of a source [Warchamp7] (#13599)
  • Fixed issues with groups in Studio Mode [Warchamp7] (#11092)
    • Fixed moving sources inside a group causing them to glitch out in Program
    • Fixed moving sources inside a group showing up live in Program
  • Adjusted naming of Window Capture methods on Windows [Penwy] (#12047)
  • Improved detection of fullscreen games for Game Capture [Kira-NT] (#10880)
  • Improved transparency handling for macOS Screen Capture [jcm93] (#13030)
  • Scaled simple output recording audio bitrate by channel count [nickvonkaenel] (#13311)
  • Removed support for Ubuntu 24.04

33.0 Bug Fixes

  • Added a startup error if obs-transitions failed to load [notr1ch] (#13321)
  • Improved file splitting for Hybrid MP4/MOV [derrod] (#13386)
  • Fixed outputs getting stuck running when a bad rescale output resolution is set [suogesi] (#13375)
  • Fixed monitoring icon state getting desynced when using third-party tools or websockets [prgmitchell] (#13822)
  • Fixed potential crash when shader cache file is invalid [notr1ch] (#13538)
  • Fixed a potential crash on Linux when USB mic is removed [R0te/RytoEX] (#13922)
  • Fixed a potential crash when renaming a source with the Add Source window open [Warchamp7] (#13800)
  • Fixed a potential deadlock during video/audio tasks [exeldro] (#13579)
  • Fixed an issue with B-frame offset calculation in AMF that could cause streams to disconnect [lexano-ivs] (#13762)
  • Fixed PipeWire screencast sources being duplicated in studio mode [tytan652] (#13673)
  • Fixed a potential crash when switching off a newly created profile [Warchamp7] (#13182)
  • Fixed a source toolbar crash when source type is missing [Penwy] (#13539)

33.0 Developer Information

  • Added frontend event and output signal for replay buffer saving [Penwy] (#8955)
  • Added guidance regarding the theme system to the top of all theme files [Warchamp7] (#13733)
  • Added ability to set a file extension filter for OBS_PATH_FILE_SAVE path types [FiniteSingularity] (#10190)
  • Added obs_frontend_is_safe_mode for first-party plugins
    • Third-party plugins are not loaded at all in Safe Mode
  • Added versions to Flatpak plugin extension point [tytan652] (#13735)
  • Updated libnsgif to 1.0.0 [RytoEX] (#11178)
    • This is a breaking change for any plugins using libobs/graphics gs_image_file
  • Clarified documentation for obs_module_unload [notr1ch] (#13327)
  • Required MbedTLS 3 and exclude 4 or later [tytan652] (#13799)
  • Fixed repeated preview enable/disables not working [WarmUpTill] (#12580)
  • Only emit core signal handlers for public canvases [tt2468] (#13574)
  • Deprecated unused hidden API for sources [derrod] (#13122)
  • Deprecated APIs for audio source monitoring_type [Warchamp7] (#13599)
    • This is replaced by a new monitoring_enabled boolean

  •  

33.0.0-beta1: OBS Studio 33.0.0 Beta 1

βœ‡OBS
Door: RytoEX

33.0 New Features

  • Updated CEF from 127/6533 to 150/7871 [WizardCM] (#13900)
    • This is a massive update to the underlying framework used for browser sources and docks from the July 2024 release to September 2026
    • All of this work is on the backend and should be invisible to users. Please be sure to report any new weirdness or problems you run into with browser sources!
  • Complete overhaul to plugin loading [FiniteSingularity/PatTheMav] (#13594)
    • First-party plugins are now in a new folder named core
    • Third-party plugins have an updated installation location and folder structure
    • Existing third-party plugins will continue to load from the legacy locations until OBS Studio 34.0
    • More information is available in our knowledge base article.
  • Improved how source snapping works in the preview [Warchamp7] (#12298)
    • New visual indicator added
    • Sources now snap along the entire axis instead of only when directly touching
    • Sources no longer snap to hidden sources
  • Improved behavior of spinboxes for number values [Warchamp7] (#12337)
    • Typing is no longer mysteriously blocked in some situations
    • Numbers are no longer cut off in some situations
    • Values now update only after pressing Enter and Enter does not close the window
    • Holding Shift + Up/Down now advances multiple steps at a time
    • Dragging the cursor inside the input but outside the text itself now works properly
  • Enabled NVENC on Arm64 [RytoEX] (#13827)

33.0 Changes

  • Added a check for encoders being missing when loading a profile [derrod] (#11340)
  • Added support for newest NVIDIA Broadcast SDKs for NVIDIA Audio Effects and Video Effects [pkviet] (#13838)
  • Added hotkeys for controlling audio monitoring of a source [Warchamp7] (#13599)
  • Fixed issues with groups in Studio Mode [Warchamp7] (#11092)
    • Fixed moving sources inside a group causing them to glitch out in Program
    • Fixed moving sources inside a group showing up live in Program
  • Adjusted naming of Window Capture methods on Windows [Penwy] (#12047)
  • Improved detection of fullscreen games for Game Capture [Kira-NT] (#10880)
  • Improved transparency handling for macOS Screen Capture [jcm93] (#13030)
  • Scaled simple output recording audio bitrate by channel count [nickvonkaenel] (#13311)
  • Removed support for Ubuntu 24.04

33.0 Bug Fixes

  • Added a startup error if obs-transitions failed to load [notr1ch] (#13321)
  • Improved file splitting for Hybrid MP4/MOV [derrod] (#13386)
  • Fixed outputs getting stuck running when a bad rescale output resolution is set [suogesi] (#13375)
  • Fixed monitoring icon state getting desynced when using third-party tools or websockets [prgmitchell] (#13822)
  • Fixed potential crash when shader cache file is invalid [notr1ch] (#13538)
  • Fixed a potential crash on Linux when USB mic is removed [R0te/RytoEX] (#13922)
  • Fixed a potential crash when renaming a source with the Add Source window open [Warchamp7] (#13800)
  • Fixed a potential deadlock during video/audio tasks [exeldro] (#13579)
  • Fixed an issue with B-frame offset calculation in AMF that could cause streams to disconnect [lexano-ivs] (#13762)
  • Fixed PipeWire screencast sources being duplicated in studio mode [tytan652] (#13673)
  • Fixed a potential crash when switching off a newly created profile [Warchamp7] (#13182)
  • Fixed a source toolbar crash when source type is missing [Penwy] (#13539)

33.0 Developer Information

  • Added frontend event and output signal for replay buffer saving [Penwy] (#8955)
  • Added guidance regarding the theme system to the top of all theme files [Warchamp7] (#13733)
  • Added ability to set a file extension filter for OBS_PATH_FILE_SAVE path types [FiniteSingularity] (#10190)
  • Added obs_frontend_is_safe_mode for first-party plugins
    • Third-party plugins are not loaded at all in Safe Mode
  • Added versions to Flatpak plugin extension point [tytan652] (#13735)
  • Updated libnsgif to 1.0.0 [RytoEX] (#11178)
    • This is a breaking change for any plugins using libobs/graphics gs_image_file
  • Clarified documentation for obs_module_unload [notr1ch] (#13327)
  • Required MbedTLS 3 and exclude 4 or later [tytan652] (#13799)
  • Fixed repeated preview enable/disables not working [WarmUpTill] (#12580)
  • Only emit core signal handlers for public canvases [tt2468] (#13574)
  • Deprecated unused hidden API for sources [derrod] (#13122)
  • Deprecated APIs for audio source monitoring_type [Warchamp7] (#13599)
    • This is replaced by a new monitoring_enabled boolean

  •  

v0.20.0-rc.6

❗ This is a pre-release

  • May contain bugs and unfinished features.

⚠️ Note for macOS users

Builds are unsigned (no Apple Developer ID). After dragging MarkText into Applications, clear the quarantine flag once:

xattr -cr /Applications/marktext.app

Verifying downloads

All artifacts are listed with their SHA-256 in SHA256SUMS.txt. Verify with:

sha256sum -c SHA256SUMS.txt --ignore-missing

What's Changed

  • docs: explain how to put marktext on PATH on every platform by @Jocs in #5459
  • fix(desktop): wrap long code-block lines when exporting to PDF (#5307) by @Jocs in #5460
  • fix(desktop): restore treePathExcludePatterns filtering in the sidebar tree by @Jocs in #5461
  • fix(desktop): require deliberate movement before a tab click becomes a drag (#4895) by @Jocs in #5464
  • fix(desktop): put the unsaved dot back on the left of the title bar path (#5467) by @Jocs in #5468
  • fix(muya): render SVG images that state no size of their own (#4991) by @Jocs in #5462
  • fix(muya): bound inline math by the text column, not by its own box (#5034) by @Jocs in #5466
  • fix(muya): give every mermaid render its own id (#5023) by @Jocs in #5465
  • fix(muya): show the text cursor over the whole editable column (#5477) by @Jocs in #5478
  • feat: support pandoc's backslash TeX math delimiters (#5446) by @Jocs in #5481
  • fix(desktop): theme the table of contents text and arrows (#5094) by @Jocs in #5486
  • fix(desktop): tell the two backslash math preferences apart in the UI (#5481) by @Jocs in #5485
  • feat(export): convert Markdown to arbitrary formats via Pandoc by @dimbc in #5379
  • fix(desktop): make source mode math highlighting follow the editor (#5483) by @Jocs in #5484
  • fix(desktop): reload an unedited tab silently when its file changes on disk (#3652) by @Jocs in #5479
  • fix(muya): keep footnote definitions packed one per line as siblings by @Jocs in #5487
  • fix(muya): resolve footnote references while escapes are still visible by @Jocs in #5491
  • fix(muya): give each repeated footnote reference its own id and backref by @Jocs in #5492
  • feat(i18n): add Russian (ru) localization by @blvcknwh1te in #5496
  • test(muya): stop the deepClone spec from overflowing the stack itself by @Jocs in #5505
  • fix(i18n): give Dutch users the Dutch editor UI, and hold the language registries together by @Jocs in #5502
  • fix(desktop): resolve local link paths without decoding the document folder (#4749) by @Jocs in #5506
  • test(desktop): repoint the technical-term checks at keys that exist by @Jocs in #5503
  • i18n: improve Russian localization wording by @NeroWolfe75 in #5507
  • feat(toc): highlight active heading based on cursor position by @rkristelijn in #4345
  • docs: update verify the download instructions by @slovanos in #5511
  • fix(desktop): keep the outline title in place, and make its word-wrap preference work by @Jocs in #5514
  • perf(muya): skip a code block re-render that produces identical DOM by @Jocs in #4876
  • fix(muya): re-render a code block when the grammar it renders with changes (#5515) by @Jocs in #5516
  • fix(desktop): stop clipboard image uploads clobbering each other and mangling paths by @Jocs in #5512
  • fix(desktop): retry a save whose rename an SMB share refused (#5322) by @Jocs in #5520
  • fix(desktop): find the uploader the user installed, wherever they installed it (#5518) by @Jocs in #5519
  • fix(desktop): find pandoc the same way the uploader finds picgo (#2751) by @Jocs in #5525
  • Type the .vue CodeMirror/spell-checker handles and forbid any in .vue (#4257) by @Jocs in #5521
  • Type the editor handle as Muya, from the engine's own declarations (#4257) by @Jocs in #5533
  • Drop the legacy muya ambient bridge and its aliases (#4257) by @Jocs in #5526
  • fix(muya): select the clicked line ourselves on a triple-click (#5389) by @Jocs in #5524
  • fix(muya): take the image references from the live DOM after selecting (#5391) by @Jocs in #5534
  • fix(muya): keep an image resize released outside the window (#5393) by @Jocs in #5537
  • fix(muya): size an image from where its resize handle was grabbed (#5392) by @Jocs in #5535
  • fix(muya): cut a cross-block selection from beforeinput too (#5415) by @Jocs in #5536
  • fix: keep the export render container out of the page layout (#5541) by @Jocs in #5542
  • fix(muya): keep a wide equation from scrolling under its own tag (#4339) by @Jocs in #5540

New Contributors

Full Changelog: v0.20.0-rc.5...v0.20.0-rc.6

  •  

Paint.NET 5.2 Beta (build 9762)

​

Welcome to the first beta for the 5.2 update! This new version has new effects and also has a big focus on performance, quality-of-life, and infrastructure improvements which prepare for the big 6.0 version that will be coming later. The two biggest changes are the new FileType plugin system and the rewritten high-precision layer rendering engine. There are also 8 new effects and very experimental support for running on Wine (Linux/Mac), which we’ll get to later.

New FileType Plugin System

The original FileType plugin system dates back to 2005 with the v2.5 release. It has withstood the test of time in the sense that it still works and has provided a lot of value for a lot of people, but it has also noticeably aged poorly in ways that have prevented progress in other areas of the app. It was written at a time when .NET itself was just 3 years old and hitting its 2.0 release with generics and 64-bit support. The modern systems used in Paint.NET for component management and isolation were nowhere to be found back then. I had no clue that the project’s longevity would stretch so far into the future, nor that so many plugins would be developed!

The old FileType plugin system is tightly coupled with the Document, Layer, and Surface classes which Paint.NET also uses internally for UI and rendering purposes. They only support the 32-bit BGRA UI8 pixel format and a flat list of bitmap layers. The new FileType system works through interfaces such as IFileTypeDocument<TPixel> and ILayer<TPixel>, along with a rich and strongly-typed imaging framework providing support for a wide variety of pixel formats, pooled bitmap allocation, scaling/interpolation, quantization/dithering, format conversion, color management, and more.

Decoupling the FileType system from the internal classes means that these two systems can now evolve independently, and internal details can be abstracted away from plugins. The new plugin system has been designed to support versioning, meaning that functionality can be added or changed in the programming interfaces that are provided to plugins while maintaining compatibility for plugins that have already been published. New layer types and topologies (e.g. layer folders) can be added without breaking existing plugins, new blend modes can be introduced, and bitmap layers can finally be migrated to a tiled storage system.

Note to plugin authors: In general, plugins should provide pixel data in the image file’s original format without converting it to BGRA32. In other words, let Paint.NET handle the conversion, whether you’re supplying pixels as RGBA64, BGR24, or even an HDR format such as RGBA FP16. Paint.NET will figure out the best conversion for pixel format and color profile handling, and when expanded pixel format support is rolled out your plugin can automatically benefit from it. Note that plugins can query at runtime which pixel formats are supported and which are native, in case they do want to do the conversion themselves for whatever reason.

New Layer Rendering Engine

The old layer rendering engine has its roots going all the way back to the 1.0 release in 2004. Over the years it has migrated from C# to C for performance reasons, and then back to C# once the language and .NET’s JIT had finally caught up to (and surpassed!) the performance of the native C compiler’s code generation. However, it has no SIMD optimizations, it only has 8 bits per channel of precision (β€œUI8”), and the code was very messy and difficult to make changes to. Working with many layers can result in incorrect colors or banding artifacts as off-by-1 errors accumulate across multiple layers.Β 

With 5.2, this has been completely rewritten and upgraded to use 32-bits of floating-point precision per channel (β€œFP32”). It is fully optimized for AVX2, AVX512, and even ARM64 NEON thanks to .NET’s new platform-agnostic intrinsics support. Because FP32 uses a lot more memory bandwidth than UI8, many tricks have been employed to optimize that to the point that there is no perceptible performance reduction from previous versions (the old renderer not using any SIMD also helps this comparison). The bottleneck is compute, not memory bandwidth, and performance really shines on CPUs with AVX512 support (e.g. AMD Zen 5) even with standard dual channel memory.

A driving factor behind this change was to prepare for future versions of Paint.NET that will expand pixel format support beyond BGRA UI8. In order to do this in a sane and maintainable manner, having a canonical pixel format became important so that each rendering kernel only needs to be written once. All of the rendering kernels can now operate exclusively on FP32 data, with high-performance format conversion and color transform kernels at the beginning and end of the rendering pipeline. This will make it much easier to add application-level support for RGBA UI16, RGBA FP16, and even RGBA FP32 β€” the layer rendering engine already supports it, the rest of the app just has to catch up.

New Effects

This release adds 8 new effects. These fill in the Artistic submenu, add some new dithering capabilities, two new distortion effects, and finally support for high-quality halftoning.

  • Artistic -> Linocut
    • Simulates a relief printmaking technique where an artist carves an image into a sheet of linoleum, rolls ink onto the raised surface, and then stamps it onto paper or fabric.
  • Artistic -> Mosaic
    • This is sort of like an expanded Pixelate effect with optional beveling and grout separation between the β€œpixels.” There are numerous tiling patterns to choose from.
  • Artistic -> Pointilism
    • Simulates a painting technique where an artist applies small, distinct dots of color next to each other to form an image.
  • Artistic -> Stained Glass
    • Simulates stained glass. Similar to Distort->Crystalize, but more fleshed out.
  • Color -> Ordered Dither
    • Simple ordered dithering patterns from the Bayer, Spiral, Dual Spiral, Blue Noise, and White Noise families.
  • Distort -> Spherize
    • Similar to Distort -> Bulge, but produces an actual spherical shape.
  • Distort -> Waves
    • A very configurable effect that can produce waves, ripples, spirals, flowers, and other shapes.
  • Stylize -> Halftone
    • Simulates physical printing, such as seen in newspapers or comic books, using either CMYK or black-and-white dots. The conversions between RGB and CMYK are color space aware and operate in linear gamma space when appropriate, resulting in a very high quality result.

Examples of each new effect:

Original
image.png
Linocut
image.png
Mosaic
image.png

Pointilism
image.png
Stained Glass
image.png
Ordered Dither
image.png

Spherize
image.png
Waves
image.png
Halftone
image.png

Experimental Wine Support

NOTE: This is not for the faint of heart! It is very much experimental and targeted towards early adopters who aren’t afraid of missing functionality, performance issues, crashes, and wrestling with dependencies.

I’ve recently made major progress getting Paint.NET working on top of Wine, which means Paint.NET can now finally run on Linux and Mac. This was first made available as part of 5.2 Alpha (build 9739) and has now been moved into its own package that you can download from a separate GitHub page with its own Releases page and Issues tracker. Updates will be independent(-ish) of the main Windows packages, at least for the foreseeable future. Each new Windows release will be accompanied by a corresponding Wine release so that it doesn’t fall behind in functionality.

What’s coming in 6.0?

The next big update will introduce a new .PDN file format that will finally enable the ability to add new features to the document and layering systems. High bit-depth pixel formats, new blend modes, and layer folders are planned to be the first use of this. Later on, features such as adjustment layers, text layers, and HDR are also planned (to name just a few).

Change Log

Changes since 5.2 Alpha (build 9739) (sorry, I forgot to cross-post it to the blog):

  • New: The Eraser tool now supports selecting a Fill pattern in the toolbar.
  • Improved: When using Image->Resize and β€œMaintain aspect ratio”, the rounding has been improved to reduce the aspect ratio error
  • Fixed a bug in the Move tools where shift-clicking on a side handle (north/south/east/west) would sometimes cause it to move on its own by 1-2 pixels.
  • Fixed: The Colors window will no longer erase the hex field if an invalid character is typed.
  • Fixed the tooltips in the File -> Open Recent menu by removing them (WinForms is just very buggy here). The directory paths are now shown on a second line of text instead.
  • Renamed the β€œMove Selected Pixels” tool to β€œMove Pixels.”
  • Fixed an SEHException error message when changing the language.
  • Experimental Wine support is now in a separate package that is updated independently(-ish) of the main package. You can get it here: https://github.com/paintdotnet/Paint.NET-on-Wine
  • Updated the DDS FileType Plus bundled plugin. The Save Options dialog will now auto-check or auto-uncheck the checkboxes for enabling mipmaps or cube maps if the image was originally opened from a DDS file.

Download and Install

This build is available via the built-in updater as long as you have opted-in to pre-release updates. From within Settings -> Updates, enable β€œAlso check for pre-release (beta) versions of Paint.NET” and then click on the Check Now button. You can also use the links below to download an offline installer or portable ZIP.

image.png

You can also download the installer here (for any supported CPU and OS), which is also where you can find downloads for offline installers, portable ZIPs, and deployable MSIs.

For the experimental builds for Wine, you can go here to download them.

​

  •  

Early Stable Update for Desktop

Β The Stable channel has been updated to 155.0.8059.12/.13 for Windows and Mac as part of our early stable release to a small percentage of users. A full list of changes in this build is available in the log.

You can find more details about early Stable releases here.

Interested in switching release channels? Β Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.


Srinivas Sista

Google Chrome

  •  

Extended Stable Update for Desktop

The Extended Stable channel has been updated to 152.0.7977.140Β for Windows and Mac which will roll out over the coming days/weeks.

A full list of changes in this build is available in the log. Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.

Srinivas Sista
Google Chrome
  •  

Stable Channel Update for Desktop

The Chrome team is delighted to announce the promotion of Chrome 154 to the stable channel for Windows, Mac and Linux. This will roll out over the coming days/weeks.

Chrome 154.0.8037.57 (Linux)Β 154.0.8037.57/.58Β Windows/Mac contains a number of fixes and improvements -- a list of changes is available in the log. Watch out for upcoming Chrome and Chromium blog posts about new features and big efforts delivered in 154.

Security Fixes and Rewards

Note: Access to bug details and links may be kept restricted until a majority of users are updated with a fix. We will also retain restrictions if the bug exists in a third party library that other projects similarly depend on, but haven’t yet fixed.

This update includes 108 security fixes. Please see the Chrome Security Page for more information.

[$5,000][551573368] Critical CVE-2026-95350: Buffer overflow in ANGLE. Reported by Billy Jheng Bing Jhong, Muhammad Alifa Ramdhan, Pan Zhenpeng of STAR Labs SG Pte. LTd. on 2026-08-24

[$2,500][530045332] Critical CVE-2026-95357: Out of bounds write in GPU. Reported by Anymous on 2026-07-01

[TBD][548585299] Critical CVE-2026-95339: Use after free in ServiceWorker. Reported by Andrew Boni on 2026-08-18

[TBD][551708184] Critical CVE-2026-95281: Buffer overflow in ANGLE. Reported by Muhammad Alifa Ramdhan of STAR Labs SG Pte. Ltd. on 2026-08-24

[TBD][552665794] Critical CVE-2026-95313: Use after free in Fullscreen. Reported by WinD39 - Huynh Dinh Vu on 2026-08-26

[N/A][553172761] Critical CVE-2026-95349: Buffer overflow in WebGL. Reported by Google on 2026-08-27

[TBD][556435507] Critical CVE-2026-95284: Buffer overflow in ANGLE. Reported by Muhammad Alifa Ramdhan (STARLABS SG) on 2026-09-03

[TBD][556576992] Critical CVE-2026-95322: Out of bounds write in GPU. Reported by David Sievers (@loknop) on 2026-09-03

[N/A][559320837] Critical CVE-2026-95329: Out of bounds write in WebGL. Reported by Google on 2026-09-09

[TBD][560439699] Critical CVE-2026-95356: Use after free in WindowDialog. Reported by Xinyang Ge on 2026-09-12

[TBD][562151598] Critical CVE-2026-95310: Use after free in AdFilter. Reported by Xinyang Ge on 2026-09-16

[$5,000][540265100] High CVE-2026-95301: Missing authorization in Extensions. Reported by OGINOME Tomohito on 2026-07-29

[$5,000][543471693] High CVE-2026-95291: UI misrepresentation in SecurityIndicators. Reported by NH DEV on 2026-08-07

[N/A][508462481] High CVE-2026-95355: Incorrect authorization in Navigation. Reported by Google on 2026-05-01

[N/A][517661385] High CVE-2026-95315: Use after free in Aura. Reported by Google on 2026-05-29

[N/A][520516206] High CVE-2026-95298: Use after free in Browser. Reported by Google on 2026-06-05

[N/A][534997484] High CVE-2026-95372: Use after free in Chromecast. Reported by Google on 2026-07-15

[N/A][537857253] High CVE-2026-95324: Uninitialized resource in GPU. Reported by Google on 2026-07-22

[N/A][543141419] High CVE-2026-95283: Buffer overflow in Tint. Reported by Google on 2026-08-06

[TBD][550953039] High CVE-2026-95293: Uninitialized resource in GPU. Reported by TienPA - NGS Holdings on 2026-08-22

[N/A][553116160] High CVE-2026-95274: Improper output encoding in DevTools. Reported by Google on 2026-08-26

[N/A][553129513] High CVE-2026-95282: Use after free in Platform. Reported by Google on 2026-08-26

[N/A][553130481] High CVE-2026-95373: Use after free in DevTools. Reported by Google on 2026-08-26

[N/A][553136141] High CVE-2026-95277: Use after free in Views. Reported by Google on 2026-08-26

[N/A][554558320] High CVE-2026-95348: Use after free in Bluetooth. Reported by Google on 2026-08-29

[TBD][555299641] High CVE-2026-95335: Use after free in HID. Reported by WinD39 - Huynh Dinh Vu on 2026-09-01

[TBD][556535630] High CVE-2026-95338: Use after free in PDFium. Reported by SeungMyung Lee (@sm1ee), Siung kim (@ksw9722) on 2026-09-03

[TBD][556576976] High CVE-2026-95318: Buffer overflow in Video. Reported by alex.laboirie on 2026-09-03

[TBD][557523002] High CVE-2026-95286: Type confusion in Bindings. Reported by @bean5oup on 2026-09-05

[TBD][558764482] High CVE-2026-95365: Type confusion in IndexedDB. Reported by HoneyBee on 2026-09-08

[TBD][559815527] High CVE-2026-95343: Use after free in WebAudio. Reported by HoneyBee on 2026-09-11

[N/A][560406548] High CVE-2026-95280: Race condition in V8. Reported by Google on 2026-09-12

[TBD][560536731] High CVE-2026-95304: Out of bounds write in V8. Reported by OpenAI Codex Security (amyb) on 2026-09-12

[TBD][560536735] High CVE-2026-95306: Type confusion in V8. Reported by OpenAI Codex Security (amyb) on 2026-09-12

[N/A][561997427] High CVE-2026-95299: Use after free in GPU. Reported by Google on 2026-09-15

[TBD][562242429] High CVE-2026-95351: Use after free in Views. Reported by Xinyang Ge on 2026-09-16

[N/A][495529018] Medium CVE-2026-95287: Missing authorization in Navigation. Reported by Google on 2026-03-23

[N/A][497204165] Medium CVE-2026-95366: Use of released resource in Core. Reported by Google on 2026-03-28

[N/A][497212105] Medium CVE-2026-95382: Improper input validation in Auth. Reported by Google on 2026-03-28

[N/A][497603247] Medium CVE-2026-95381: Improper input validation in Printing. Reported by Google on 2026-03-30

[N/A][500127519] Medium CVE-2026-95331: Out of bounds write in ANGLE. Reported by Google on 2026-04-06

[N/A][501648493] Medium CVE-2026-95297: Missing authorization in Contextual Tasks. Reported by Google on 2026-04-11

[N/A][502179319] Medium CVE-2026-95375: Incorrect authorization in BrowserTag. Reported by Google on 2026-04-13

[N/A][502242455] Medium CVE-2026-95302: Incorrect authorization in WebAPKs. Reported by Google on 2026-04-13

[N/A][511791538] Medium CVE-2026-95362: Cross-site request forgery in DevTools. Reported by Google on 2026-05-10

[N/A][513049042] Medium CVE-2026-95369: Inappropriate implementation in XML. Reported by Google on 2026-05-14

[N/A][513134076] Medium CVE-2026-95376: Externally controlled reference in DevTools. Reported by Google on 2026-05-14

[N/A][513162143] Medium CVE-2026-95359: Uninitialized resource in GPU. Reported by Google on 2026-05-14

[N/A][513992281] Medium CVE-2026-95294: UI misrepresentation in Browser. Reported by Google on 2026-05-17

[N/A][514019137] Medium CVE-2026-95337: UI misrepresentation in Messages. Reported by Google on 2026-05-17

[N/A][514059630] Medium CVE-2026-95346: UI misrepresentation in Chromoting. Reported by Google on 2026-05-17

[N/A][514072284] Medium CVE-2026-95320: Missing authorization in Navigation. Reported by Google on 2026-05-17

[N/A][514487499] Medium CVE-2026-95317: Incorrect authorization in MediaCapture. Reported by Google on 2026-05-19

[N/A][516404074] Medium CVE-2026-95345: Use after free in Actor. Reported by Google on 2026-05-25

[N/A][517163294] Medium CVE-2026-95330: Improper state validation in Downloads. Reported by Google on 2026-05-27

[N/A][517417437] Medium CVE-2026-95370: Inappropriate implementation in NFC. Reported by Google on 2026-05-28

[N/A][517442714] Medium CVE-2026-95303: Incomplete cleanup in SmartCard. Reported by Google on 2026-05-28

[N/A][517584808] Medium CVE-2026-95360: Race condition in Editing. Reported by Google on 2026-05-28

[N/A][517596255] Medium CVE-2026-95295: Information leak in Mobile. Reported by Google on 2026-05-28

[N/A][517730821] Medium CVE-2026-95276: Improper input validation in Themes. Reported by Google on 2026-05-29

[N/A][517802696] Medium CVE-2026-95314: Incorrect authorization in HID. Reported by Google on 2026-05-29

[N/A][520504291] Medium CVE-2026-95371: Missing authorization in Views. Reported by Google on 2026-06-05

[N/A][522061704] Medium CVE-2026-95353: Use after free in Bindings. Reported by Google on 2026-06-10

[N/A][522344883] Medium CVE-2026-95363: UI misrepresentation in FileSystem. Reported by Google on 2026-06-10

[N/A][523719002] Medium CVE-2026-95341: Improper input validation in Desktop. Reported by Google on 2026-06-14

[N/A][524582798] Medium CVE-2026-95354: Use after free in Verifier. Reported by Google on 2026-06-16

[N/A][526550688] Medium CVE-2026-95384: Race condition in Transactions Platform. Reported by Google on 2026-06-22

[N/A][532962621] Medium CVE-2026-95336: Information leak in Transactions Platform. Reported by Google on 2026-07-09

[N/A][536161355] Medium CVE-2026-95290: Missing authorization in NFC. Reported by Google on 2026-07-18

[N/A][536648933] Medium CVE-2026-95325: Use after free in ANGLE. Reported by Google on 2026-07-19

[TBD][542926849] Medium CVE-2026-95275: Incorrect reference resolution in MediaStream. Reported by Zabith Mohammed (@nmzabith) on 2026-08-05

[TBD][543464436] Medium CVE-2026-95374: Incorrect authorization in Network. Reported by NH DEV on 2026-08-07

[N/A][545449081] Medium CVE-2026-95300: Missing authorization in DevTools. Reported by Google on 2026-08-12

[TBD][545879261] Medium CVE-2026-95321: UI misrepresentation in Payments. Reported by jodyritonga on 2026-08-13

[TBD][546438368] Medium CVE-2026-95323: UI misrepresentation in Chromium. Reported by Wihdatu Nuuro Ahmadi on 2026-08-14

[N/A][546639650] Medium CVE-2026-95332: Use of uninitialized variable in Tint. Reported by Google on 2026-08-14

[N/A][547832510] Medium CVE-2026-95312: Information leak in Passwords. Reported by Google on 2026-08-17

[TBD][548611433] Medium CVE-2026-95344: Race condition in DevTools. Reported by @bean5oup on 2026-08-18

[TBD][549911100] Medium CVE-2026-95289: Incorrect authorization in Scroll. Reported by Vu Van Tien (@n0_Be3r) on 2026-08-21

[TBD][550181232] Medium CVE-2026-95347: Use after free in Updater. Reported by a45hif on 2026-08-21

[N/A][553123003] Medium CVE-2026-95311: Free of non-heap memory in Fonts. Reported by Google on 2026-08-26

[N/A][553141660] Medium CVE-2026-95358: Incorrect authorization in Mobile. Reported by Google on 2026-08-26

[TBD][559682346] Medium CVE-2026-95333: Use after free in Metrics. Reported by sean geofrey on 2026-09-10

[$500][423956129] Low CVE-2026-95307: UI misrepresentation in ExtensionsMenu. Reported by Hafiizh on 2025-06-11

[N/A][497094708] Low CVE-2026-95285: Missing authorization in WebView. Reported by Google on 2026-03-28

[N/A][497344014] Low CVE-2026-95278: Missing authorization in WakeLock. Reported by Google on 2026-03-29

[N/A][502077689] Low CVE-2026-95327: Information leak in Networking. Reported by Google on 2026-04-13

[N/A][513403696] Low CVE-2026-95334: Incorrect reference resolution in WebProtect. Reported by Google on 2026-05-15

[N/A][513714849] Low CVE-2026-95308: Integer overflow in Metrics. Reported by Google on 2026-05-16

[N/A][513781838] Low CVE-2026-95292: Incorrect authorization in Safebrowsing. Reported by Google on 2026-05-16

[N/A][513791872] Low CVE-2026-95352: Incorrect authorization in DevTools. Reported by Google on 2026-05-16

[N/A][514012689] Low CVE-2026-95279: UI misrepresentation in Omnibox. Reported by Google on 2026-05-17

[N/A][514524620] Low CVE-2026-95367: Information leak in DataTransfer. Reported by Google on 2026-05-19

[N/A][517192965] Low CVE-2026-95385: Inappropriate implementation in PlatformIntegration. Reported by Google on 2026-05-27

[N/A][522413520] Low CVE-2026-95368: Incorrect authorization in DevTools. Reported by Google on 2026-06-10

[N/A][523765972] Low CVE-2026-95319: Use after free in Printing. Reported by Google on 2026-06-14

[N/A][533041383] Low CVE-2026-95326: Incomplete cleanup in Bluetooth. Reported by Google on 2026-07-09

[N/A][533074595] Low CVE-2026-95309: UI misrepresentation in Mobile. Reported by Google on 2026-07-09

[N/A][533095855] Low CVE-2026-95361: Confused deputy in DevTools. Reported by Google on 2026-07-09

[N/A][533102653] Low CVE-2026-95288: UI misrepresentation in Mobile. Reported by Google on 2026-07-09

[N/A][534579660] Low CVE-2026-95380: Type confusion in V8. Reported by Google on 2026-07-14

[TBD][547027738] Low CVE-2026-95342: Missing authorization in V8. Reported by Hongwei Li, Zhun Wang, Ziyue Pan, Junmin Zhu, Saastha Vasan, and Wenbo Guo on 2026-08-16

[TBD][551296612] Low CVE-2026-95296: Missing authorization in Core. Reported by Quyền SƑn (@zer0qs1337) on 2026-08-23

[N/A][552023752] Low CVE-2026-95316: Unchecked return value in Performance. Reported by Google on 2026-08-24

[N/A][553148673] Low CVE-2026-95328: Confused deputy in Mobile. Reported by Google on 2026-08-26

[N/A][553268567] Low CVE-2026-95340: Incorrect authorization in PictureInPicture. Reported by Google on 2026-08-27

[N/A][553271219] Low CVE-2026-95364: Improper input validation in Passwords. Reported by Google on 2026-08-27

[N/A][553921181] Low CVE-2026-95305: UI misrepresentation in Chromoting. Reported by Google on 2026-08-28

We would also like to thank all security researchers that worked with us during the development cycle to prevent security bugs from ever reaching the stable channel.

Many of our security bugs are detected using AddressSanitizer, MemorySanitizer, UndefinedBehaviorSanitizer, Control Flow Integrity, libFuzzer, or AFL.

Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.


Srinivas Sista

Google Chrome

Share on TwitterΒ 
  •  

Firefox 156.0.1

Fixed

  • Fixed the NVDA screen reader not announcing address bar buttons when the mouse pointer moves over them. (Bug 2069276)

  • Fixed elements inside a link not showing their CSS :active styles while being clicked. (Bug 2067272)

  • Fixed Firefox becoming unresponsive on some pages that use CSS anchor positioning. (Bug 2070171)

  • Fixed Firefox windows on macOS 27 immediately returning to maximized after being restored by double-clicking the title bar. (Bug 2066632)

  • Fixed Firefox leaking system handles on Windows as content processes were started and stopped. (Bug 2069644)

Changed

  • Pressing Tab now moves focus straight to the text field of the address bar and search bar instead of stopping on the search engine button first. The button can still be reached with Shift+Tab.

  •  

Development build

Below are development builds with the latest fixes and improvements. Please test them thoroughly and report problems immediately, so that any regressions can be fixed in time for next stable release.

Latest development build: 2.8.2.56 (October 7th 2026)

Latest stable release build: 2.8.2
https://github.com/clsid2/mpc-hc/releases/tag/2.8.2

  •  

v0.20.0-rc.5

❗ This is a pre-release

  • May contain bugs and unfinished features.

⚠️ Note for macOS users

Builds are unsigned (no Apple Developer ID). After dragging MarkText into Applications, clear the quarantine flag once:

xattr -cr /Applications/marktext.app

Verifying downloads

All artifacts are listed with their SHA-256 in SHA256SUMS.txt. Verify with:

sha256sum -c SHA256SUMS.txt --ignore-missing

What's Changed

  • fix(desktop): load the e2e Playwright config by moving it to the package root by @Fr4ncis in #5435
  • fix(muya): ignore a table tool click once its table left the document (#5442) by @Jocs in #5443
  • docs: add StarDesk as a special sponsor by @Jocs in #5444
  • fix(tests): Windows paths + CI + timeout fix by @dzid26 in #5323
  • ci: check every text file out as LF so the Windows test leg sees the same bytes by @Jocs in #5447
  • ci: bound the unit-test job at ten minutes by @Jocs in #5448
  • fix(desktop): keep title bar path segments in order under the Bidi algorithm by @dronov-dmitry in #5317
  • fix(muya): apply pandoc's tex_math_dollars constraints to $…$ (#5446) by @Jocs in #5449
  • feat: add the texMathDollars preference, replacing the math option (#5446) by @Jocs in #5450
  • feat: implement pandoc's tex_math_gfm, replacing the GitLab compatibility option (#5446) by @Jocs in #5457
  • feat: show selected text word count by @Renakoni in #4457

New Contributors

Full Changelog: v0.20.0-rc.4...v0.20.0-rc.5

  •  

Stable Channel Update for Desktop

Β The Stable channel has been updated to 153.0.8010.52/.53 for Windows and Mac andΒ 153.0.8010.52 toΒ Linux which will roll out over the coming days/weeks. A full list of changes in this build is available in the LogΒ 

Security Fixes and Rewards

Note: Access to bug details and links may be kept restricted until a majority of users are updated with a fix. We will also retain restrictions if the bug exists in a third party library that other projects similarly depend on, but haven’t yet fixed.
This update includes 16 security fixes. Please see the Chrome Security Page for more information.

[TBD][500417361] Critical CVE-2026-93374: Use after free in Dawn. Reported by Florian Schweitzer on 2026-04-08 [N/A][548085797] Critical CVE-2026-93372: Buffer overflow in WebGL. Reported by Google on 2026-08-17 [$3,000][550839154] High CVE-2026-93375: Incorrect reference resolution in Tracing. Reported by M. Fauzan Wijaya (Gh05t666nero) on 2026-08-22 [TBD][541707261] High CVE-2026-93382: Use after free in PDFium. Reported by WinD39 - Huynh Dinh Vu on 2026-08-02 [N/A][553130676] High CVE-2026-93387: Improper state validation in Skia. Reported by Google on 2026-08-26 [N/A][553132214] High CVE-2026-93373: Use after free in Extensions. Reported by Google on 2026-08-26 [TBD][556853443] High CVE-2026-93381: Buffer overflow in PDFium. Reported by SeungMyung Lee (@sm1ee), Siung kim (@ksw9722) on 2026-09-03 [TBD][560039872] High CVE-2026-93379: Incorrect authorization in ORB. Reported by OGINOME Tomohito on 2026-09-11 [N/A][560121552] High CVE-2026-93377: Type confusion in V8. Reported by Google on 2026-09-11 [N/A][498411599] Medium CVE-2026-93380: Race condition in FileSystem. Reported by Google on 2026-04-01 [N/A][511832293] Medium CVE-2026-93384: Server-side request forgery in Omnibox. Reported by Google on 2026-05-10 [N/A][515493668] Medium CVE-2026-93383: Information leak in Permissions. Reported by Google on 2026-05-22 [N/A][520521197] Medium CVE-2026-93376: Out of bounds read in DataTransfer. Reported by Google on 2026-06-05 [N/A][540051167] Medium CVE-2026-93378: Missing authorization in Storage. Reported by Google on 2026-07-28 [N/A][553136980] Medium CVE-2026-93385: Information leak in Paint. Reported by Google on 2026-08-26 [N/A][513996595] Low CVE-2026-93386: UI misrepresentation in WebAppInstalls. Reported by Google on 2026-05-17

We would also like to thank all security researchers that worked with us during the development cycle to prevent security bugs from ever reaching the stable channel.

Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.

Srinivas Sista

Google Chrome
  •  

Extended Stable Update for Desktop

Β The Extended Stable channel has been updated to 152.0.7977.134Β for Windows and Mac which will roll out over the coming days/weeks.

A full list of changes in this build is available in the log. Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.

Srinivas Sista
Google Chrome
  •  

2.8.2

Changes from 2.8.1 to 2.8.2:

Updates:

  • Updated LAV Filters to version 0.83-5-gd65a9
  • Updated MPC Video Renderer to version 0.10.8.2587

Changes/additions:

  • Added ReplayGain support. Options can be found in audio switcher.
  • Improvements for exclusive mode seekbar when using MPCVR.
  • Improvements for opening a selection of files from Explorer. Now supports DropTarget interface.
  • Playback rate can now be shown in statusbar for audio files.
  • Keyboard shortcuts can now be edited without a mouse. Press Space or Enter to start editing a selected command. Press Enter or Tab to apply a pressed key combination. Enter/Tab can only be set as hotkey when combined with Alt/Ctrl/Shift.
  • Improvements for ATSC/DVB channel scanning.

Fixes:

  • Lots of small fixes and improvements.

  •  

v0.20.0-rc.4

❗ This is a pre-release

  • May contain bugs and unfinished features.

⚠️ Note for macOS users

Builds are unsigned (no Apple Developer ID). After dragging MarkText into Applications, clear the quarantine flag once:

xattr -cr /Applications/marktext.app

Verifying downloads

All artifacts are listed with their SHA-256 in SHA256SUMS.txt. Verify with:

sha256sum -c SHA256SUMS.txt --ignore-missing

What's Changed

  • chore(desktop): disable the Report button in the error dialog by @Jocs in #5359
  • fix(muya): run paragraph commands on the whole table or code block (#4944) by @Jocs in #5358
  • fix(muya): don't drop blocks when a cut ends inside a code block (#4903, #5148) by @Jocs in #5357
  • feat: add source line number toggle by @masalha-alaa in #5111
  • fix(muya): change the heading level of the caret's paragraph, not its list (#5360) by @Jocs in #5361
  • fix(muya): keep a setext heading's level when promoting or demoting it (#5362) by @Jocs in #5363
  • fix(muya): keep every line when a multi-line block becomes a heading (#5366) by @Jocs in #5367
  • fix(muya): collapse only the nested code block when a cut starts in its language line (#5368) by @Jocs in #5370
  • fix(muya): keep the code block when a cut ends in its language line (#5371) by @Jocs in #5372
  • fix(muya): remove the selected rest of a list or quote when a cut starts in it (#5385) by @Jocs in #5397
  • feat(muya): support same-line display math by @Renakoni in #4935
  • fix(muya): start an image resize only from the resize bar's own handles (#5116) by @Jocs in #5382
  • fix(muya): don't crash or replace another block when picking a table size after undo (#5355) by @Jocs in #5384
  • fix(desktop): launch normally when NODE_ENV=development is set (#5053) by @Jocs in #5374
  • fix(desktop): open files from a second instance started with --user-data-dir (#3020) by @Jocs in #5375
  • fix(desktop): keep debug mode out of release builds (#5407) by @Jocs in #5410
  • fix(desktop): read locale files from the app's resources (#5408) by @Jocs in #5411
  • fix(muya): keep the document intact when a cut ends in a table (#5400, #5405, #5399, #5398) by @Jocs in #5406
  • fix(muya): cancel Backspace that turns a setext heading into a paragraph (#5035) by @Jocs in #5381
  • fix(muya): keep a dollar sign in a regex replace capture by @Dev-next-gen in #5404
  • fix(muya): regexp replace groups β€” per-match Replace All, unmatched groups, two-digit $nn by @Jocs in #5420
  • fix(muya): keep an inline raw HTML tag's id intact by @Dev-next-gen in #5416
  • fix(muya): re-read the block type after a Backspace on a syntax marker (#5388) by @Jocs in #5421
  • fix(muya): keep blocks after a paragraph merged into a table cell out of the row (#5386) by @Jocs in #5422
  • fix(muya): keep the rest of a blockquote quoted on forward-Delete merge (#5423) by @Jocs in #5424
  • fix(muya): escape braces in a plain-text find query by @Dev-next-gen in #5428
  • fix(desktop): open Quick Open when files are open without a folder by @Dev-next-gen in #5431
  • fix(muya): select the document when Select All's cached caret block was removed by undo (#5387) by @Jocs in #5425

New Contributors

Full Changelog: v0.20.0-rc.3...v0.20.0-rc.4

  •  

Early Stable Update for Desktop

The Stable channel has been updated to 154.0.8037.44/.45 for Windows. as part of our early stable release to a small percentage of users. A full list of changes in this build is available in the log.

You can find more details about early Stable releases here.

Interested in switching release channels? Β Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.


Srinivas Sista

Google Chrome

  •  

Stable Channel Update for Desktop

The Stable channel has been updated to 153.0.8010.47/.48 for Windows and Mac andΒ 153.0.8010.47Β for Linux, which will roll out over the coming days/weeks. A full list of changes in this build is available in the LogΒ 

Security Fixes and Rewards

Note: Access to bug details and links may be kept restricted until a majority of users are updated with a fix. We will also retain restrictions if the bug exists in a third party library that other projects similarly depend on, but haven’t yet fixed.

This update includes 42 security fixes. Please see the Chrome Security Page for more information.

[N/A][556870863] Critical CVE-2026-91726: Out of bounds read in WebGL. Reported by Google on 2026-09-03 [TBD][557320614] Critical CVE-2026-91721: Use after free in Internals. Reported by xinyang on 2026-09-04 [TBD][558456602] Critical CVE-2026-91749: Use after free in Workers. Reported by WinD39 - Huynh Dinh Vu on 2026-09-08 [$1,500][552283275] High CVE-2026-91724: Use after free in Input. Reported by Hafiizh on 2026-08-25 [$1,000][556715288] High CVE-2026-91728: Integer overflow in V8. Reported by Jihyeon Jeong (Compsec Lab, Seoul National University / Research Intern) on 2026-09-03 [N/A][516780835] High CVE-2026-91734: Incorrect authorization in Core. Reported by Google on 2026-05-26 [N/A][516893912] High CVE-2026-91727: Incorrect reference resolution in Extensions. Reported by Google on 2026-05-26 [N/A][516947138] High CVE-2026-91743: Race condition in Core. Reported by Google on 2026-05-27 [N/A][520019273] High CVE-2026-91744: Race condition in PlatformIntegration. Reported by Google on 2026-06-04 [N/A][521486621] High CVE-2026-91712: Race condition in Extensions. Reported by Google on 2026-06-08 [N/A][521559611] High CVE-2026-91748: Race condition in Extensions. Reported by Google on 2026-06-09 [N/A][523470135] High CVE-2026-91720: Uninitialized resource in ANGLE. Reported by Google on 2026-06-13 [N/A][523554372] High CVE-2026-91731: Type confusion in Compositing. Reported by Google on 2026-06-13 [N/A][540016074] High CVE-2026-91747: Use after free in Skia. Reported by Google on 2026-07-28 [N/A][540021213] High CVE-2026-91733: Improper state validation in Skia. Reported by Google on 2026-07-28 [TBD][546413288] High CVE-2026-91741: Type confusion in CacheStorage. Reported by Salvatore Gulizia (nickname: Serotav) on 2026-08-14 [TBD][547815507] High CVE-2026-91709: Type confusion in ServiceWorker. Reported by Jihyeon Jeong (Compsec Lab, Seoul National University / Research Intern) on 2026-08-17 [TBD][549225472] High CVE-2026-91717: Missing authorization in Android. Reported by jodyritonga on 2026-08-20 [N/A][552416113] High CVE-2026-91735: Incorrect authorization in WebUI. Reported by Google on 2026-08-25 [N/A][553115724] High CVE-2026-91708: Race condition in Network. Reported by Google on 2026-08-26 [N/A][553121008] High CVE-2026-91736: Use after free in DOM. Reported by Google on 2026-08-26 [N/A][553122373] High CVE-2026-91740: Uninitialized resource in Skia. Reported by Google on 2026-08-26 [N/A][553132148] High CVE-2026-91710: Use after free in WebAppInstalls. Reported by Google on 2026-08-26 [N/A][553133215] High CVE-2026-91718: Use after free in Core. Reported by Google on 2026-08-26 [N/A][554558368] High CVE-2026-91716: Use after free in Auth. Reported by Google on 2026-08-29 [N/A][556260782] High CVE-2026-91746: Integer overflow in Compositing. Reported by Google on 2026-09-02 [TBD][557206809] High CVE-2026-91729: Use after free in DigitalCredentials. Reported by sean geofrey on 2026-09-04 [TBD][558036280] High CVE-2026-91737: Use after free in PDF. Reported by SeungMyung Lee (@sm1ee), Siung kim (@ksw9722) on 2026-09-06 [TBD][558342353] High CVE-2026-91711: Out of bounds write in ServiceWorker. Reported by Cristian Di Nicola (@crih.exe) on 2026-09-07 [TBD][558367547] High CVE-2026-91715: Type confusion in ServiceWorker. Reported by Cristian Di Nicola (@crih.exe) on 2026-09-07 [N/A][558734727] High CVE-2026-91745: Use after free in V8. Reported by Google on 2026-09-08 [TBD][474131239] Medium CVE-2026-91723: Race condition in WebAppInstalls. Reported by Luan Herrera (@lbherrera_) on 2026-01-07 [TBD][511062248] Medium CVE-2026-91732: Missing authorization in AppManifest. Reported by pakhunov.anton.n on 2026-05-08 [N/A][513858387] Medium CVE-2026-91742: Confused deputy in PriceTracking. Reported by Google on 2026-05-16 [N/A][517710554] Medium CVE-2026-91714: Observable discrepancy in Fonts. Reported by Google on 2026-05-29 [N/A][518032534] Medium CVE-2026-91725: Observable discrepancy in CSS. Reported by Google on 2026-05-29 [N/A][521951328] Medium CVE-2026-91739: Missing authorization in Transactions Platform. Reported by Google on 2026-06-09 [N/A][523715133] Medium CVE-2026-91713: Missing authorization in Browser. Reported by Google on 2026-06-14 [N/A][536450979] Medium CVE-2026-91738: Improper input validation in ANGLE. Reported by Google on 2026-07-19 [TBD][543640868] Medium CVE-2026-91730: Incomplete cleanup in GetUserMedia. Reported by Keita Sode and Daisuke Hatakeyama (SYZD Research) on 2026-08-07 [TBD][554953456] Medium CVE-2026-91722: Use after free in Input. Reported by TIENPA on 2026-08-31 [TBD][542115030] Low CVE-2026-91719: Code injection in XML. Reported by Zabith Mohammed (@nmzabith) on 2026-08-03

We would also like to thank all security researchers that worked with us during the development cycle to prevent security bugs from ever reaching the stable channel.

Many of our security bugs are detected using AddressSanitizer, MemorySanitizer, UndefinedBehaviorSanitizer, Control Flow Integrity, libFuzzer, or AFL.

Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.


Srinivas Sista

Google Chrome
  •  

Extended Stable Update for Desktop

Β The Extended Stable channel has been updated to 152.0.7977.130 for Windows and Mac which will roll out over the coming days/weeks.

A full list of changes in this build is available in the log. Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.

Srinivas Sista
Google Chrome
  •  

Firefox 156.0

New

  • Firefox on macOS can now be set to open automatically when the computer starts up, from the Startup section of Settings.

  • Localized Wikipedia and occasional sponsored suggestions in the address bar are now available in France, Germany, and Italy. These suggestions can be turned off in Firefox Suggest settings.

Fixed

  • Fixed an issue where dragging an image to a new position in a rich-text editor could replace it with a long line of text instead of moving it.

  • Fixed high-sample-rate FLAC audio in MP4 failing to play on sites such as Bilibili.

  • Fixed subtitles not appearing in the Picture-in-Picture window when they are turned on in the video player after the window has already opened.

  • Fixed bookmarks moving out of their folder when the folder and the bookmarks inside it were selected and dragged together in the Bookmarks sidebar.

  • Fixed the find bar becoming permanently unavailable in a tab after reversing the panes in Split View.

  • Fixed some sites failing to load when DNS over HTTPS is enabled and the site does not support HTTPS.

  • Fixed Firefox losing all network connectivity for some users with the built-in VPN enabled.

  • Fixed an issue on Windows where Firefox could block an auto-hiding taskbar from showing.

  • Various security fixes.

Changed

  • Firefox's built-in PDF viewer now starts up to 45% faster.

  • Improved memory and CPU usage when Firefox displays large JPEG images scaled down to fit a page.

  • On Windows devices with ARM64 processors, WebRTC video calls may now use hardware H264 decoding instead of falling back to software.

Enterprise

Developer

Web Platform

  • text-box-trim now uses the font metrics of a ::first-line pseudo-element when one applies, matching other browsers and the specification.

Community Contributions

  •  

v0.20.0-rc.3

❗ This is a pre-release

  • May contain bugs and unfinished features.

⚠️ Note for macOS users

Builds are unsigned (no Apple Developer ID). After dragging MarkText into Applications, clear the quarantine flag once:

xattr -cr /Applications/marktext.app

Verifying downloads

All artifacts are listed with their SHA-256 in SHA256SUMS.txt. Verify with:

sha256sum -c SHA256SUMS.txt --ignore-missing

What's Changed

  • fix(muya): make a code block a diagram when its language is a diagram language (#5060) by @Jocs in #5304
  • docs: fix the macOS alias path in the CLI docs by @Jocs in #5308
  • chore: run only eslint --fix on staged desktop TS/Vue files by @Jocs in #5318
  • fix(desktop): ignore line-ending menu updates for a closed window (#4923) by @Jocs in #5319
  • fix: #4926 prevent emoji deletion from splitting surrogate pairs by @Renakoni in #4931
  • fix(desktop): keep exported links working from folders named with #, ? or % by @Dev-next-gen in #5320
  • fix(desktop): explain the max width format in preferences (#5331) by @Jocs in #5334
  • fix(muya): delete emoji whole in code blocks and drop the caret-inside-cluster handler (#4926) by @Jocs in #5332
  • fix(desktop): keep exported images working from folders named with #, ? or % (#5335) by @Jocs in #5337
  • fix(muya): regex search freezes on zero-width patterns and splits emoji by @Jocs in #5333
  • fix(desktop): keep the share host in exported links from UNC documents (#5336) by @Jocs in #5338
  • fix: #4899 keep trailing content out of the child list when outdenting a list item by @doktorigi in #4913
  • fix(muya): keep the link popover open when moving between links (#5313) by @anandghegde in #5324
  • fix: reuse image on case-insensitive path match (#3119) by @dzid26 in #5326
  • fix(desktop): name copied images after their content, not their path (#5344) by @Jocs in #5346
  • fix(muya): only outdent a paragraph that sits in a nested list item (#5342) by @Jocs in #5345
  • fix(muya): split the list when outdenting a task item into a plain list (#5341) by @Jocs in #5348
  • fix(muya): edit a footnote definition as its own container (#5340, #5343) by @Jocs in #5347
  • fix(muya): keep a Tab-indented list item out of a sublist of the other kind (#5349) by @Jocs in #5354
  • fix(muya): preserve ordered list source markers by @Renakoni in #4776

New Contributors

Full Changelog: v0.20.0-rc.2...v0.20.0-rc.3

  •  

HWMonitor 1.68

  • PCI Express errors counters on AMD and Intel GPUs.
  • New metrics on AMD Strix Point, Strix Halo and Kraken Point : NPU power, NPU clocks, NPU TOPS and TOPS per watt, NPU DRAM bandwidth usage, global platform power and DRAM read and write bandwidths.
  • New HDD metrics (IOPS, average latency, NVMe controller link speed).
  • Remembers devices & sensor types nodes state.
  •  

v0.20.0-rc.2

❗ This is a pre-release

  • May contain bugs and unfinished features.

⚠️ Note for macOS users

Builds are unsigned (no Apple Developer ID). After dragging MarkText into Applications, clear the quarantine flag once:

xattr -cr /Applications/marktext.app

Verifying downloads

All artifacts are listed with their SHA-256 in SHA256SUMS.txt. Verify with:

sha256sum -c SHA256SUMS.txt --ignore-missing

What's Changed

  • fix: preserve Google Docs CSS formatting on paste by @Renakoni in #4699
  • fix(desktop): preserve RTL text direction in PDF and print export by @Jocs in #4874
  • docs: update sponsor logo by @Jocs in #5014
  • docs: remove sponsor ukey by @Jocs in #5217
  • fix: preserve viewport when toggling task-list checkbox by @Awaker-OTE in #5189
  • fix(desktop): allow saving directly to a drive root (#5150) by @Panisnbb in #5188
  • docs: fix grammar issues in FAQ.md by @woltary02-creator in #5089
  • fix(ui): sync quick insert highlight with input method by @KDOJP in #5176
  • feat(i18n): add Dutch locale + validation tests + fix existing issues by @rkristelijn in #5137
  • Japanese translation update by @coolvitto in #5049
  • fix: allow copy-paste in same folder with auto-rename by @rkristelijn in #5139
  • chore: add pre-commit hooks (husky + lint-staged) by @rkristelijn in #4999
  • fix(muya): escape HTML in image attribute values (CWE-79) by @andesyteoss in #4980
  • fix: #5001 persist pasted bitmap images to the assets folder per preferences by @Panisnbb in #5168
  • fix(muya): preserve cursor on IME composition backspace(#4956) by @Zengzzhao in #4957
  • fix(muya): size table columns to their content by @Renakoni in #4952
  • fix: handle UNC image paths and watchers by @Renakoni in #4778
  • fix(desktop): ignore revoked output pipe errors on macOS by @Awaker-OTE in #5229
  • feat(desktop): add "Reset Zoom" item to the Window menu by @xrgzs in #5185
  • fix: #3469 decode Windows clipboard file paths as UTF-16LE by @Panisnbb in #5167
  • fix(desktop): prevent CodeMirror line tree corruption by @Renakoni in #4930
  • fix(i18n): add the missing Dutch resetZoom label by @githello1 in #5245
  • feat(macOS): add Dictionary lookup for selected editor text by @nikkogibler in #4814
  • fix: #4890 use file extension for side bar icons by @doktorigi in #4910
  • fix(muya): #4747 deep clone editor state without recursing by @CookPiu in #5259
  • fix: init image size when render html tag image by @Jocs in #5264
  • fix: render rect selection in table by @Jocs in #5265
  • fix: the missing locale key by @Jocs in #5266
  • fix: #5152 align TOC navigation with editor viewport by @foo-hao in #5153
  • fix: #5130 keep Electron locale resources for all supported UI languages by @legsing in #5132
  • fix: #5129 detect system language on first start by @legsing in #5131
  • fix: skip website preview deploy on fork PRs by @Jocs in #5278
  • feat: add 'Treat soft newlines as spaces' preference (#1849) by @wmoss in #4937
  • fix(muya): keep IME input intact after a soft line break by @Jocs in #5281
  • fix(muya): stop the quick-insert hint claiming a line of its own by @Jocs in #5283
  • fix(muya): give a code block's trailing empty line a line box by @Jocs in #5286
  • fix(muya): keep footnote reference ids intact for special identifiers (#5208) by @Jocs in #5285
  • fix(muya): skip search matches whose block left the document (#5163, #5215) by @Jocs in #5287
  • fix(muya): keep the image resize bar from crashing after its image is removed (#5216) by @Jocs in #5288
  • fix(muya): ignore a quick-insert pick once its paragraph is gone (#5213) by @Jocs in #5289
  • fix(muya): drop an image selection whose block left the document (#5055) by @Jocs in #5291
  • fix(muya): number empty lines in code blocks (#5294) by @Jocs in #5295
  • fix(muya): don't restore a drag selection onto removed blocks (#4981, #5256) by @Jocs in #5290
  • fix(muya): end the paragraph on a Shift+Enter that would leave an empty line by @Jocs in #5300
  • fix: make anchor links reach CJK headings and headings in other documents (#5292) by @Jocs in #5298
  • fix(desktop): flush pending edits before entering source code mode by @richbodo in #5103
  • fix(muya): load relative images from folders named with #, ? or % (#5302) by @Jocs in #5301
  • test(desktop): wait for TOC scrolls to settle in the toc-scroll e2e by @Jocs in #5303

New Contributors

Full Changelog: v0.20.0-rc.1...v0.20.0-rc.2

  •  

Early Stable Update for Desktop

Β The Stable channel has been updated to 154.0.8037.17/.18 for Windows. Mac is coming shortly , as part of our early stable release to a small percentage of users. A full list of changes in this build is available in the log.

You can find more details about early Stable releases here.

Interested in switching release channels? Β Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.


Srinivas Sista

Google Chrome

  •  

Extended Stable Update for Desktop

Β The Extended Stable channel has been updated to 152.0.7977.120Β for Windows and Mac which will roll out over the coming days/weeks.

A full list of changes in this build is available in the log. Interested in switching release channels? Find out how here. If you find a new issue, please let us know by filing a bug. The community help forum is also a great place to reach out for help or learn about common issues.

Srinivas Sista
Google Chrome
  •  
❌