❌

Normale weergave

Bitfocus Companion v5.0.7

1 Oktober 2026 om 21:28

πŸ“¦ Downloads available at

πŸ’΅ Donate to the project at

Companion v5.0.7 - Release Notes

🐞 BUG FIXES

  • only add imageBuffers layer to simple presets when a feedback declares imageBuffer #4490
  • limit preset advanced-feedback style overrides to affectedProperties #4410 #4490
  • some surface open race conditions
  • update elgato-stream-deck surface module
  • layered presets lose all feedbacks when style overrides use plain values (#4477)
  • late closeSurface closing a reopened plugin surface
  • abort signal not being propagated into module action callback
  • move expression stream re-evaluation log to silly level #4489

Full Changelog: v5.0.6...v5.0.7

  •  

hMailServer 5.7.1, build 3116

29 September 2026 om 08:55

Security:

  • Fixed script injection in event scripts. With JScript, untrusted values passed to event handlers (such as the logon password in OnClientValidatePassword, or error text and UIDs sent by remote servers) could break out of their string. With either script language, a rule's "Run function" name could carry code. This would allow an attacker to run arbitrary code in the hMailServer process. Values are now escaped, and rule function names may only contain letters, digits and underscores.

If you are unable to install this version, disable JScript execution and do not give end-users access to the hMailServer COM API.

  •  

Legacy releases

28 September 2026 om 20:32

Archived hMailServer builds, from 4.1.1 to 5.6.9 build 2607. These versions are no longer supported and are kept for reference only. Use the latest release for new installations.

  •  

v0.16.24

27 September 2026 om 20:28

[0.16.24] - 2026-09-27

If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.

Added

  • DNS: PowerDNS Authoritative provider for automatic DNS record management.

Changed

Fixed

  • Troubleshoot tool: TLSA records are looked up for every MX host, including hosts whose zone is not DNSSEC signed.
  • Spam filter:
    • OpenPhish and PhishTank entries containing uppercase characters never match, since message URLs are lowercased while HTTP lookup entries keep their original case. HTTP lookups now match keys case-insensitively.
    • URL shortener links are followed using the lowercased URL, so case-sensitive short links resolve to the wrong destination or not at all.
    • Incremental training never advances its position past the first run, so every retained sample added since then is trained again, and counted again in the reservoir, on each run until it expires.
    • Updating the rules only adds new objects, so upstream changes to existing rules, DNSBL servers, HTTP lookups, lookup keys and file extensions never reach an existing installation.
    • Updating the rules reports success when objects fail to import, or when a configuration error stops the updated settings from being activated.
  • JMAP:
    • A PushSubscription created within the verification rate limit window of another one on the same account never receives its PushVerification, since the blocked verification is dropped instead of being sent once the window expires.
    • A push notification retried after a failed delivery can report an older state than a change queued during the failed attempt, since the older state changes are merged last and overwrite the newer ones.
    • Changes made while a push request is in flight are not delivered until the next change reaches the same subscription, since a successful delivery cancels the pending retry.
    • The VAPID aud claim is derived from a hand-written parse of the push URL, so a crafted push URL can make the server sign a token for a push service other than the one the request is sent to.
    • Email/import rejects a blobId that refers to a Blob/upload creation id in the same request ("#u0") with Invalid blob id..
    • Email/set with a full mailboxIds object identical to the current mailboxes, together with a keyword change, stores the message with IMAP UID 0, so IMAP clients stop seeing it.
  • MTA:
    • A node without the outboundMta role stops replying to DATA and to JMAP submissions once about 1024 messages have been queued on it.
    • MX records are resolved through the DNSSEC-validating resolver even when DANE is disabled.
    • A DATA stage Sieve script does not see headers added by milters or MTA hooks, and discards every milter and MTA hook change when it edits the message.
  • MySQL: Range deletions and search index removals start with a single unbounded DELETE and switch to chunks only after a timeout.
  • IMAP: COPY and MOVE fail with NO [CONTACTADMIN] when another session changes the same message at the same time.
  • Autodiscover: Implicit TLS ports (993, 995, 465) are advertised with <Encryption>TLS</Encryption>, which Outlook reads as STARTTLS.
  • HTTP: Idle keep-alive connections are never closed.

Check binary attestation here

  •  

PostgreSQL 19 Beta 4 Released!

24 September 2026 om 02:00

The PostgreSQL Global Development Group announces that the fourth beta release of PostgreSQL 19 is now available for download. This release contains PostgreSQL 19 feature previews ahead of general availability, though some details of the release can change during the beta period.

You can find information about all of the PostgreSQL 19 features and changes in the release notes:

https://www.postgresql.org/docs/19/release-19.html

The next planned release of PostgreSQL 19 is the release candidate, which should occur in early October. Based on testing and evaluation, this means that the PostgreSQL 19 GA may also occur in October. More details will be provided as we move closer to these releases.

This beta release reverted several features that were originally planned for PostgreSQL 19. The PostgreSQL community strongly believes that, first and foremost, PostgreSQL must be reliable. Additionally, the community strives for a predictable release schedule. Because of this, the community chose to remove some features from the PostgreSQL 19 release so they can be potentially be included in a later major release after more time working through the community development and review process.

Your testing and feedback help the community ensure that PostgreSQL 19 upholds our standards of delivering a stable, reliable release of the world's most advanced open source relational database. Please read more about our beta testing process and how you can contribute:

https://www.postgresql.org/developer/beta/

Upgrading to PostgreSQL 19 Beta 4

To upgrade to PostgreSQL 19 Beta 4 from an earlier version of PostgreSQL, you will need to use a strategy similar to upgrading between major versions of PostgreSQL (e.g. pg_upgrade or pg_dump / pg_restore). For more information, please visit the documentation section on upgrading.

Changes Since Beta 3

Fixes and changes in PostgreSQL 19 Beta 4 include:

  • Revert SQL/PGQ (property graph query) support.
  • Revert online enabling and disabling of data checksums.
  • Revert support for temporal updates/deletes provided by the FOR PORTION OF clause.
  • Revert ALTER TABLE ... MERGE PARTITIONS and ALTER TABLE ... SPLIT PARTITIONS.
  • Remove the pg_get_role_ddl(), pg_get_tablespace_ddl(), and pg_get_database_ddl() functions.
  • Revert a change that forced LC_COLLATE to C in the postmaster process.
  • Several fixes to the performance improvement feature for the foreign key constraint checks.
  • Several fixes for the new REPACK command, including crashes, incorrect behavior with invalid indexes and materialized views, and several permission and error-reporting corrections.
  • Several fixes for the new WAIT FOR command, including a deadlock and clearer reporting of isolation-level errors.
  • Fix validation of an empty FOREIGN_JOIN list in pg_plan_advice.
  • Several fixes for CREATE PUBLICATION ... EXCEPT.
  • Fix logical replication initial table synchronization when replicating from an older PostgreSQL version to v19.
  • Several fixes for logical replication conflict detection.
  • Several fixes for the new autovacuum scoring system, including for TOAST tables.
  • Fix for the COPY FROM SIMD optimization.
  • Fix a crash when accessing a partition whose concurrent detach did not complete.
  • Clarify that failed transactions are reported separately when using pgbench --continue-on-error.

Please see the release notes for a complete list of new and changed features:

https://www.postgresql.org/docs/19/release-19.html

Testing for Bugs & Compatibility

The stability of each PostgreSQL release greatly depends on you, the community, to test the upcoming version with your workloads and testing tools to find bugs and regressions before the general availability of PostgreSQL 19. As this is a Beta, minor changes to database behaviors, feature details, and APIs are still possible. Your feedback and testing will help determine the final tweaks on the new features, so please test in the near future. The quality of user testing helps determine when we can make a final release.

A list of open issues is publicly available in the PostgreSQL wiki. You can report bugs using this form on the PostgreSQL website:

https://www.postgresql.org/account/submitbug/

Beta Schedule

This is the fourth beta release of version 19. The PostgreSQL Project is planning to move to the release candidate portion of the release cycle, and will continue to issue release candidates until PostgreSQL 19 is made generally available. For further information please see the Beta Testing page.

Links

If you have corrections or suggestions for this release announcement, please send them to the pgsql-www@lists.postgresql.org public mailing list.

  •  

uNmINeD 0.20.10-dev

Door: megasys
21 September 2026 om 14:42

New uNmINeD development snapshot is available for download!

Changes:

  • Fixed Bedrock LevelDB parsing errors
  • (GUI) Fixed random black isometric tiles
  •  

v0.16.23

21 September 2026 om 11:57

[0.16.23] - 2026-09-21

If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.

Added

  • Expressions: bit_and function.

Changed

Fixed

  • MTA:
    • A mailing list whose recipients include another mailing list is accepted at RCPT TO and then rejected at local delivery with 550 5.5.0 Mailbox not found.
    • DMARC aggregate reports carry two spf elements per record and the version element of a DMARC aggregate report is written as 1 instead of 1.0.
    • DSNs generated for an alias rewrite or a list expansion emit a doubled addr-type in Original-Recipient (rfc822;rfc822;user@example.org).
    • DSNs that cannot be written to the store are discarded, the recipients are flagged as notified and the original message is removed from the queue, losing both the bounce and the message.
  • POP3:
    • TOP msg n counts the n lines from the first byte of the message instead of from the first byte of the body.
    • A message whose very first line begins with . is not byte-stuffed.
  • Spam filter: Moving or copying a message from one account into another creates no training sample, so the classifier never learns from it.
  • Sieve: envelope "orcpt" yields the bare address for an ORCPT supplied over SMTP. It now carries the addr-type prefix in every case, as required by RFC 6009.
  • ACME: The _acme-challenge TXT records published for a DNS-01 authorization are never removed.
  • DNS: The DNSSEC resolver queries a single nameserver at a time, working around a hickory-resolver race that cancels the TCP retry when two nameservers return a truncated response in parallel.
  • Troubleshoot tool:
    • MX records are resolved through the DNSSEC-validating resolver, matching the resolver used by the delivery path.
    • A TLSA lookup that fails or returns bogus records stops the delivery attempt for that host, instead of continuing without DANE.
  • OIDC: Bearer tokens that carry no email, preferred_username or upn claim are always authenticated against the default directory.
  • Meilisearch: A confirmation timeout is treated as a failed write even when failOnTimeout is disabled, so an index whose batches take longer than pollInterval x maxRetries never completes an indexing task and resubmits the same batch indefinitely.
  • WebUI: A failed update no longer takes an Application offline.
  • FoundationDB: The cached read version is invalidated when any broadcast is received from another node.
  • Redis:
    • On a cluster, the rate limiter and the blob upload quota issue INCR and EXPIRE as a MULTI/EXEC transaction, whose MOVED redirects collapse into a single EXECABORT that never refreshes the slot map.
    • A connection that fails because it is addressing the wrong server is returned to the pool and reused, since the recycle check only issues PING.

Check binary attestation here

  •  

v1.21.1

20 September 2026 om 18:18

Fixes and improvements

General

  • require browser POST requests to have an allowed origin (#6238) Browsers can send POST requests without performing any preflight request and without checking whether the request origin is present in Access-Control-Allow-Origin. Intercept these requests and check server-side whether the origin is allowed, blocking the request if it is not.
  • conf: fix comparison and sharing of the default authInternalUsers (#6205)
  • h265: fix DTS extraction of streams with long-term reference pictures (bluenviron/mediacommon#371)
  • pmp4: support stsz with a constant sample size (#5803) (bluenviron/mediacommon#373)
  • pmp4, fmp4: restore check on inbound H265 SPS (bluenviron/mediacommon#374) A valid H265 SPS is required for marshaling back an MP4, so we have to resume checking them.
  • pmp4: support tracks without edts (bluenviron/mediacommon#375) The edit box is optional (ISO/IEC 14496-12, 8.6.5), but tracks without it were rejected with "unexpected box 'mdia'".
  • pmp4: return seek errors from GetPayload (bluenviron/mediacommon#376) GetPayload checked the wrong variable after seeking, therefore a failed seek was ignored and the payload was read from the current position of the reader.
  • pmp4, fmp4: correctly fill HvcC NumTemporalLayers / TemporalIdNested from SPS (bluenviron/mediacommon#379)
  • pmp4: support tracks longer than 2^32 ticks (bluenviron/mediacommon#377)

RTSP

RTMP

HLS

  • make the server manage sessions (#6239) Sessions are now managed by the HLS server, detaching their lifecycle from muxers. This also comes with a performance improvement, since finding a session now traverses a single mutex, and not two channels like before.
  • return 404 when a session is valid but muxer is closed (#5736) (#6240) HLS sessions are now kept open for up to 30 seconds after a muxer is closed. This allows the server to handle incoming requests belonging to these sessions and to classify then as 404 rather than 401.
  • change error returned in case session is not found (#6241) match the RTSP behavior and return a "session not found" message rather than an "authentication error", which is reserved for creating sessions, not for using them.
  • muxer: return 404 when closed (bluenviron/gohlslib#394)

WebRTC

  • fix AV1 getting stuck by stripping padding (#5632) (#5774) (#6242) AV1 OBU padding is generated by several encoders. Stripping it has been demonstrated to solve most situations in which browsers get stuck when playing such streams.
  • fix stuck decoding with DJI drones (#5221) (#6051) (#6243) Streams from DJI drones contain SEI units with payload type 5 and a specific UUID that seem to cause stuck videos on Chrome and Firefox. Filter out these units.
  • add ability to exclude interfaces (#5788)

Dependencies

  • code.cloudfoundry.org/bytefmt updated from v0.88.0 to v0.90.0
  • github.com/MicahParks/keyfunc/v3 updated from v3.8.1 to v3.8.2
  • github.com/abema/go-mp4 updated from v1.7.1 to v1.7.3
  • github.com/bluenviron/gohlslib/v2 updated from v2.4.4 to v2.4.5
  • github.com/bluenviron/gortmplib updated from v1.0.2 to v1.0.3
  • github.com/bluenviron/gortsplib/v5 updated from v5.6.5 to v5.6.6
  • github.com/bluenviron/mediacommon/v2 updated from v2.9.4 to v2.9.5
  • github.com/gin-contrib/pprof updated from v1.5.4 to v1.5.5
  • github.com/matthewhartstonge/argon2 updated from v1.5.7 to v1.6.3
  • github.com/pion/ice/v4 updated from v4.4.1 to v4.4.2
  • github.com/pion/interceptor updated from v0.1.47 to v0.1.48
  • github.com/pion/sdp/v3 updated from v3.0.19 to v3.0.20
  • github.com/pion/transport/v4 updated from v4.1.0 to v4.1.1
  • github.com/pion/webrtc/v4 updated from v4.2.19 to v4.2.20
  • golang.org/x/crypto updated from v0.55.0 to v0.57.0
  • golang.org/x/net updated from v0.58.0 to v0.59.0
  • golang.org/x/sync updated from v0.22.0 to v0.23.0
  • golang.org/x/sys updated from v0.47.0 to v0.48.0
  • golang.org/x/term updated from v0.45.0 to v0.46.0
  • github.com/bytedance/gopkg updated from v0.1.3 to v0.1.4
  • github.com/bytedance/sonic updated from v1.15.0 to v1.15.2
  • github.com/bytedance/sonic/loader updated from v0.5.0 to v0.5.1
  • github.com/cloudwego/base64x updated from v0.1.6 to v0.1.7
  • github.com/gabriel-vasile/mimetype updated from v1.4.12 to v1.4.13
  • github.com/gin-contrib/sse updated from v1.1.0 to v1.1.1
  • github.com/go-playground/validator/v10 updated from v10.30.1 to v10.30.3
  • github.com/goccy/go-json updated from v0.10.5 to v0.10.6
  • github.com/klauspost/cpuid/v2 updated from v2.3.0 to v2.4.0
  • github.com/mattn/go-isatty updated from v0.0.20 to v0.0.23
  • github.com/pelletier/go-toml/v2 updated from v2.2.4 to v2.4.3
  • github.com/pion/dtls/v3 updated from v3.1.5 to v3.1.8
  • github.com/pion/mdns/v2 updated from v2.1.0 to v2.2.0
  • github.com/pion/srtp/v3 updated from v3.0.13 to v3.0.15
  • github.com/pion/stun/v3 removed
  • github.com/pion/turn/v5 updated from v5.0.13 to v5.1.0
  • go.mongodb.org/mongo-driver/v2 updated from v2.5.0 to v2.8.0
  • golang.org/x/arch updated from v0.22.0 to v0.29.0
  • golang.org/x/text updated from v0.41.0 to v0.42.0
  • google.golang.org/protobuf updated from v1.36.10 to v1.36.11
  • github.com/pion/stun/v4 v4.0.0 added
  • hls.js updated from v1.7.2 to v1.7.3

Security

Binaries are compiled from source code by the Release workflow, which is a fully-visible process that prevents any change or external interference in produced artifacts.

Checksums of binaries are also published in a public blockchain by using GitHub Attestations, and they can be verified by running:

ls mediamtx_* | xargs -L1 gh attestation verify --repo bluenviron/mediamtx

You can verify checksums of binaries by downloading checksums.sha256 and running:

cat checksums.sha256 | grep "$(ls mediamtx_*)" | sha256sum --check

  •  

Bitfocus Companion v5.0.6

Door: Julusian
18 September 2026 om 22:41

πŸ“¦ Downloads available at

πŸ’΅ Donate to the project at

Companion v5.0.6 - Release Notes

🐞 BUG FIXES

  • surface module compatibility check using wrong versions #4472
  • improve UX of internal: Local Variable: Set value name field, clarifying what is valid input #4467
  • unable to change version of surface module
  • better logging in internal actions when not finding local variable to update #4466
  • Page dropdown not scrolling to the current page #4456
  • respect explicit show_topbar when scaling legacy font sizes
  • suppress logging for rosstalk noop commands #4463
  • sanitise custom-variable option values
  • update canvas library to fix png containing svg issue #4438

Full Changelog: v5.0.5...v5.0.6

  •  

v4.3.23

18 September 2026 om 15:38

Features

  • Added a read-only API endpoint to retrieve preview deployment runtime logs by application UUID and pull request ID, with line limits and optional timestamps. (#11884)

Fixes

  • Fixed deployment status and metadata processing when remote command output contained leading or trailing whitespace.

What's Changed

Full Changelog: v4.3.22...v4.3.23

  •  

v4.3.22

18 September 2026 om 14:02

Breaking Changes

  • Removed host-path configuration for persistent volumes from the UI and API. API requests that include host_path are now rejected.

Features

  • Added a pull request settings modal with refresh and deployment controls for preview deployments.
  • Added real-time Sentinel synchronization status across server and application views.
  • Added separate options to delete local and S3 archives when a volume backup schedule was removed.

Fixes

  • Generated separate Traefik rules for comma-separated Docker Compose preview domains, which fixed broken preview routing (#11812, closed #7915).
  • Fell back to the system DNS resolver when configured resolvers returned no address records (#11811, closed #11810).
  • Preserved whitespace in streamed command output, which prevented Docker Compose argument injection from corrupting Dockerfiles (#11466, closed #11386).
  • Preserved pull request filters in deployment history and showed the active filter.
  • Redirected team switches to the dashboard to prevent invalid cross-team pages.

Improvements

  • Made scheduled tasks, database backups, volume backups, and Docker cleanups execute only once per occurrence across distributed schedulers.
  • Improved volume backup execution details and archive actions on mobile devices.
  • Simplified persistent storage controls and kept volume actions on one line.

What's Changed

Full Changelog: v4.3.21...v4.3.22

  •  

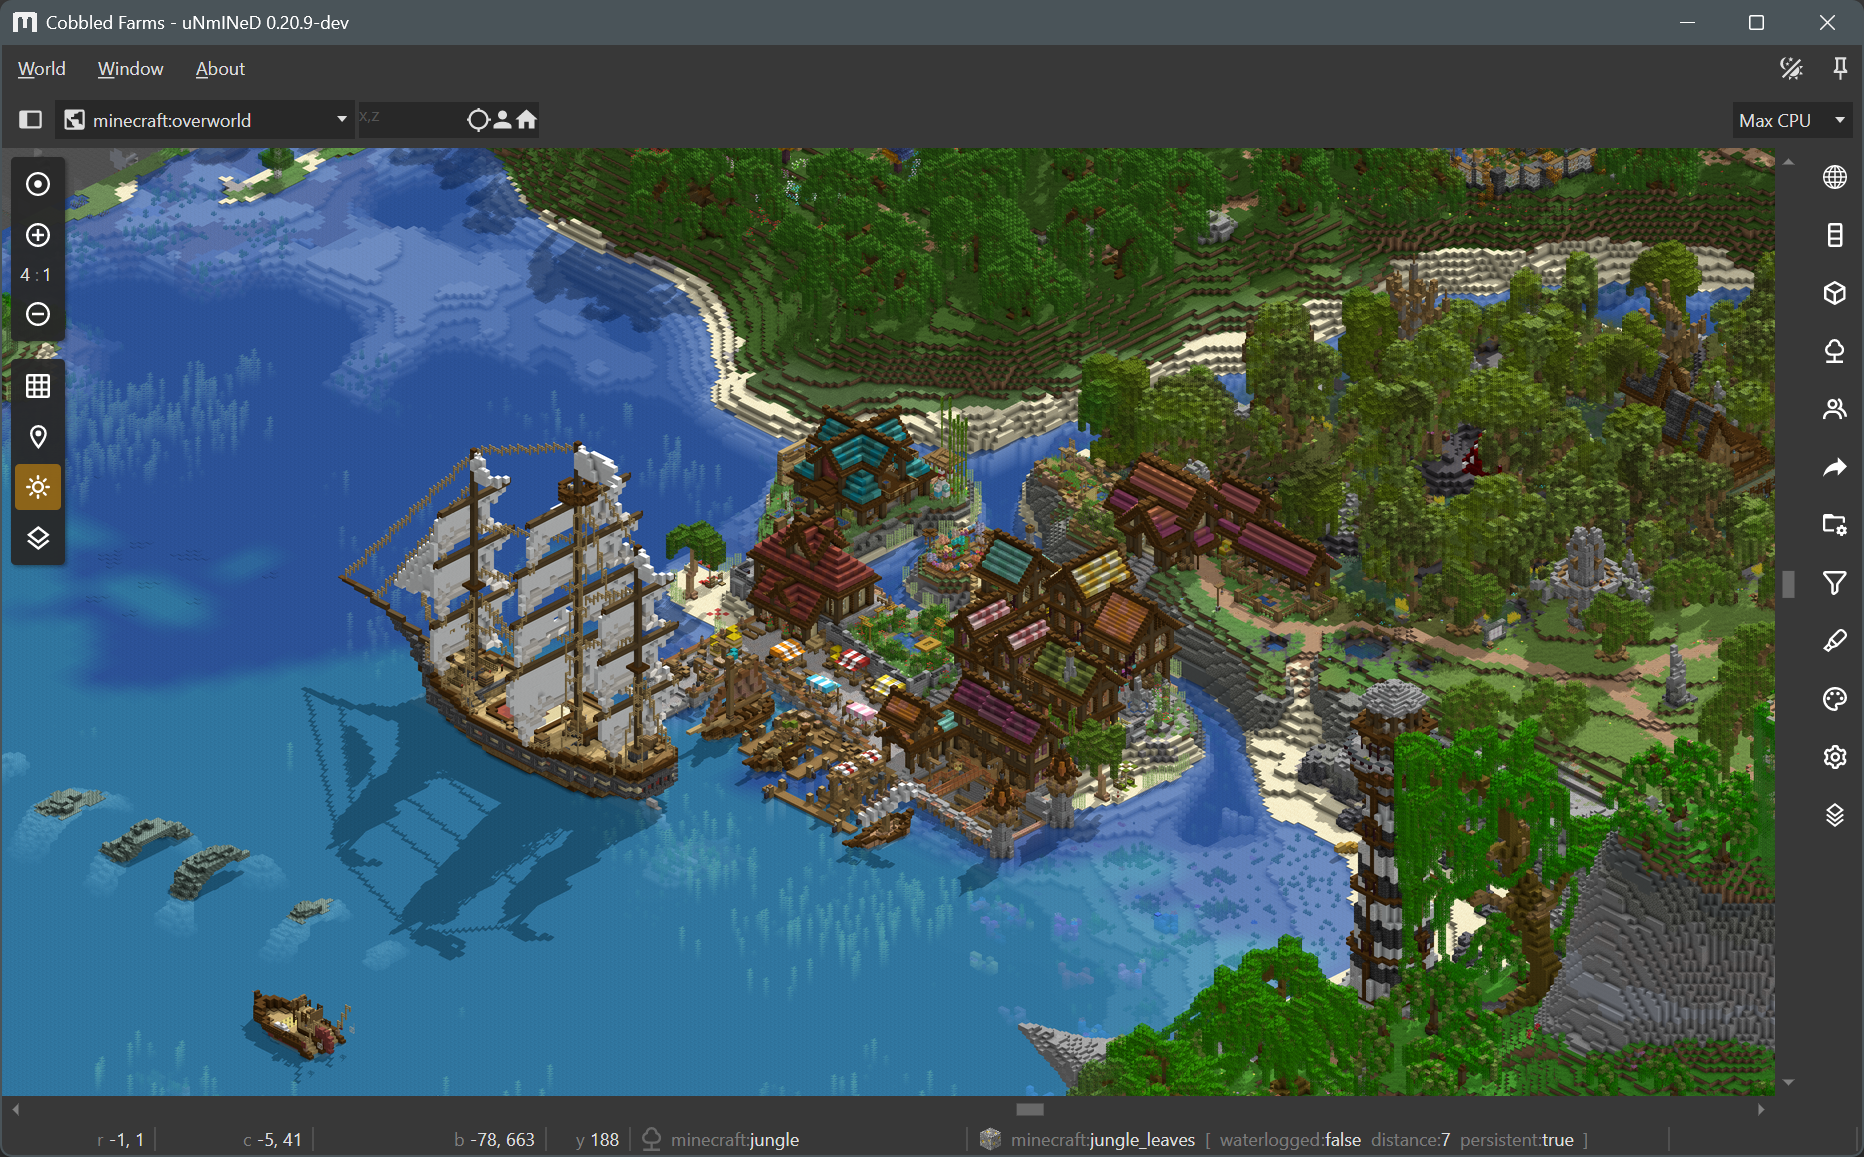
uNmINeD 0.20.9-dev

Door: megasys
17 September 2026 om 20:41

New uNmINeD development snapshot is available for download!

Changes:

  • Fixed 3-digit #rgb color parsing
  • Fixed background color handling in web export
  • Fixed Go to spawn and Go to player buttons for JE 26.x
  • (GUI) Fixed broken highlighter GUI
  • (GUI) Improved sun direction selector
  • (Isometric) Speed (~2x) and memory optimizations
  • (Isometric) Added sunlight shadow casting
  • (Isometric) Added top edge lightening
  • (Isometric) Added block variant randomization
  • (Isometric) Added high precision alpha blending
  • (Isometric) Added a lot of settings
  • (Isometric) Improved water rendering quality
  • (Isometric) Fixed zoom positioning
  • (GUI) Updated ReactiveUI to 24.x
  • Rolled back to .NET 10.x

Sunlight shadows in isometric mode:

  •  

Asterisk Release 24.0.0-rc1

17 September 2026 om 16:59

The Asterisk Development Team would like to announce
release candidate 1 of asterisk-24.0.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/24.0.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 24.0.0-rc1

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-24.0.0-rc1

Links:

Summary:

  • Commits: 37
  • Commit Authors: 20
  • Issues Resolved: 26
  • Security Advisories Resolved: 0

  •  

Asterisk Release 22.12.0-rc1

17 September 2026 om 16:44

The Asterisk Development Team would like to announce
release candidate 1 of asterisk-22.12.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/22.12.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 22.12.0-rc1

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-22.12.0-rc1

Links:

Summary:

  • Commits: 39
  • Commit Authors: 20
  • Issues Resolved: 29
  • Security Advisories Resolved: 0

  •  

Asterisk Release 23.6.0-rc1

17 September 2026 om 16:43

The Asterisk Development Team would like to announce
release candidate 1 of asterisk-23.6.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/23.6.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 23.6.0-rc1

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-23.6.0-rc1

Links:

Summary:

  • Commits: 39
  • Commit Authors: 20
  • Issues Resolved: 29
  • Security Advisories Resolved: 0

  •  

Asterisk Release 20.22.0-rc1

17 September 2026 om 16:42

The Asterisk Development Team would like to announce
release candidate 1 of asterisk-20.22.0.

The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/20.22.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk

Repository: https://github.com/asterisk/asterisk
Tag: 20.22.0-rc1

This release resolves issues reported by the community
and would have not been possible without your participation.

Thank You!

Change Log for Release asterisk-20.22.0-rc1

Links:

Summary:

  • Commits: 40
  • Commit Authors: 20
  • Issues Resolved: 31
  • Security Advisories Resolved: 0

  •  

v4.3.21

15 September 2026 om 14:39

Features

  • Made restart limits opt-in for applications, preview deployments, and service applications. Existing resources that still used the previous limit of 10 restarts were reset to unlimited.

Fixes

  • Hid application names, server names, deployment URLs, team member emails, and job IDs from the Helper deployment check unless detailed output was explicitly requested.

Improvements

  • Updated the supported Traefik patch releases to 3.7.13, 3.6.25, and 2.11.57.

Full Changelog: v4.3.20...v4.3.21

  •  

v4.3.20

15 September 2026 om 09:20

Features

  • Added an All option to the log viewer and accepted lines=all across application, database, and service log APIs. The existing -1 value remained available for compatibility.

Fixes

  • Fixed scheduled backup deletion for service databases so it kept the database context and returned to the correct backup page.
  • Preserved each service component’s stored application or database type when generating Traefik labels.
  • Restored hourly Sentinel version checks for enabled, eligible servers while continuing to exclude build servers.

Improvements

  • Ran Traefik version checks whenever Coolify checked for updates instead of only once a week.
  • Updated Coolify Helper to 1.0.17 and moved the bundled MinIO client to a pinned AIStor release.

Full Changelog: v4.3.19...v4.3.20

  •  

v0.16.22

13 September 2026 om 20:43

[0.16.22] - 2026-09-13

If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.

Added

Changed

Fixed

  • WebDAV: PROPFIND responses do not declare the namespace of every requested property on the DAV:multistatus element.
  • MTA:
    • SMTP session state obtained before STARTTLS is discarded once the TLS handshake completes, as required by RFC 3207.
    • Inbound throttle, outbound throttle and queue quota match expressions evaluate their if/then conditions.
    • DMARC: Messages without an aligned SPF or DKIM pass from a domain that publishes a DMARC policy are reported as fail instead of none in logs.
    • DMARC: A temporary DNS error on an SPF or DKIM check whose identifier aligns with the author domain produces temperror instead of fail.
    • DMARC: A policy record without a p tag is only applied, as p=none, when it contains a rua tag, even if it declares sp or np.
  • iMIP: Notification subjects and bodies omit the event start date, time and timezone for recurring events.
  • OIDC: Discovery is retried for 30 seconds before the directory is marked as unavailable, so a provider that is still starting up no longer requires a restart.
  • WebUI: The cached bundle of an Application is discarded when its resourceUrl changes or the record is deleted, so the next unpack fetches the new resource.
  • DNS: Append . to MX record hostnames.
  • Recovery mode: Automatic IP banning is disabled during recovery and initial setup.
  • FoundationDB: The cached read version is invalidated when a queue refresh or registry change broadcast is received.
  • Sieve: Messages filed with fileinto by a user script are treated as ham and are no longer moved to Junk when classified as spam.
  • IMAP:
    • SELECT, EXAMINE and STATUS on a shared mailbox require the r (read) right.
    • AUTHENTICATE is refused on clear-text connections unless allowPlainTextAuth is enabled, and the greeting and CAPABILITY response advertise LOGINDISABLED instead of the AUTH= mechanisms in that case.
  • IMAP, POP3, ManageSieve: Partial commands received before STARTTLS or STLS are discarded once the TLS handshake completes.
  • Network: Inbound TLS handshakes, both implicit and STARTTLS, are aborted after the listener's tlsTimeout, releasing the connection slot.
  • OAuth: A random key is used when the OIDC provider's encryptionKey or HMAC signatureKey cannot be read, instead of an empty key.
  • LDAP: The {local} and {domain} filter placeholders are escaped.
  • JMAP:
    • CalendarEvent/set stores useDefaultAlerts per user, and CalendarEvent/get returns false when it was never set.
    • CalendarEvent/get returns null for baseEventId unless the id is a synthetic recurrence instance.
    • CalendarEvent/get returns null for requested recurrenceRule and recurrenceOverrides properties on synthetic recurrence instances.
    • CalendarEvent/get and ContactCard/get return only id when the properties argument is an empty list, instead of every property.

Check binary attestation here

  •  

hMailServer 5.7, build 3013

13 September 2026 om 10:34

Features

  • Added DMARC support: incoming messages can now be checked against the sender domain's DMARC policy.
  • Passwords are now stored using Argon2id or PBKDF2, selectable by the administrator.
  • Delivery status notifications (bounces) now include In-Reply-To and References headers, so mail clients thread them together with the original message.
  • The IMAP OnClientLogon event is now fired for clients logging on with AUTHENTICATE PLAIN, not just LOGIN.

Bug fixes

  • Backup and restore now compress and decompress using half of the available processor cores instead of all available.
  • The bundled 7-Zip used for backup and restore was upgraded to 26.03.
  • Fixed: several issues with concurrent access to the same IMAP mailbox from multiple clients.
  • Fixed: an external POP3 fetch account could stay locked after a failed fetch, silently stopping mail collection for that account until the server was restarted.
  • Fixed: a failed DNS lookup was treated as "no records found", which could cause a message to be scored as spam when the HELO host could not be looked up
  • Fixed: the data directory synchronizer could have deleted live message files in public folders when run in delete mode.
  • Fixed: a client could bypass the required HELO/EHLO greeting by sending RSET, or by sending MAIL FROM directly after a STARTTLS handshake

Installation

  • New installations now run the hMailServer service as Network Service, with data and logs stored in C:\ProgramData\hMailServer
  • Fixed: the installer overwrote the ValidLanguages setting, discarding any changes the administrator had made to it.

  •  

v4.3.19

10 September 2026 om 17:50

Breaking Changes (well not breaking, but kinda, not sure haha)

  • Made Sentinel mandatory on regular servers. Existing regular servers were enabled automatically, and the enable or disable setting became read-only in the UI and API. This is mandatory for upcoming features. Sentinel will have a bigger responsibility.

Features

  • Restored each user's last active team after login and added a team picker when no saved team was available. (#11503)
  • Moved service application and database settings into a modal and added Docker restart-limit settings, including API support for max_restart_count.
  • Added indexing, redirect, and hostname regeneration controls to application, preview, and service domain editors.

Fixes

  • Prevented duplicate two-factor challenge submissions and redirected stale authenticated submissions instead of returning HTTP 419. (#11223, closed #10670 and #10731)
  • Accepted custom usernames in SCP-style SSH Git URLs across source setup, API creation, webhooks, clones, and repository links. (#11685, closed #11686)
  • Accepted uppercase letters in existing S3-compatible bucket names. (closed #11536)
  • Detected Docker Compose domain conflicts across service domains and treated HTTP and HTTPS forms as the same routing identity.
  • Preserved inherited service ports instead of saving them as overrides, and ignored hostless URLs when deployments calculated port overrides.
  • Saved Compose environment files atomically to prevent partial writes and truncated files.
  • Made the "Restart Limit Reached" email notification toggle work. (closed #11705)
  • Distinguished same-named application containers on different servers in the terminal.
  • Fixed sidebar preference handling, application domain display, two-factor status display, and duplicate metrics status badges.

Improvements

  • Pulled image-based Docker Compose services before stopping the current deployment, which reduced downtime and stopped deployments early when an image pull failed.
  • Improved domain editing and queued DNS checks across applications, previews, and services. DNS checks now ran only after relevant hostname or scheme changes.
  • Improved mobile application settings navigation, pinned domain save controls, compacted service domain cards, and made view controls consistent.
  • Improved the environment variable editor, modal scrolling, button loading states, and backup settings layouts.
  • Upgraded Sentinel from 0.0.22 to 1.0.1.

What's Changed

  • fix: prevent duplicate 2FA challenge submissions causing HTTP 419 by @PRSFM in #11223
  • feat(teams): persist active team and add team selection screen by @adiologydev in #11503
  • fix: support generic SSH Git usernames by @Marmelatze in #11685

New Contributors

Full Changelog: v4.3.18...v4.3.19

  •  

hMailServer 5.7, build 2843

29 Augustus 2026 om 12:20

Installation

  • Bundle libmariadb.dll with the installation (#479)
  • Support for passing in the password during install (#570)
  • Installer now propagates a non-zero exit code when DBSetup fails

Stability fixes

  • Addressed race conditions during IMAP communication
  • Fixed a file received over SMTP being left open
  • Fixed memory leak when reloading and checking event scripts
  • Upgraded to OpenSSL 3.5.8

Other

  • Documentation refresh

  •  

hMailServer 5.7, build 2788

22 Augustus 2026 om 17:09
  • Experimental support for MariaDB Connector (C). To use, put libmariadb.dll in hMailServer\Bin. hMailServer will prefer it over libmysql.dll if both exists.
  • IMAP improvements
    • Removed the ImapAuthAllowPlainText legacy option
    • Fixed invalid "Recent" count in IMAP notifications
    • Fixed FETCH not honoring the start.size partial-fetch clause
  • DKIM improvements
    • DKIM signatures for domain aliases
    • DKIM-sign all email sent from a domain, not just per-account
    • Fixed signing failure for messages >10MB
    • DKIM verification when the published DNS record is a CNAME
    • Signing for NDR/bounce messages
  • Optional X-Original-Rcpt-To header for incoming mail.
  • IMAP improvements: RFC 6154 support - LIST extension for Special-Use Mailboxes (\Sent, \Drafts, \Junk, \Trash, etc.), including auto-creation of special-use folders on account creation.
  • Security: TLS 1.3 support added
  • Security: OpenSSL upgraded to 3.5.7
  • 64-bit only. Support for x86/32-bit dropped.

  •  

v4.3.18

8 September 2026 om 10:36

Features

  • Added configurable alerts when scheduled database backups missed a set number of days. #11433 closed #11425.
  • Streamed S3-only volume archives directly to S3 so those backups no longer needed temporary local disk space. #11642
  • Added an instance setting for the CDN URL used to serve stored images such as profile avatars and project icons.

Improvements

  • Refreshed the UI with WCAG-compliant contrast, a unified surface system, a full-height settings rail, and a rebuilt mobile navigation drawer. #11659 closed #11532.
  • Preserved in-progress domain edits across refreshes, stacked domain rows on small screens, and moved preview deployment settings onto the Previews page.
  • Paginated service backup history, showed S3 destination details, disabled Backup Now unless the database was running, added search on server resources, and let operators enable Sentinel from its logs page.

Fixes

  • Allowed General application settings to be saved when an existing domain used a wildcard. #11683 closed #11641.
  • Prevented duplicate Coolify Cloud subscription checkouts and recovered subscriptions after missed or out-of-order Stripe webhooks. #11666
  • Preserved PATH in terminal sessions so SSH proxy commands such as cloudflared worked. #11638 closed #11611.
  • Stopped the persistent storage PR suffix dropdown from clipping inside the volumes table. #11637 closed #11605.
  • Returned scheduled task execution duration as a JSON number so the CLI could parse listings. #11636 closed #11616.
  • Persisted S3 storage settings when creating a new volume backup schedule. #11635 closed #11627.
  • Cleaned up preview deployments when a pull request closed after its base branch changed. #11634 closed #11609.
  • Persisted the Make publicly available setting for service databases. #11633 closed #11345.
  • Restored webhook delivery for always-send notifications, including SSL renewal, API token expiry, server force-enable/disable, and Hetzner deletion failures. #11528 closed #11507.
  • Raised nginx request header buffers so large Cookie headers no longer returned HTTP 400 before reaching Coolify. #11404 closed #11403.
  • Kept modal contents intact across Livewire re-renders instead of dropping the body and leaving a click-blocking overlay. #11294
  • Routed Docker Compose domains using each service's ports, stored explicit ports as overrides through the API, and stopped multi-service Compose domains from inheriting the application port.
  • Applied the same domain validation rules to the service API as the UI, including wildcards and oversized URLs.
  • Limited instance public IP DNS hints to the localhost server so remote servers showed their own addresses.
  • Preserved shell negation in sudo-wrapped commands on servers that use a non-root SSH user.
  • Deferred inspection of PostgreSQL custom-format backup archives to pg_restore so valid dumps were not rejected.

What's Changed

New Contributors

Full Changelog: v4.3.17...v4.3.18

  •  
❌