 Log in
Legacy releases
28 September 2026 om 20:32
Archived hMailServer builds, from 4.1.1 to 5.6.9 build 2607. These versions are no longer supported and are kept for reference only. Use the latest release for new installations.


Archived hMailServer builds, from 4.1.1 to 5.6.9 build 2607. These versions are no longer supported and are kept for reference only. Use the latest release for new installations.
If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.
TLSA records are looked up for every MX host, including hosts whose zone is not DNSSEC signed.PushSubscription created within the verification rate limit window of another one on the same account never receives its PushVerification, since the blocked verification is dropped instead of being sent once the window expires.aud claim is derived from a hand-written parse of the push URL, so a crafted push URL can make the server sign a token for a push service other than the one the request is sent to.Email/import rejects a blobId that refers to a Blob/upload creation id in the same request ("#u0") with Invalid blob id..Email/set with a full mailboxIds object identical to the current mailboxes, together with a keyword change, stores the message with IMAP UID 0, so IMAP clients stop seeing it.outboundMta role stops replying to DATA and to JMAP submissions once about 1024 messages have been queued on it.DATA stage Sieve script does not see headers added by milters or MTA hooks, and discards every milter and MTA hook change when it edits the message.DELETE and switch to chunks only after a timeout.COPY and MOVE fail with NO [CONTACTADMIN] when another session changes the same message at the same time.<Encryption>TLS</Encryption>, which Outlook reads as STARTTLS.
The PostgreSQL Global Development Group announces that the fourth beta release of PostgreSQL 19 is now available for download. This release contains PostgreSQL 19 feature previews ahead of general availability, though some details of the release can change during the beta period.
You can find information about all of the PostgreSQL 19 features and changes in the release notes:
https://www.postgresql.org/docs/19/release-19.html
The next planned release of PostgreSQL 19 is the release candidate, which should occur in early October. Based on testing and evaluation, this means that the PostgreSQL 19 GA may also occur in October. More details will be provided as we move closer to these releases.
This beta release reverted several features that were originally planned for PostgreSQL 19. The PostgreSQL community strongly believes that, first and foremost, PostgreSQL must be reliable. Additionally, the community strives for a predictable release schedule. Because of this, the community chose to remove some features from the PostgreSQL 19 release so they can be potentially be included in a later major release after more time working through the community development and review process.
Your testing and feedback help the community ensure that PostgreSQL 19 upholds our standards of delivering a stable, reliable release of the world's most advanced open source relational database. Please read more about our beta testing process and how you can contribute:
https://www.postgresql.org/developer/beta/
To upgrade to PostgreSQL 19 Beta 4 from an earlier version of PostgreSQL,
you will need to use a strategy similar to upgrading between major versions of
PostgreSQL (e.g. pg_upgrade or pg_dump / pg_restore). For more
information, please visit the documentation section on
upgrading.
Fixes and changes in PostgreSQL 19 Beta 4 include:
FOR PORTION OF
clause.ALTER TABLE ... MERGE PARTITIONS and
ALTER TABLE ... SPLIT PARTITIONS.pg_get_role_ddl(), pg_get_tablespace_ddl(), and
pg_get_database_ddl() functions.LC_COLLATE to C in the postmaster process.REPACK command, including crashes, incorrect
behavior with invalid indexes and materialized views, and several permission
and error-reporting corrections.WAIT FOR command, including a deadlock and clearer
reporting of isolation-level errors.FOREIGN_JOIN list in pg_plan_advice.CREATE PUBLICATION ... EXCEPT.COPY FROM SIMD optimization.pgbench --continue-on-error.Please see the release notes for a complete list of new and changed features:
https://www.postgresql.org/docs/19/release-19.html
The stability of each PostgreSQL release greatly depends on you, the community, to test the upcoming version with your workloads and testing tools to find bugs and regressions before the general availability of PostgreSQL 19. As this is a Beta, minor changes to database behaviors, feature details, and APIs are still possible. Your feedback and testing will help determine the final tweaks on the new features, so please test in the near future. The quality of user testing helps determine when we can make a final release.
A list of open issues is publicly available in the PostgreSQL wiki. You can report bugs using this form on the PostgreSQL website:
https://www.postgresql.org/account/submitbug/
This is the fourth beta release of version 19. The PostgreSQL Project is planning to move to the release candidate portion of the release cycle, and will continue to issue release candidates until PostgreSQL 19 is made generally available. For further information please see the Beta Testing page.
If you have corrections or suggestions for this release announcement, please send them to the pgsql-www@lists.postgresql.org public mailing list.
New uNmINeD development snapshot is available for download!
Changes:
If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.
bit_and function.RCPT TO and then rejected at local delivery with 550 5.5.0 Mailbox not found.spf elements per record and the version element of a DMARC aggregate report is written as 1 instead of 1.0.addr-type in Original-Recipient (rfc822;rfc822;user@example.org).TOP msg n counts the n lines from the first byte of the message instead of from the first byte of the body.. is not byte-stuffed.envelope "orcpt" yields the bare address for an ORCPT supplied over SMTP. It now carries the addr-type prefix in every case, as required by RFC 6009._acme-challenge TXT records published for a DNS-01 authorization are never removed.hickory-resolver race that cancels the TCP retry when two nameservers return a truncated response in parallel.email, preferred_username or upn claim are always authenticated against the default directory.failOnTimeout is disabled, so an index whose batches take longer than pollInterval x maxRetries never completes an indexing task and resubmits the same batch indefinitely.Application offline.INCR and EXPIRE as a MULTI/EXEC transaction, whose MOVED redirects collapse into a single EXECABORT that never refreshes the slot map.PING.
General
RTSP
Quantization < 127RTMP
HLS
WebRTC
Dependencies
Binaries are compiled from source code by the Release workflow, which is a fully-visible process that prevents any change or external interference in produced artifacts.
Checksums of binaries are also published in a public blockchain by using GitHub Attestations, and they can be verified by running:
ls mediamtx_* | xargs -L1 gh attestation verify --repo bluenviron/mediamtx
You can verify checksums of binaries by downloading checksums.sha256 and running:
cat checksums.sha256 | grep "$(ls mediamtx_*)" | sha256sum --check
internal: Local Variable: Set value name field, clarifying what is valid input #4467Full Changelog: v5.0.5...v5.0.6
Full Changelog: v4.3.22...v4.3.23
host_path are now rejected.Full Changelog: v4.3.21...v4.3.22
New uNmINeD development snapshot is available for download!
Changes:
Sunlight shadows in isometric mode:
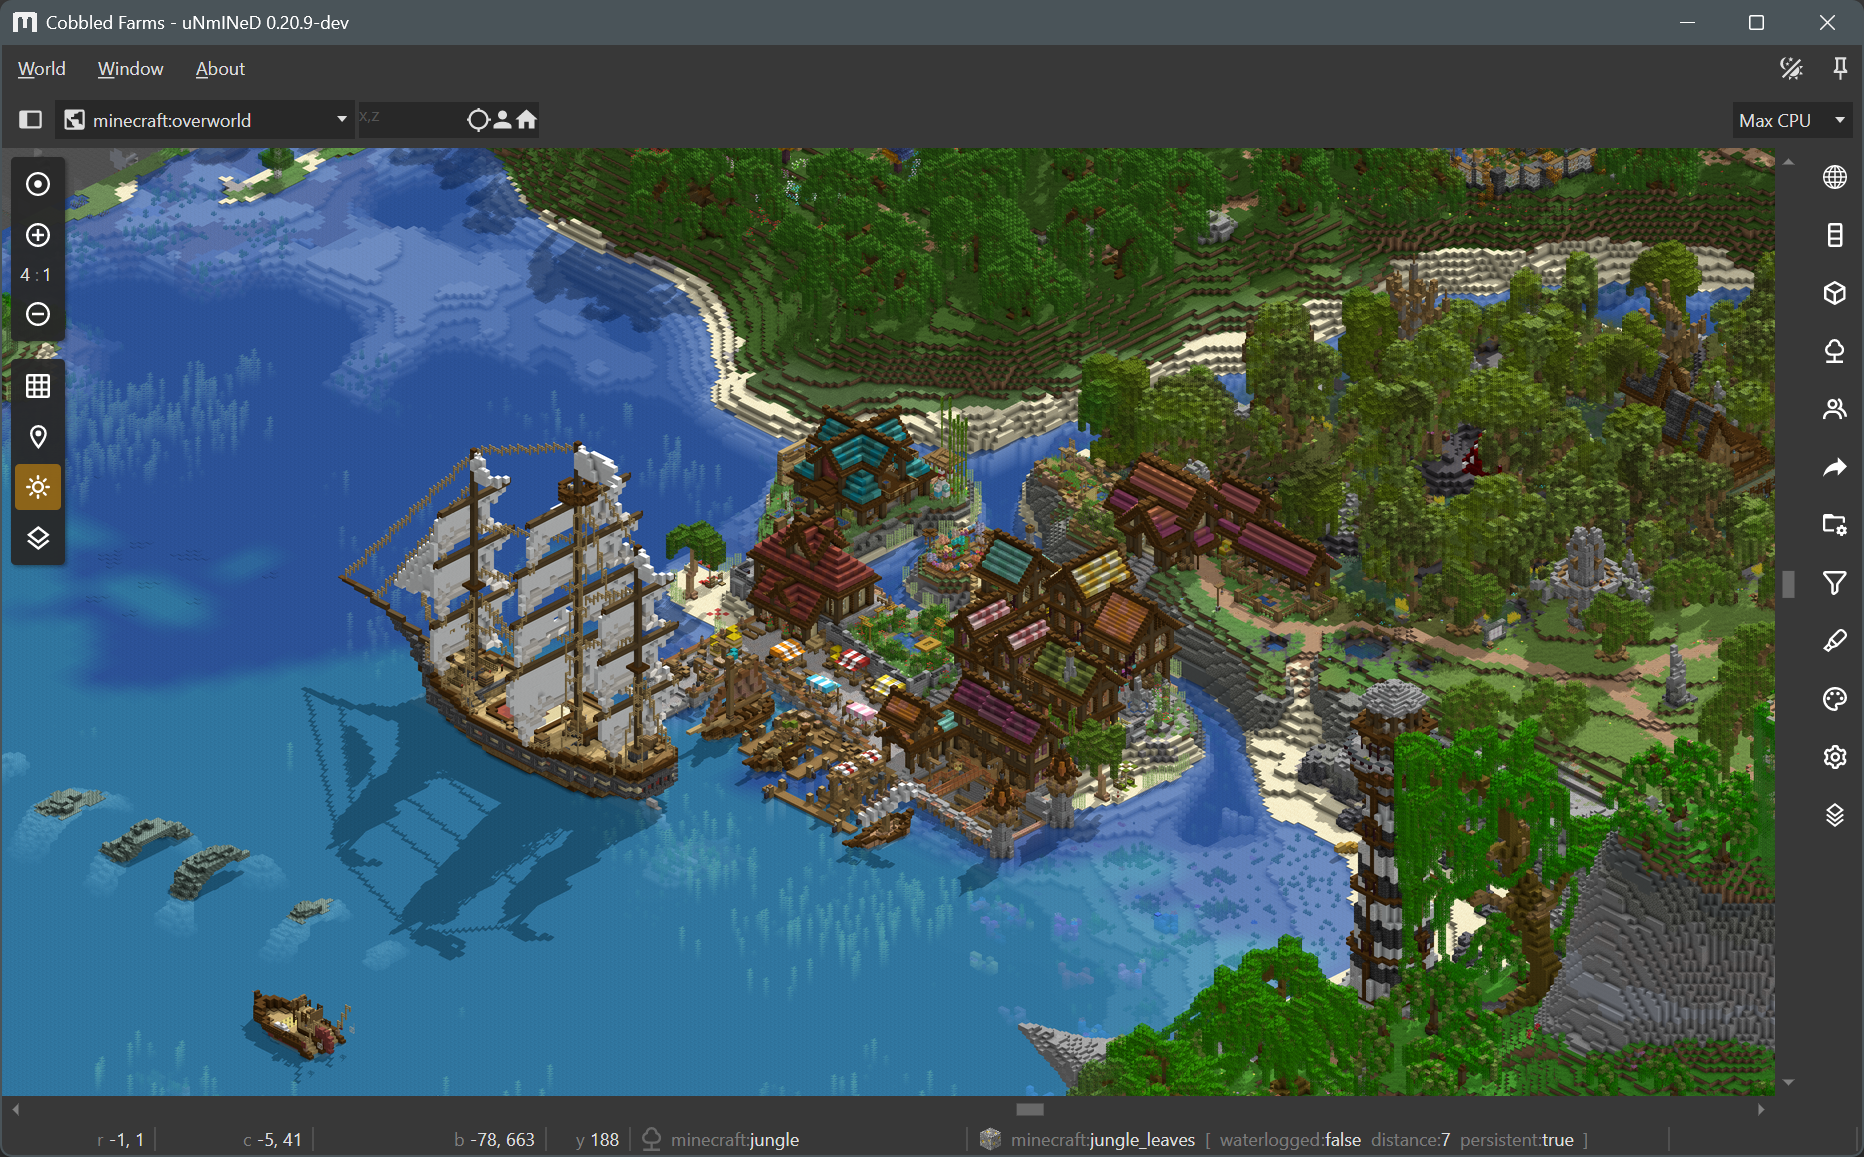
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-24.0.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/24.0.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 24.0.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-22.12.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/22.12.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 22.12.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-23.6.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/23.6.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 23.6.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-20.22.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/20.22.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 20.22.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!

nginx-1.30.5 stable and nginx-1.31.6 mainline versions have been released, with fixes for buffer overflow vulnerability when using ngx_http_v3_module (CVE-2026-90439).
Full Changelog: v4.3.20...v4.3.21
lines=all across application, database, and service log APIs. The existing -1 value remained available for compatibility.Full Changelog: v4.3.19...v4.3.20
If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.
PROPFIND responses do not declare the namespace of every requested property on the DAV:multistatus element.STARTTLS is discarded once the TLS handshake completes, as required by RFC 3207.match expressions evaluate their if/then conditions.fail instead of none in logs.temperror instead of fail.p tag is only applied, as p=none, when it contains a rua tag, even if it declares sp or np.Application is discarded when its resourceUrl changes or the record is deleted, so the next unpack fetches the new resource.. to MX record hostnames.fileinto by a user script are treated as ham and are no longer moved to Junk when classified as spam.SELECT, EXAMINE and STATUS on a shared mailbox require the r (read) right.AUTHENTICATE is refused on clear-text connections unless allowPlainTextAuth is enabled, and the greeting and CAPABILITY response advertise LOGINDISABLED instead of the AUTH= mechanisms in that case.STARTTLS or STLS are discarded once the TLS handshake completes.STARTTLS, are aborted after the listener's tlsTimeout, releasing the connection slot.encryptionKey or HMAC signatureKey cannot be read, instead of an empty key.{local} and {domain} filter placeholders are escaped.CalendarEvent/set stores useDefaultAlerts per user, and CalendarEvent/get returns false when it was never set.CalendarEvent/get returns null for baseEventId unless the id is a synthetic recurrence instance.CalendarEvent/get returns null for requested recurrenceRule and recurrenceOverrides properties on synthetic recurrence instances.CalendarEvent/get and ContactCard/get return only id when the properties argument is an empty list, instead of every property.
Features
Bug fixes
Installation
max_restart_count.Full Changelog: v4.3.18...v4.3.19
Installation
Stability fixes
Other
Full Changelog: v4.3.17...v4.3.18
[An on-line version of this announcement will be available at https://www.postfix.org/announcements/postfix-3.11.7.html]
This release addresses medium-impact problems that need to be fixed as some enable remote DOS or SMTP smugggling.
The fixes below, and more, are also released in the unstable version postfix-3.12-20260902.
In addition to updated releases for the supported Postfix versions 3.8-3.11, releases will also be available for the out-of-support Postfix versions 3.5-3.7. NOTE: these do not include the patches for out-of-support Postfix versions that have been issued for "large SMTP inputs (June 2026)", and for "TLSA parsing (June 2026)". Those patches still need to be applied.
These defects were found by "Qualys assisted by Claude Mythos Preview", and by "OpenAI Security"; three date from 20 or more years ago.
SMTP smuggling:
Bug (introduced: Postfix 3.9, date: 20240106) SMTP smuggling was still possible with smtpd_proxy_filter (disabled by default) when the after-filter SMTP server used the default policy settings "smtpd_forbid_bare_newline_exclusions = $mynetworks" and "smtpd_forbid_bare_newline = normalize". Reported by OpenAI Security. Fix by Wietse.
As suggested by OpenAI Security, eliminate stray CR characters from the smtpd_proxy_filter input stream. The before-proxy-filter SMTP server already eliminated stray LF.
Bug (introduced: Postfix 3.11, date: 20250917): SMTP smuggling was possible with smtpd_proxy_filter (disabled by default) when the before-filter SMTP server added a "Require-TLS-ESMTP: yes" message header, due to implementation edge cases. Adding this header is enabled with the "requiretls_esmtp_header = yes" default setting. Reported by OpenAI Security. Fix by Wietse.
Server crashes and panic()s:
Bug (defect introduced: Postfix 3.0, date: 20140707): null pointer read error after receiving MAIL FROM, RCPT TO, and VRFY with an UTF8 address but no SMTPUTF8 parameter. This requires "smtputf8_enable = yes" (the default) and "strict_smtputf8 = yes" (not default). With this, the SMTP server did an unnecessary MAIL FROM reset without RCPT TO reset. A crafted remote SMTP client could then send a DATA command and crash a Postfix SMTP server process with a null pointer read error. Reported by Wonyoung Jung (정원영).
Other bugs
Bug (defect introduced: Postfix 3.4, date: 20180303): the MySQL client setting "tls_verify_cert = yes" had no effect with Oracle MySQL 8 and later. Report and fix by OpenAI Security.
Bug (defect introduced: Postfix-beta, date: 19990119): the pipe(8) delivery agent deleted a command-line argument if the argument contained $user AND $user expanded to an empty string, breaking the positional order of arguments. This was a workaround for a problem that hopefully no longer exists. Reported by Qualys, assisted by Claude Mythos Preview.
Bug (defect introduced: Postfix 2.3, date: 20050323): the SMTP client enhanced status code parser could process stale data when a remote SMTP server sent a three-digit reply without other text. Reported by Qualys, assisted by Claude Mythos Preview.
TLS
Isolation: stamp Postfix SMTP server TLS session tickets with their master.cf service name. With this, an SMTP server defined in master.cf will no longer accept tickets issued by a different SMTP server defined in the same master.cf file. Fix by OpenAI security.
Configuration safety
The postmap and postalias commands now log a warning when creating a root-owned database file in a directory that is not owned by root. They log that the database source file, indexed file(s), and parent directory should have the same owner, to prevent a privilege-escalation attack. Problem reported by OpenAI Security, remediation strategy (don't break production deployment) by Wietse.
Read after free, memory over-read
Bug (introduced: Postfix 2.3, date: 20060629): a malicious Milter or attacker-in-the-middle could trigger a null-terminated heap memory overread in the SMTP daemon while formatting a malformed multiline response. Fix from OpenAI Security adopted with minor changes.
Bug (defect introduced: Postfix 3.0, date: 20141117): in the postqueue command don't free() text before logging a fatal error message. Reported by Qualys, assisted by Claude Mythos Preview.
Code hygiene: in the SMTP client protocol engine, evaluate a RETURN() macro argument before freeing resources. Reported by Qualys, assisted by Claude Mythos Preview.
Code hardening (defense in depth, prevention)
(Postfix 3.11) Hardening: in the non-BerkeleyDB migration service, delay the decision between running postmap or postalias until after the database file/directory owner/permission checks. The benefit from making the decision early (better error messages) was not worth the risk. Qualys, assisted by Claude Mythos Preview.
(Postfix 3.11) Hardened the database parent directory permission checks for automatic re-indexing with the non-Berkeley-DB migration service.
Hardening command-line email submission: the postdrop command now disallows null and line-break characters in queue file envelope records (line-break characters in non-envelope queue file records are already neutralized by default with "cleanup_replace_stray_cr_lf = yes").
The new constraint not only eliminates line-break injection into local mailbox files as reported by OpenAI Security, but also prevents other forms of misuse. Later, this constraint may be moved into the Postfix core. Fix by Wietse.
Shut up nagging from multiple AIs and harden the virtual delivery agent against an evil (LDAP or SQL) database.
Code hygiene: myrealloc(ptr, 0) still resulted in a panic. Reported by Qualys, assisted by Claude Mythos Preview. Also adopt a mystrndup() fix from Postfix 3.12.
Other:
Portability: OpenBSD does not define NS_INT16SZ. Brad Smith.
You can find the updated Postfix source code on the mirrors listed at https://www.postfix.org/.
If you are upgrading from v0.16.x, replace the binary (or run docker pull). If you are upgrading from v0.15.x and below, please read the upgrading documentation for more information on how to upgrade from previous versions.
SieveUserInterpreter.dkimSignDomain setting, which defaults to the account's own domain.CalendarEvent/set requests that ask for scheduling messages are rejected with a forbidden error when the account cannot send them.Calendar/get and AddressBook/get return every property when the properties argument is omitted or null.ping events advertise the interval in seconds rather than milliseconds.STATUS or FETCH batch receives its tagged completion, instead of the first failing command dropping the responses for all commands queued behind it.DAV:quota-available-bytes.METHOD:REQUEST carrying the RECURRENCE-ID instead of a METHOD:ADD.fileinto :specialuse and specialuse_exists accept special-use attributes in the \Trash form.[::]) fall back to IPv4 when socket creation fails with EPROTONOSUPPORT.
Media-over-QUIC
API
General
alwaysAvailableRecorded parameter that controls whether recording happens during offline periods for always-available paths. When set to false, recording only starts when a real source is connected.API
Media-Over-QUIC
RTSP
RTMP
HLS
WebRTC
RPI Camera
Dependencies
Binaries are compiled from source code by the Release workflow, which is a fully-visible process that prevents any change or external interference in produced artifacts.
Checksums of binaries are also published in a public blockchain by using GitHub Attestations, and they can be verified by running:
ls mediamtx_* | xargs -L1 gh attestation verify --repo bluenviron/mediamtx
You can verify checksums of binaries by downloading checksums.sha256 and running:
cat checksums.sha256 | grep "$(ls mediamtx_*)" | sha256sum --check
