Log in
nginx-1.29.8 mainline version has been released.
6 April 2026 om 23:00
2026-04-07
nginx-1.29.8 mainline version has been released.

nginx-1.29.8 mainline version has been released.
The Asterisk Development Team would like to announce
release candidate 2 of asterisk-23.3.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/23.3.0-rc2
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 23.3.0-rc2
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
Author: nappsoft
Date: 2026-04-02
When the res_cdrel_custom modules is reloaded and the config has not been changed asterisk should not free the old config. Otherwise the connection to the database will be closed and no new connection will be opened.
Resolves: #1852
Author: George Joseph
Date: 2026-03-31
Several issues are resolved:
Internally, floats were used for timestamp values but this could result
in wrapping so they've been changed to doubles.
Historically, the default CEL eventtime format is <seconds>.<microseconds>
with <microseconds> always being 6 digits. This should have continued to be
the case but res_cdrel_custom wasn't checking the dateformat setting in
cel.conf and was defaulting to %F %T. res_cdrel_custom now gets the default
date format from cel.conf, which will be whatever the dateformat parameter
is set to or <seconds>.<microseconds> if not set.
The timeval field formatter for both CDR and CEL wasn't handling custom
strftime format strings correctly. This is now fixed so you should be able
to specifiy custom strftime format strings for the CEL eventtime and CDR
start, answer and end fields. For example: eventtime(%FT%T%z).
Resolves: #1844
Resolves: #1845

The Asterisk Development Team would like to announce
release candidate 2 of asterisk-22.9.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/22.9.0-rc2
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 22.9.0-rc2
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
Author: nappsoft
Date: 2026-04-02
When the res_cdrel_custom modules is reloaded and the config has not been changed asterisk should not free the old config. Otherwise the connection to the database will be closed and no new connection will be opened.
Resolves: #1852
Author: George Joseph
Date: 2026-03-31
Several issues are resolved:
Internally, floats were used for timestamp values but this could result
in wrapping so they've been changed to doubles.
Historically, the default CEL eventtime format is <seconds>.<microseconds>
with <microseconds> always being 6 digits. This should have continued to be
the case but res_cdrel_custom wasn't checking the dateformat setting in
cel.conf and was defaulting to %F %T. res_cdrel_custom now gets the default
date format from cel.conf, which will be whatever the dateformat parameter
is set to or <seconds>.<microseconds> if not set.
The timeval field formatter for both CDR and CEL wasn't handling custom
strftime format strings correctly. This is now fixed so you should be able
to specifiy custom strftime format strings for the CEL eventtime and CDR
start, answer and end fields. For example: eventtime(%FT%T%z).
Resolves: #1844
Resolves: #1845
The Asterisk Development Team would like to announce
release candidate 2 of asterisk-20.19.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/20.19.0-rc2
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 20.19.0-rc2
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
Author: nappsoft
Date: 2026-04-02
When the res_cdrel_custom modules is reloaded and the config has not been changed asterisk should not free the old config. Otherwise the connection to the database will be closed and no new connection will be opened.
Resolves: #1852
Author: George Joseph
Date: 2026-03-31
Several issues are resolved:
Internally, floats were used for timestamp values but this could result
in wrapping so they've been changed to doubles.
Historically, the default CEL eventtime format is <seconds>.<microseconds>
with <microseconds> always being 6 digits. This should have continued to be
the case but res_cdrel_custom wasn't checking the dateformat setting in
cel.conf and was defaulting to %F %T. res_cdrel_custom now gets the default
date format from cel.conf, which will be whatever the dateformat parameter
is set to or <seconds>.<microseconds> if not set.
The timeval field formatter for both CDR and CEL wasn't handling custom
strftime format strings correctly. This is now fixed so you should be able
to specifiy custom strftime format strings for the CEL eventtime and CDR
start, answer and end fields. For example: eventtime(%FT%T%z).
Resolves: #1844
Resolves: #1845
You can install pre-built binaries from https://repo.dovecot.org/
Docker images can be found at https://hub.docker.com/r/dovecot/dovecot
Please review https://doc.dovecot.org/2.4.3/installation/upgrade/2.3-to-2.4.html and https://doc.dovecot.org/2.4.3/installation/installation.html.
There are experimental features in 2.4, one is enabled with --enable-experimental-mail-utf8, and another with --enable-experimental-imap4rev2, and you also need to set mail_utf8_extensions=yes and imap4rev2_enabled=yes to enable them in config.
The Asterisk Development Team would like to announce
the release of Certified asterisk-22.8-cert2.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/certified-22.8-cert2
and
https://downloads.asterisk.org/pub/telephony/certified-asterisk
Repository: https://github.com/asterisk/asterisk
Tag: certified-22.8-cert2
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
Author: Mike Bradeen
Date: 2026-03-25
Address the following pjproject security vulnerabilities
GHSA-j29p-pvh2-pvqp - Buffer overflow in ICE with long username
GHSA-8fj4-fv9f-hjpc - Heap use-after-free in PJSIP presense subscription termination header
GHSA-g88q-c2hm-q7p7 - ICE session use-after-free race conditions
GHSA-x5pq-qrp4-fmrj - Out-of-bounds read in SIP multipart parsing
Resolves: #1833
The Asterisk Development Team would like to announce
the release of Certified asterisk-20.7-cert10.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/certified-20.7-cert10
and
https://downloads.asterisk.org/pub/telephony/certified-asterisk
Repository: https://github.com/asterisk/asterisk
Tag: certified-20.7-cert10
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
Author: Mike Bradeen
Date: 2026-03-24
Address the following pjproject security vulnerabilities
GHSA-j29p-pvh2-pvqp - Buffer overflow in ICE with long username
GHSA-8fj4-fv9f-hjpc - Heap use-after-free in PJSIP presense subscription termination header
GHSA-g88q-c2hm-q7p7 - ICE session use-after-free race conditions
GHSA-x5pq-qrp4-fmrj - Out-of-bounds read in SIP multipart parsing
Resolves: #1833
The Asterisk Development Team would like to announce
the release of asterisk-21.12.2.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/21.12.2
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 21.12.2
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
Author: Mike Bradeen
Date: 2026-03-25
Address the following pjproject security vulnerabilities
GHSA-j29p-pvh2-pvqp - Buffer overflow in ICE with long username
GHSA-8fj4-fv9f-hjpc - Heap use-after-free in PJSIP presense subscription termination header
GHSA-g88q-c2hm-q7p7 - ICE session use-after-free race conditions
GHSA-x5pq-qrp4-fmrj - Out-of-bounds read in SIP multipart parsing
Resolves: #1833
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-22.9.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/22.9.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 22.9.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-23.3.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/23.3.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 23.3.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!
The Asterisk Development Team would like to announce
release candidate 1 of asterisk-20.19.0.
The release artifacts are available for immediate download at
https://github.com/asterisk/asterisk/releases/tag/20.19.0-rc1
and
https://downloads.asterisk.org/pub/telephony/asterisk
Repository: https://github.com/asterisk/asterisk
Tag: 20.19.0-rc1
This release resolves issues reported by the community
and would have not been possible without your participation.
Thank You!

nginx-1.28.3 stable and nginx-1.29.7 mainline versions have been released, with fixes for buffer overflow vulnerability in the ngx_http_dav_module (CVE-2026-27654), buffer overflow vulnerabilities in the ngx_http_mp4_module (CVE-2026-27784, CVE-2026-32647), mail session authentication vulnerabilities (CVE-2026-27651, CVE-2026-28753) and OCSP result bypass vulnerability in stream (CVE-2026-28755). Additionally, nginx-1.29.7 mainline version introduces support for Multipath TCP and upgrades the default proxy HTTP version to HTTP/1.1 with keep-alive enabled.
New uNmINeD development snapshot is available for download!
Changes:
nginx-1.28.3 stable and nginx-1.29.7 mainline versions have been released, with fixes for buffer overflow vulnerability in the ngx_http_dav_module (CVE-2026-27654), buffer overflow vulnerabilities in the ngx_http_mp4_module (CVE-2026-27784, CVE-2026-32647), mail session authentication vulnerabilities (CVE-2026-27651, CVE-2026-28753) and OCSP result bypass vulnerability in stream (CVE-2026-28755). Additionally, nginx-1.29.7 mainline version introduces support for Multipath TCP and upgrades the default HTTP version to HTTP/1.1 with keep-alive enabled.
New uNmINeD development snapshot is available for download!
Changes:
Full Changelog: v4.0.0-beta.469...v4.0.0-beta.470
nginx-1.28.3 stable and nginx-1.29.7 mainline versions have been released, with fixes for buffer overflow vulnerability in the ngx_http_dav_module (CVE-2026-27654), buffer overflow vulnerabilities in the ngx_http_mp4_module (CVE-2026-27784, CVE-2026-32647), mail session authentication vulnerabilities (CVE-2026-27651, CVE-2026-28753) and OCSP result bypass vulnerability in stream (CVE-2026-28755)
We are pleased to announce the availability of a preview of the MariaDB 13.0 series. MariaDB 13.0 is a preview rolling release, published on 23 March 2026, and it continues the work started in 12.3 while adding a solid set of entirely new features. And this one is interesting. This preview release brings a nice […]
MariaDB 13.0 Preview Now Available appeared first on MariaDB.org
Full Changelog: v4.0.0-beta.468...v4.0.0-beta.469
Full Changelog: v4.0.0-beta.467...v4.0.0-beta.468
docker_cleanup parameter to API stop endpoints (#8899, fixes #7758)Full Changelog: v4.0.0-beta.466...v4.0.0-beta.467
Full Changelog: v4.0.0-beta.465...v4.0.0-beta.466
Full Changelog: v4.0.0-beta.464...v4.0.0-beta.465
unofficial support that is why this was not added fasteruuid and pr support@, / and & support to names and descriptionsminWidth and maxWidth propsv4.3.7 instead of latest (solution provided by #8045 author)vite.config.js with the strapi FQDNFull Changelog: v4.0.0-beta.462...v4.0.0-beta.463
dockerfile_location as it is needed for Dockerfile deployments to work properlyis_spa which can be used together with is_staticis_auto_deploy_enabled and is_force_https_enableddocker_compose_domains with conflict checking and force_domain_override supportLOWERCASEUSER as magic variable which are sometimes required e.g. as docker registry usernamedestinationsByServer querynulluuid format from cuid2 parameters in openapi specdocker_compose_raw from post and patch endpoints, as the compose file is sourced from git and should not be manually settable via the apidocker_compose_domains (URLs)docker_compose_domains by validating each array field and verifying which fields are alloweddomains when the build pack is dockercomposedomains in docker_compose_domains are proper URLs and include a valid scheme (http or https)docker_compose_domains in domain conflict check via Application::ownedByCurrentTeamAPIis_static and connect_to_docker_network fields where not updating on some endpointsfqdn column which allows to remove all URLs from the domains fieldtype and docker_compose_raw is filled show an errortype is not valid show an error with all valid service typesASCII to UTF-8 to allow special characters, emojis and moreAPP_NAME env in development
APP_NAME for development might seem like a good idea but it is annoying and causes issues when debugging, especially with Redis as it is used as the key prefix/settings for root user on cloud instanceAlready registered? button from the /register page when there are 0 users as clicking on it would just redirect you back to /registerdomains update code from services endpointsdomains) validation
fqdn to urls as that is what it actually isdocker_compose_raw description more clear.env file in development to not expose all ENVs in deployment logsvariables section in development to not expose all ENVs in deployment logsFull Changelog: v4.0.0-beta.460...v4.0.0-beta.461
Optimize queries, views with caches and prevent N+1 queries.
tldr: some views are faster
Full Changelog: v4.0.0-beta.459...v4.0.0-beta.460
Full Changelog: v4.2.5...v4.2.6
New uNmINeD development snapshot is available for download!
Changes:
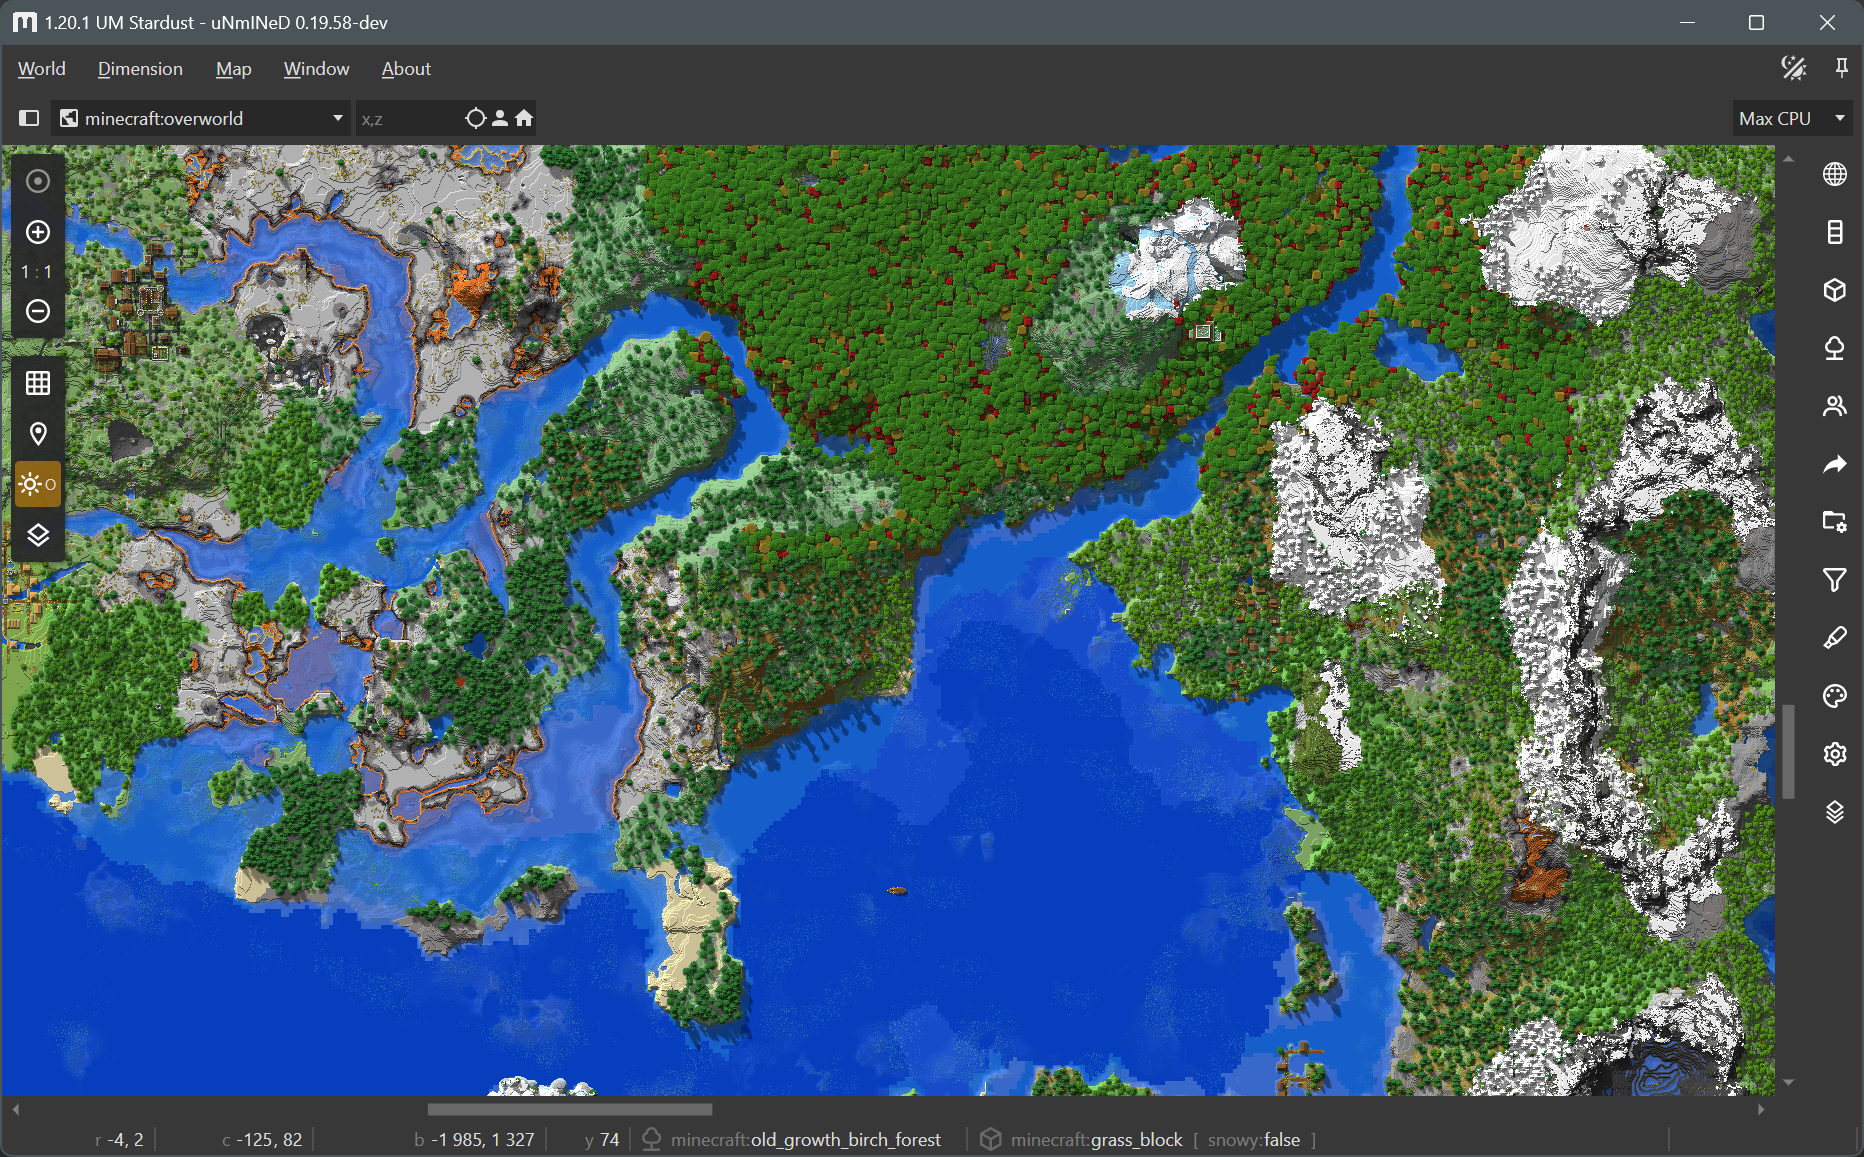
uNmINeD now can read biome and block metadata from datapacks/mods and behavior/resource packs, and it calculates map colors for custom blocks automatically by averaging their textures instead of displaying them as pink.
By default, uNmINeD displays each block as a square filled with a single color. When textured rendering is enabled, it still does not render blocks in 3D, instead it fills the squares with an image (the in-game texture of a block) rather than a solid color.
Textured rendering can be enabled on the render settings side panel (the tab with a cog wheel icon). It works for zoom-in levels 4:1 or higher. It works well with cube-like blocks, but fences, walls and other blocks with a complex 3D model look off. Upcoming releases will be able to render fences and walls correctly, and images to be used for complex blocks will be customizable.
Using textures or datapacks/mods with Java Edition worlds requires a Minecraft client JAR file. If you have Minecraft installed, uNmINeD will automatically find your client JAR file, otherwise you have to copy it from another machine, and select it in uNmINeD’s app settings.
Using textures or behavior packs with Bedrock Edition worlds requires a vanilla resource pack. You can download it from Mojang: https://github.com/Mojang/bedrock-samples/releases. Find your version (or use the latest), click on Assets, and download the full package named bedrock-samples-xxxxx-full.zip (or the source code zip package, either one is good), then select the downloaded file in uNmINeD’s app settings.
Use --java-client-jar=/path/to/1.21.11.jar to select your Minecraft client JAR.
Use --bedrock-vanilla-pack=/path/to/bedrock-samples-v1.26.0.2-full.zip to select your vanilla resource pack.
Use --textures=true for textured rendering (effective at zoom-in levels 4:1 or higher).
Selecting a client JAR or a vanilla resource pack is required for all datapack related functions, including automatic color calculation for custom blocks and textured rendering.
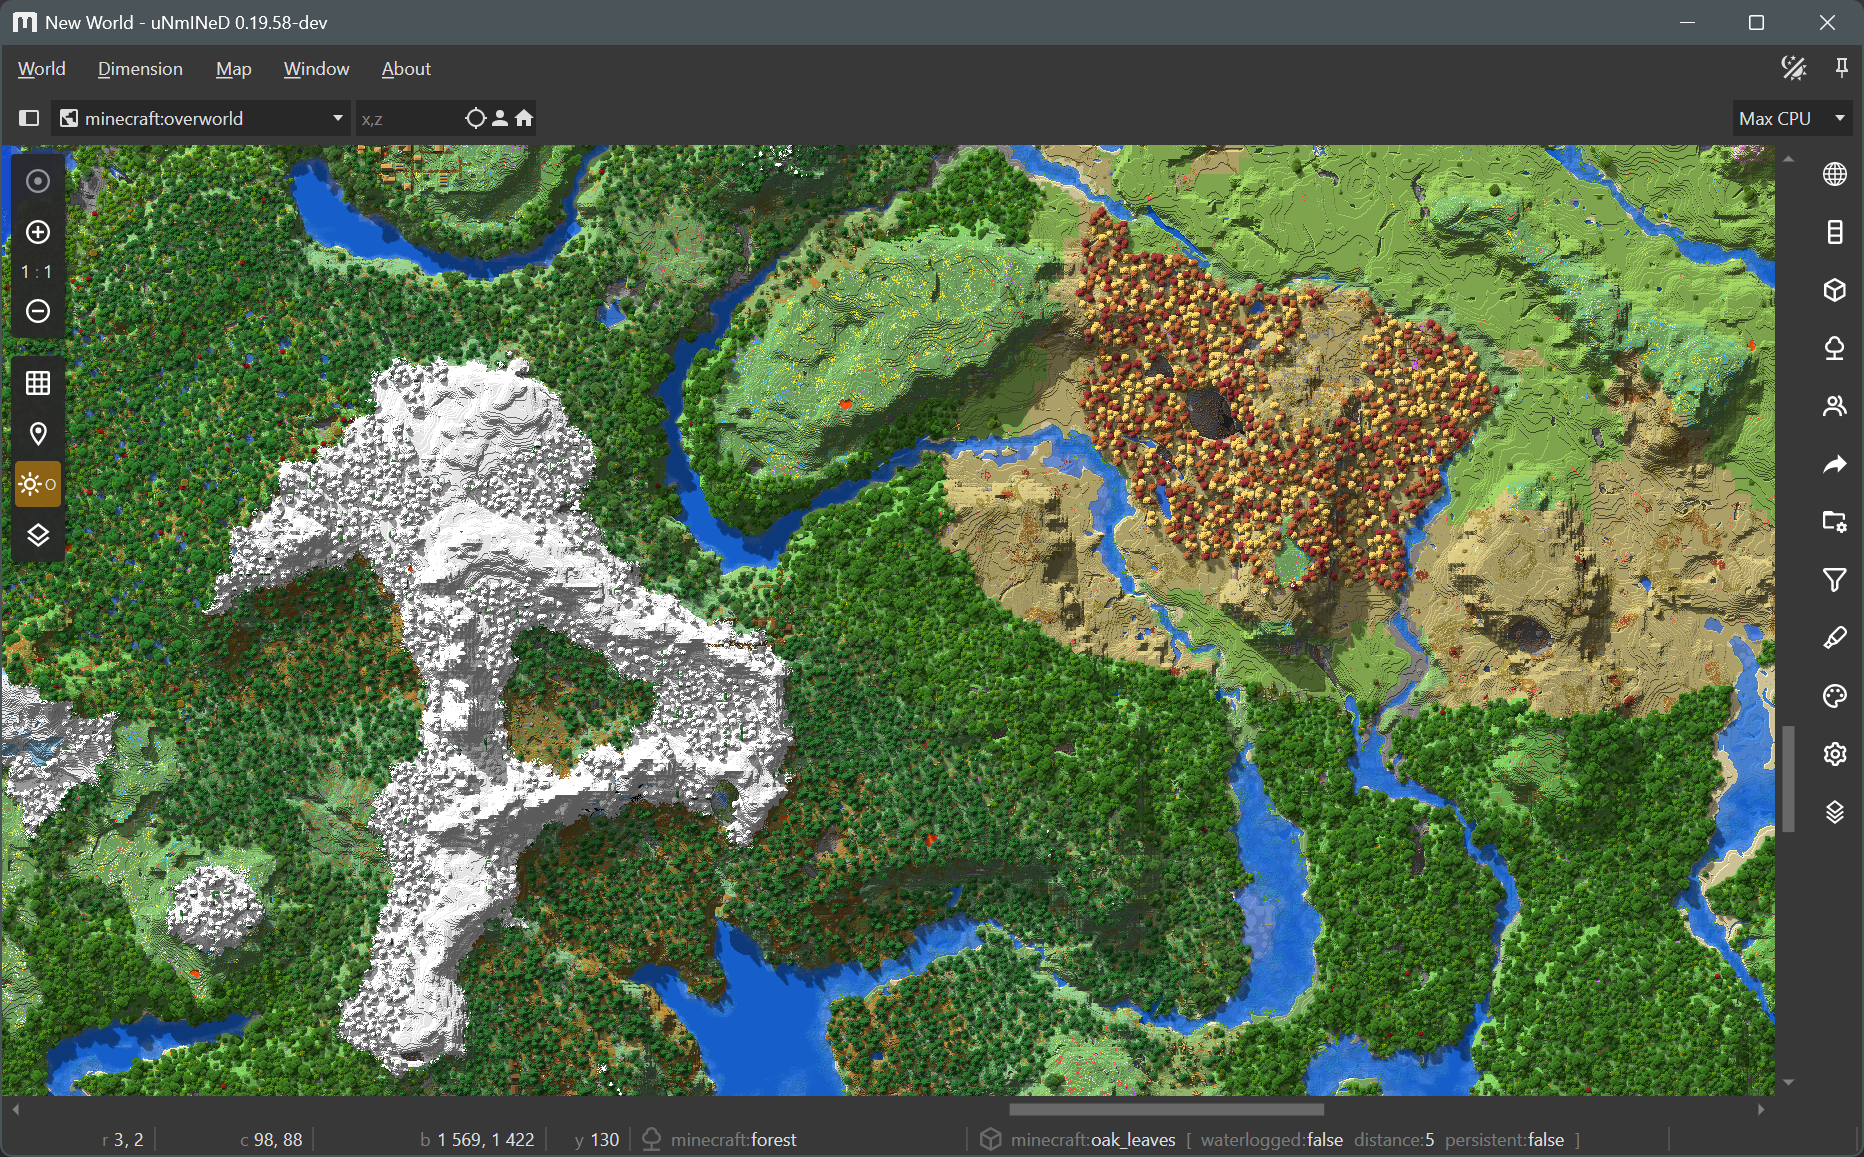
Oh The Biomes We’ve Gone:
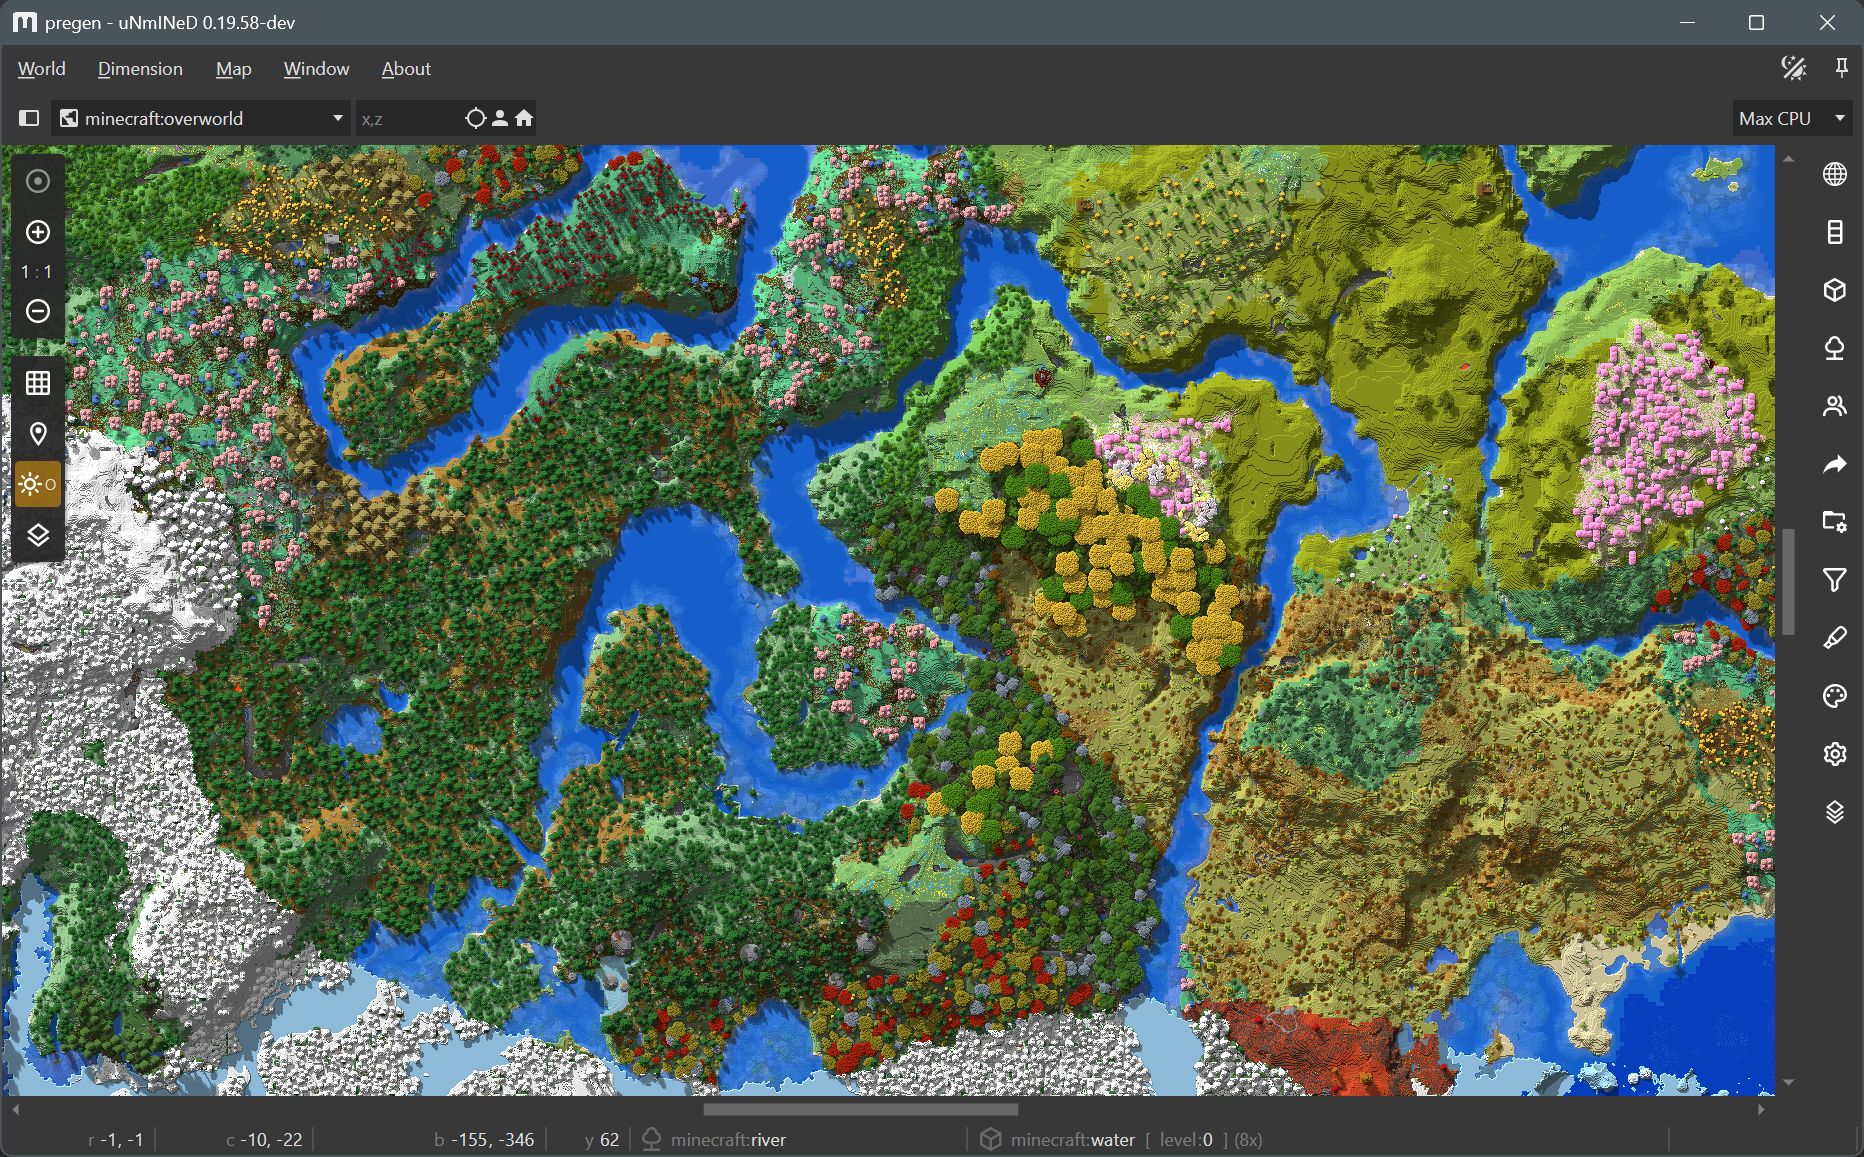
Biomes O’Plenty:
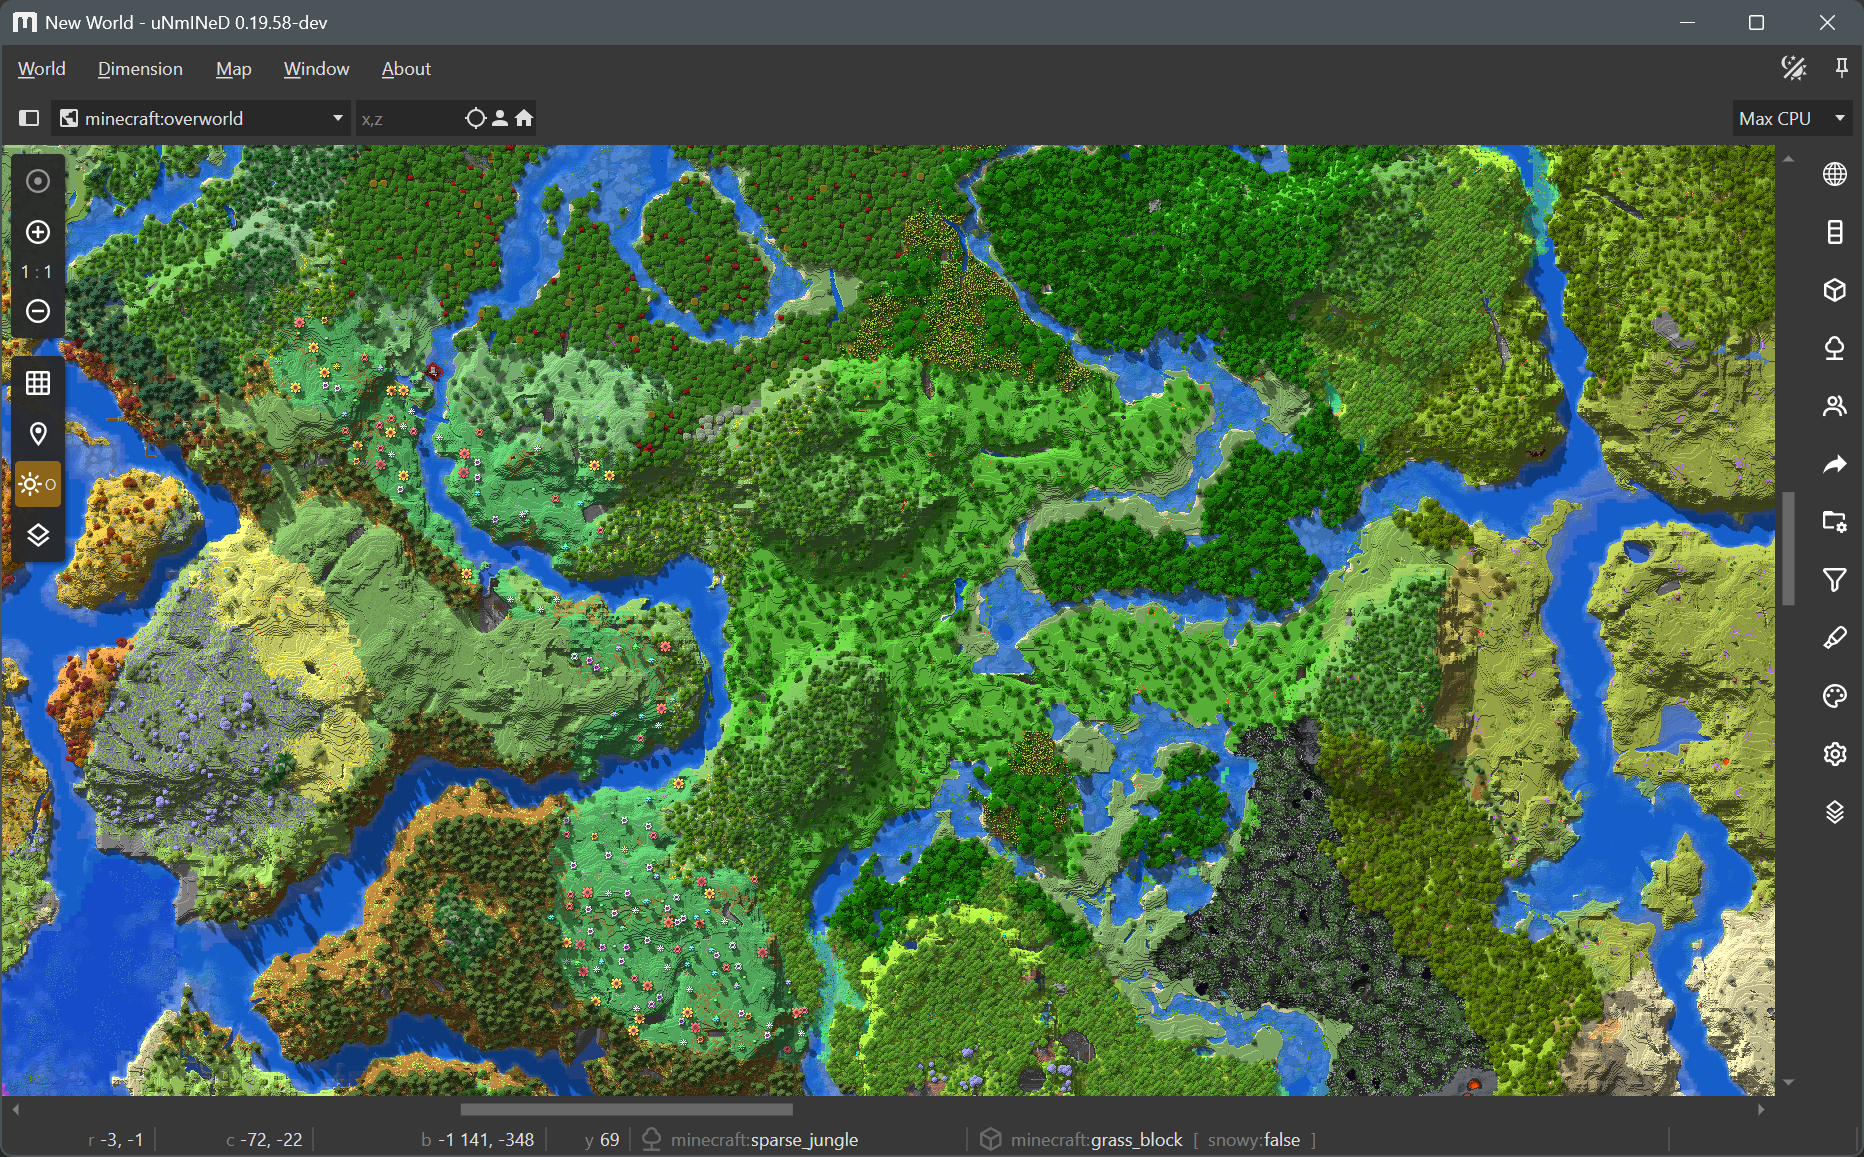
Regions Unexplored:
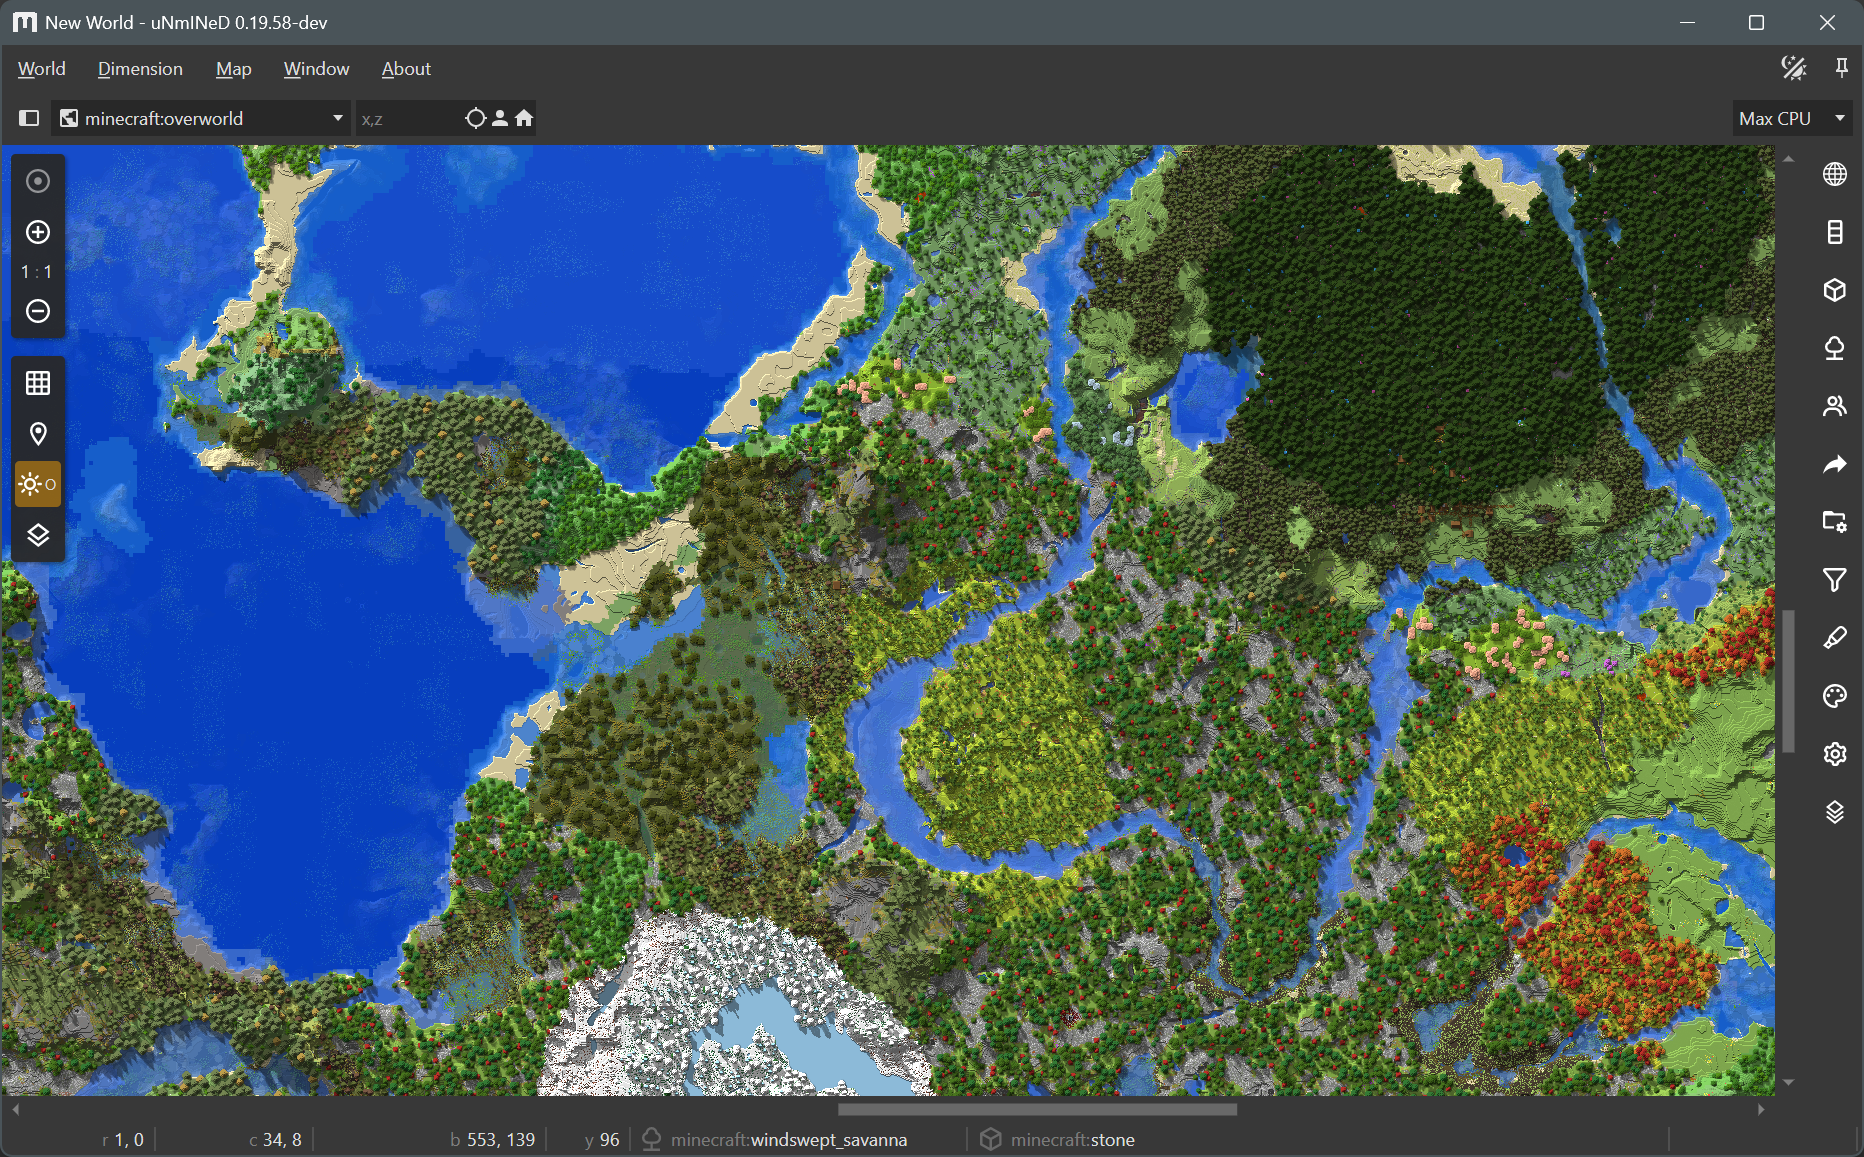
Terralith:
Wilder Wild: